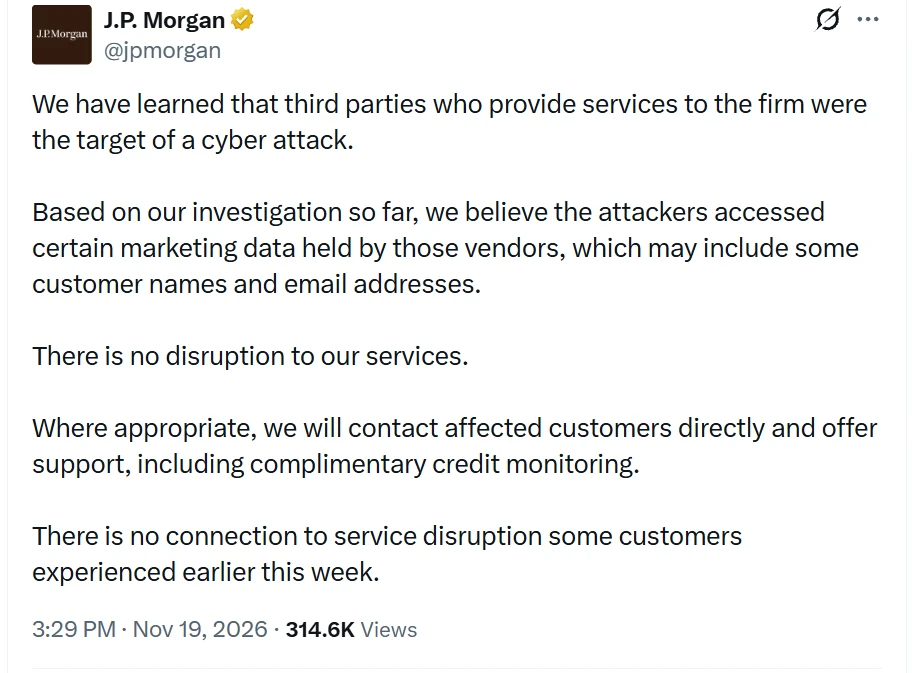
J.P. Morgan Chase disclosed a data breach stemming from a cyberattack targeting external service providers, which resulted in the exposure of customer personal information and marketing data. The bank clarified that its own operations were not disrupted and that the incident is separate from an unrelated service outage that occurred earlier in the same week.
In an announcement posted to X, Chase stated: "We have learned that third parties who provide services to the firm were the target of a cyber attack." The bank added: "Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses."

As the largest U.S. bank by assets with approximately $4.1 trillion in holdings as of June 2026, J.P. Morgan Chase serves roughly 78 million active digital customers through its consumer banking operations.
Both Visa and Mastercard issued separate statements confirming involvement in third-party incidents, though neither has disclosed direct customer impact. Operating across more than 200 countries, these payment networks collectively process annual transaction volumes measured in the trillions of dollars.
A Visa spokesperson told BleepingComputer: "Visa is aware of these claims. They are associated with an incident involving a third-party service provider in Asia Pacific. Visa's systems were not involved and were not impacted. No payments data such as card numbers were affected. This is unrelated to any of the system disruptions across different industries this past week."
Mastercard reported to BleepingComputer that it "were recently informed of an incident at a third-party provider that resulted in the exposure of limited amount of email addresses – non-payments information – from a small subset of cardholders enrolled in a specific benefit program." A Mastercard representative stated: "There is no impact to the Mastercard payment network or the ability for people to use their cards. At this time, the exposure has been contained and our teams are working with the provider to support the impacted cardholders as needed."
n0n ransomware group claims responsibility
On November 11, 2026, the n0n ransomware group claimed credit for the attack, identifying Qubole as the likely third-party provider. Qubole, owned by Idera, operates as a cloud data analytics platform offering automated processing, real-time analysis, and reporting capabilities.
Between October 14 and 26, 2026, attackers leveraged compromised Qubole credentials to infiltrate customer AWS environments by exploiting IAM roles that had been configured to permit Qubole access. The group claimed to have extracted 53.9 GB of data spanning 30,743 files directly from Qubole's systems, encompassing customer contracts, pricing information, employee records, trial user data, and production information.
The attackers also alleged possession of nearly one petabyte of data obtained from Qubole customer networks. On November 16, 2026, n0n published the purported Chase, Visa, and Mastercard data on its extortion website.
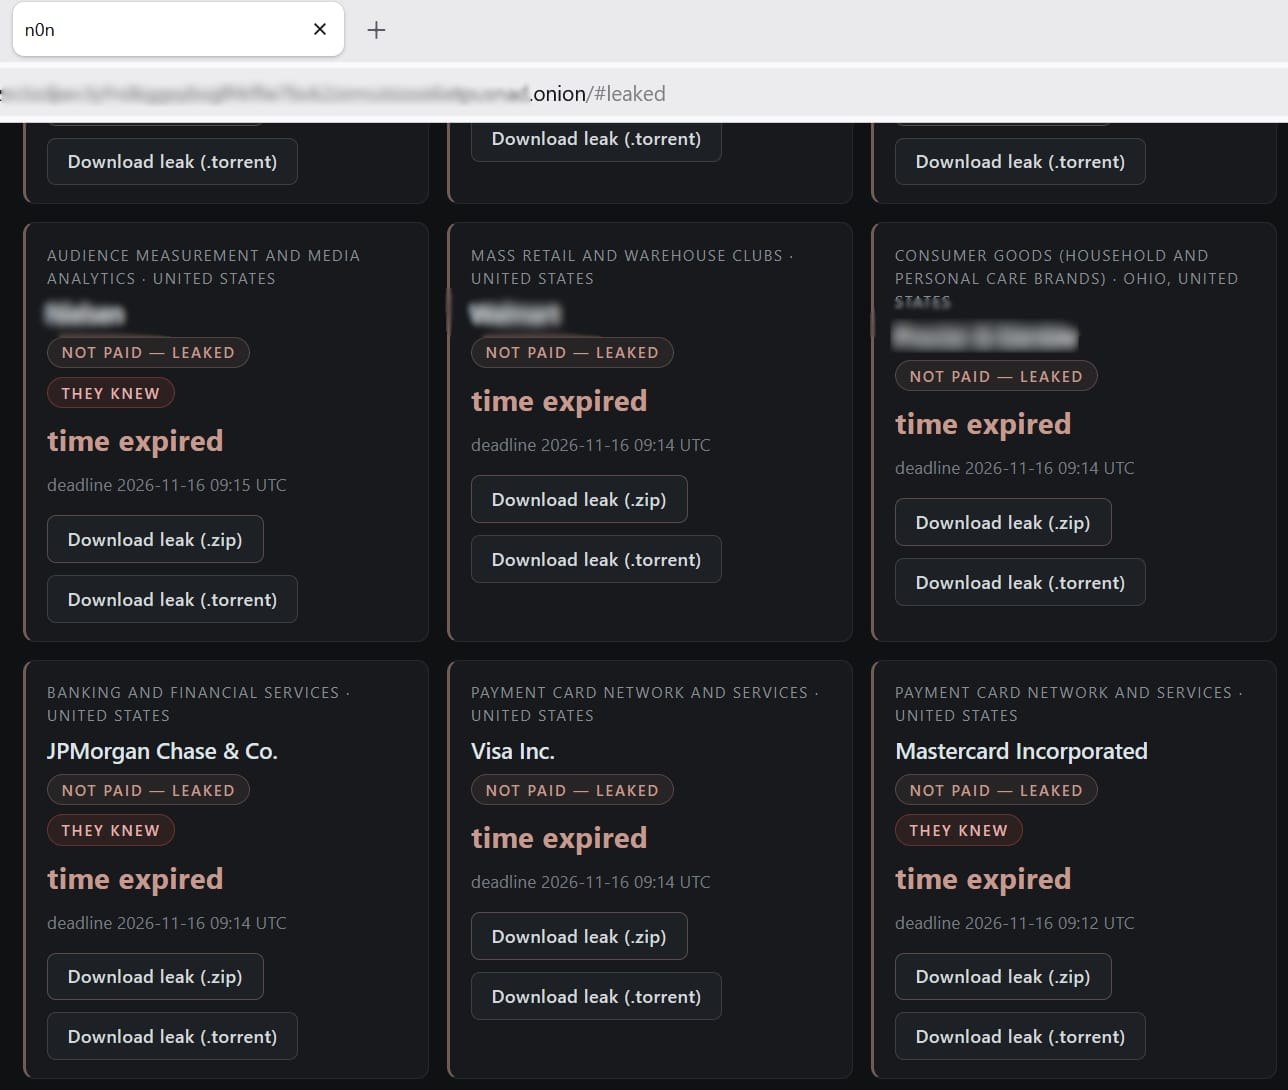
According to the hacking group, it had contacted Qubole and certain affected companies prior to public disclosures by security firms Sentra and Wiz, but its extortion demands went unanswered. Qubole did not respond to BleepingComputer's request for comment regarding the threat actors' claims at the time of publication.