Synology has alerted customers to apply updates immediately following a wave of C3RB3R ransomware infections targeting its network-attached storage devices. The Taiwanese vendor is pushing users to enable automatic patching and deploy the latest version of DiskStation Manager (DSM) software across their NAS infrastructure.
In a Thursday advisory, the company stated: "Synology has identified threat actors exploiting a vulnerability patched in December 2024 to target devices running outdated versions of DSM. These attacks aim to encrypt data and extort ransom." The firm added that it "strongly urges all users running vulnerable versions to update DSM immediately to protect their systems. Synology also recommends enabling automatic updates to keep DSM up to date at all times."
Synology has not yet disclosed which specific vulnerability is being leveraged in the current campaign, though the company referenced a November 2024 security advisory covering patches for three flaws: CVE-2024-10441 (arbitrary code execution), CVE-2024-50629 (file read), and CVE-2024-10445 (file write).
Affected users should immediately restrict external access to the management interface and apply one of the following DSM versions or newer:
- 7.2.2-72806-1 or above
- 7.2.1-69057-6 or above
- 7.2-64570-4 or above
- 7.1.1-42962-7 or above
- 6.2.4-25556-8 or above
This represents a rare security warning from Synology; the vendor's previous customer alert came in August 2019 following widespread brute-force attacks that resulted in eCh0raix ransomware infections.
Attack details and ransom demands
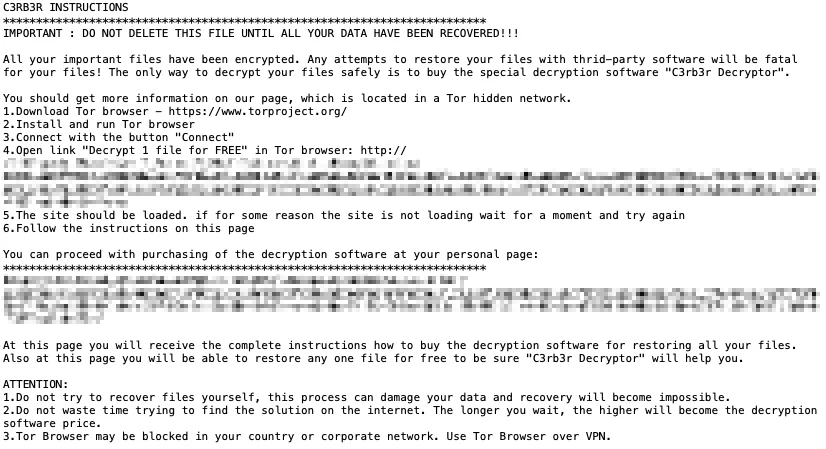
Reports of C3RB3R infections began surfacing more than two weeks ago, with victims discovering encrypted files bearing the .L0CK3D extension and ransom notes named read-me3.txt. Attackers are demanding thousands of dollars for the "C3rb3r Decryptor" tool, accessible through a dark web portal.
The ransom message warns: "All your important files have been encrypted. Any attempts to restore your files with thrid-party software will be fatal for your files! The only way to decrypt your files safely is to buy the special decryption software 'C3rb3r Decryptor'. At this page you will receive the complete instructions how to buy the decryption software for restoring all your files. Also at this page you will be able to restore any one file for free to be sure 'C3rb3r Decryptor' will help you."
History of the C3RB3R malware
The C3RB3R variant (also tracked as CerberImposter) takes its name from a notorious Ransomware-as-a-Service operation that launched in 2016. The original Cerber campaign dominated the threat landscape before ceasing operations at the end of 2019, accounting for over 80% of ransomware attacks and roughly a quarter of all ransomware infections on enterprise systems.
The modern C3RB3R strain first appeared in December 2021 and has since been deployed against Atlassian Confluence and GitLab infrastructure, exploiting remote code execution vulnerabilities (CVE-2021-26084 and CVE-2021-22205) and authentication bypass flaws (CVE-2023-22518).
Security monitoring firm Shadowserver currently tracks more than 380,000 Synology NAS devices exposed to the internet, though the organization does not disclose how many have been patched or whether any are honeypots.