Two newly patched flaws in Ivanti's Connect Secure (ICS) remote access gateway have been under active exploitation as part of coordinated attack chains since at least October 1. The vulnerabilities, designated CVE-2026-111357 and CVE-2026-118527, were deployed by threat actors in combination with an authentication bypass flaw (CVE-2026-104935) that Ivanti addressed in October to neutralize the primary attack vector.
CVE-2026-111357 carries high severity and enables privilege escalation, while CVE-2026-118527 permits authenticated attackers to upload files to unpatched systems. When Ivanti initially released patches for CVE-2026-104935 last month, the company advised administrators to apply updates urgently due to documented exploitation activity in the field.
Ivanti explained its patching approach in a Thursday advisory update: "At the time of discovery of exploitation, Ivanti had a fix developed for CVE-2026-104935 which was already in QA for supported versions, and we made the decision to not delay getting a fix to customers that resolved the primary exploitation path when the LPE was discovered." The company added, "Because of this, our focus was initially centered on the disclosure of CVE-2026-104935 and providing protection for our customers as quickly as possible."
Attack campaign details
Security researchers at Volexity, who discovered the flaw, documented that a threat actor tracked as UTA0576 had been chaining CVE-2026-104935 with two additional vulnerabilities since at least October 3 to achieve unauthenticated root-level code execution on fully patched ICS devices. According to Volexity's analysis, "Notably, UTA0576 deployed no malware or web shell. Instead, the threat actor re-exploited the device for every command it ran and tampered with logs to cover its tracks, evading Ivanti's Integrity Checker Tool."
Threat intelligence firm Defused independently verified Volexity's findings, identifying the initial signs of active CVE-2026-104935 exploitation beginning October 1.
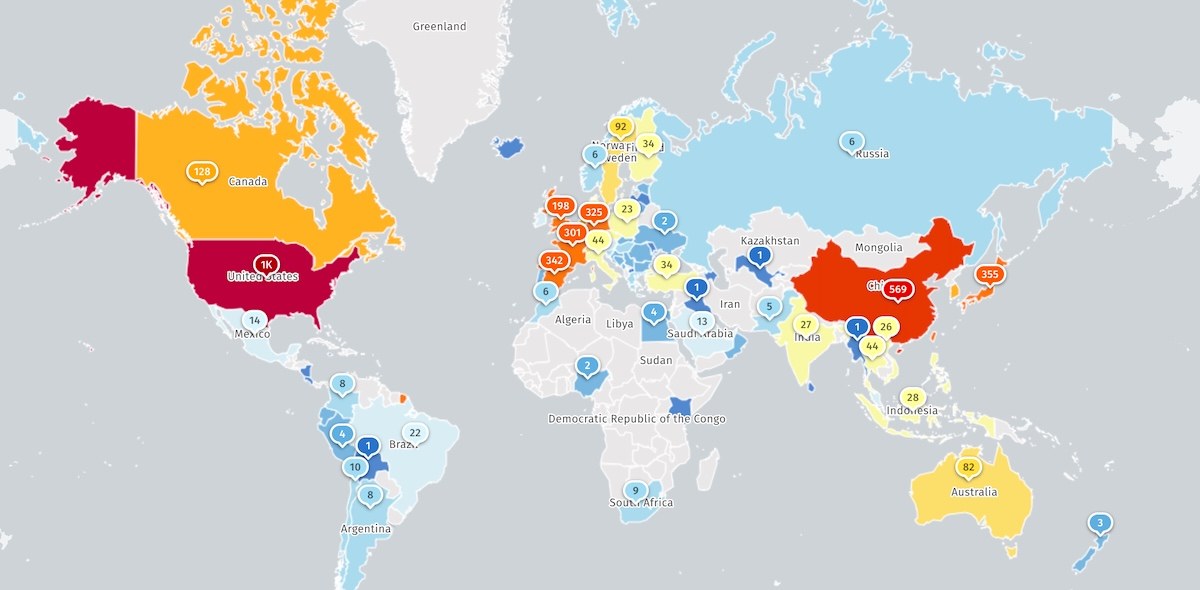
On Tuesday, the US Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-104935 to its list of actively exploited vulnerabilities and directed federal agencies to deploy patches by Friday. Internet threat monitoring service Shadowserver has identified more than 5,000 Internet-exposed ICS instances, though data on how many organizations have already mitigated the vulnerability remains unavailable.
Broader vulnerability history
Ivanti's Connect Secure platform has become a frequent target for zero-day exploitation campaigns, as vulnerabilities in the gateway provide rapid access to enterprise networks for data theft operations. The company has patched numerous Connect Secure zero-days over recent years, many of which attackers chained together in widespread campaigns to distribute malware.
In early January 2024, Ivanti released fixes for a command injection flaw (CVE-2024-21887) and an authentication bypass (CVE-2023-46805), followed two weeks later by a patch for a server-side request forgery vulnerability (CVE-2024-21893). More recently, the company addressed a remote code execution bug (CVE-2025-0282) in January 2025 and a second RCE vulnerability (CVE-2025-22457) that state-sponsored hackers linked to China have exploited since at least mid-March 2025.
Ivanti operates with approximately 3,000 employees, maintains partnerships with over 7,000 resellers, and serves more than 40,000 customers globally through its IT asset management offerings. Since November 2021, CISA has designated 38 Ivanti vulnerabilities as actively exploited in the wild, with 12 of those also appearing in ransomware attacks.