Shift Up, the South Korean developer behind Goddess of Victory: NIKKE, disclosed that threat actors had compromised the game's PC launcher through a supply-chain attack. The intrusion resulted in distribution of malware designed to exfiltrate user credentials and cryptocurrency wallet information. On November 4 at 02:30 (UTC +9), the studio released a client update to remediate the compromise.
We have identified an issue indicating that the PC Launcher's script files may have been tampered with by a third party. Accordingly, client fixes and an update were implemented on November 4 at approximately 02:30 (UTC+9). We are currently investigating the scope of the impact caused by this issue, and we will provide further details regarding follow-up measures in a separate notice.
Shift Up's statement on X
Goddess of Victory: NIKKE is a sci-fi shooter RPG available on Windows, iOS, and Android. Its publisher, Level Infinite, reported that the title has accumulated more than 45 million downloads since its 2022 launch, with Google Play alone accounting for 10 million installations.
Malicious launcher scripts delivered backdoor
While Level Infinite has withheld specifics, independent security researcher MotherSphere published findings on GitHub indicating that four JavaScript files hosted on Level Infinite's content delivery network had been altered. According to the researcher's analysis, these files were modified on September 27, 2026, to inject malicious JavaScript that would download additional code from attacker-controlled infrastructure each time a player launched the game.
The injected code remained concealed within legitimate JavaScript and employed obfuscation techniques to mask the domains insightjs[.]com and insightjs[.]org, from which the malicious payloads originated. BleepingComputer verified that two of the altered JavaScript files contained an obfuscated loader capable of retrieving and executing code from these domains, with failover capability to the secondary domain if the primary was unreachable.
MotherSphere's investigation revealed that the downloaded code leveraged the launcher's built-in capabilities to fetch and execute a malicious LuaJIT payload designated insight.bundle, which deployed a remote-access agent identified as K2F. This backdoor enabled attackers to execute arbitrary commands, enumerate and exfiltrate local files, capture screen content, harvest NIKKE account login details, and extract data cached in web browsers.
The malware included functionality to deploy an additional malicious Windows DLL named platform_experience_helper.dll that could persist on infected systems even after the game launcher was terminated. Analysis of a DLL sample submitted to VirusTotal revealed code capable of harvesting cryptocurrency wallet information from browser extensions, including MetaMask, Phantom, and Coinbase Wallet.
The DLL possessed the capability to intercept sensitive wallet data such as recovery phrases and private keys, potentially granting attackers access to cryptocurrency holdings. Nevertheless, it remains unclear whether the attackers deployed this component across infected machines or successfully conducted any cryptocurrency theft.
MotherSphere documented that Level Infinite replaced three of the compromised JavaScript files on November 3 with unmodified versions. However, the researcher indicated that a compromised instance of the fourth file continued to be distributed to users as of 22:26 GMT, suggesting that at least one malicious script remained accessible following the company's client update deployment.
The researcher published indicators of compromise that users can reference to verify whether the malicious Lua agent executed on their systems. The presence of the string k2f_chan in the Launcher/intl_service/debug.log file within the NIKKE installation directory indicates the malicious Lua agent ran, though this does not establish whether the DLL was also loaded.
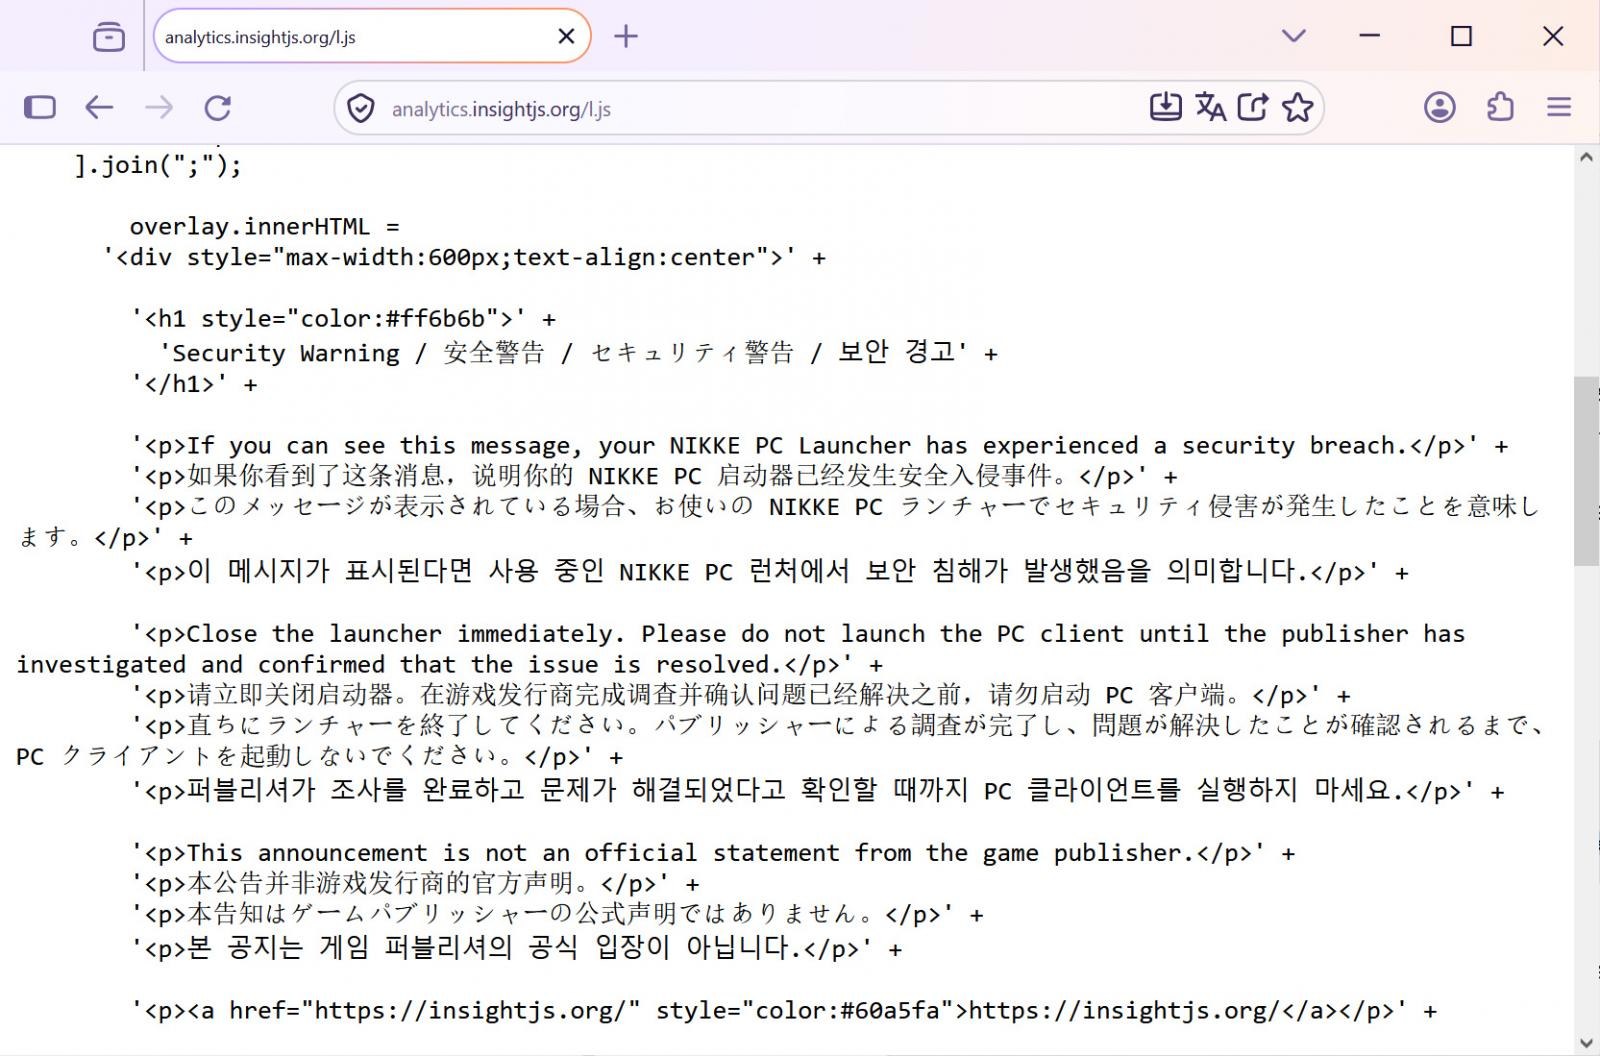
BleepingComputer discovered that the insightjs[.]org backup domain now serves code displaying a security warning within the game launcher. The warning, presented in English, Chinese, Japanese, and Korean, instructs players to immediately close the launcher and refrain from launching the PC client until the publisher confirms resolution. The message explicitly states it is not an official publisher announcement, leaving unclear who presently controls the domain or when the malicious payload was replaced.
Level Infinite did not respond to requests for comment on MotherSphere's analysis by publication time.
Players who may have been affected should execute a comprehensive system scan using current antivirus definitions. Those who determine they were compromised should perform a clean Windows installation and reset passwords and other sensitive credentials from an uncompromised device.