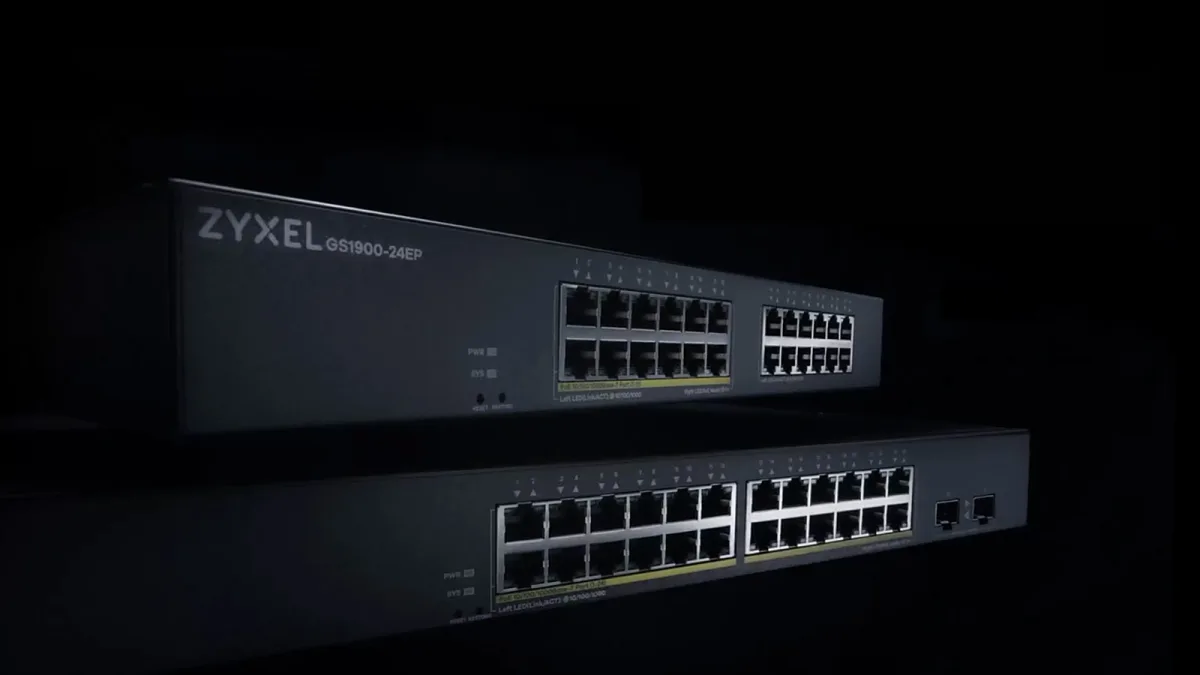
Zyxel has released a fix for a zero-day flaw affecting its GS1900 series network switches that threat actors exploited to breach nearly 1,000 devices globally and extract configuration data and login credentials. The vulnerability, identified as CVE-2026-107441, is an out-of-bounds write defect in the switches' web management interface that permits an unauthenticated attacker with network access to run operating system commands through malformed HTTP requests.
Ten different GS1900 switch models are vulnerable to this flaw. Zyxel distributed firmware patches on October 22 and issued a security advisory on November 3.
The discovery process revealed a critical misidentification: the vulnerability was initially confused with an earlier flaw that Zyxel had already remediated months before the exploitation campaign began.
Campaign mistakenly attributed to older vulnerability
In June 2026, Zyxel released updates for CVE-2026-7273, a pre-authentication buffer overflow affecting the same GS1900 product line. Beginning in mid-August, GreyNoise, a cybersecurity firm, detected activity from a suspected Chinese-speaking actor designated as Kapibala targeting Zyxel equipment. The group successfully compromised 996 devices spread across 48 nations.
The attackers leveraged the vulnerability to run remote commands, then deployed a script designed to harvest device settings, extract hashed root passwords, and gather network topology information. Researchers connected Kapibala to the Red Heron operation, which Acronis had previously documented as exploiting a severe flaw in the self-hosted Git platform Gitea.
When GreyNoise made its findings public on September 21, the campaign was attributed to CVE-2026-7273, the vulnerability Zyxel had already patched in June. On the same day, CISA included CVE-2026-7273 in its Known Exploited Vulnerabilities list, mandating that federal agencies patch the issue.
New vulnerability discovered during investigation
Binarly, a firmware security research firm, determined that the actual exploit in these attacks targeted a different, previously undiscovered vulnerability that had not been addressed. While examining Red Heron infrastructure associated with the JITTERLY backdoor and SIXZUT rootkit, Binarly researchers uncovered an exposed archive holding an obfuscated Python exploit designed for Zyxel GS1900 switches.
Analysis of the exploit revealed it explicitly verified for firmware versions that had been patched against CVE-2026-7273, suggesting the exploit was either newly created or modified to work around those patches. On September 28, Binarly verified that the exploit continued to function against all ten firmware releases that had received the CVE-2026-7273 fix.
The researchers identified the mechanism: the earlier security update introduced protections against buffer overflow, but attackers could circumvent these by corrupting a parameter counter before validation occurred. This technique enabled memory corruption and command execution without requiring authentication, even on devices running the patched firmware.
Binarly notified Zyxel of the findings on September 29. The vendor acknowledged the new vulnerability on October 11 and assigned it the identifier CVE-2026-107441. Zyxel determined it warranted a separate CVE designation because the exploit also took advantage of inadequate validation of HTTP parameter lengths.
On October 22, Zyxel deployed updated firmware that enforces parameter size limits and validates parameter counts before copying data into memory, blocking the exploitation method. Whether the recovered exploit was intentionally engineered to circumvent the earlier updates or exploited a related weakness that those patches did not fully address remains uncertain.
Organizations running affected Zyxel GS1900 switches should apply the latest firmware updates immediately to mitigate the risk from CVE-2026-107441.