Cybersecurity authorities across three nations have issued alerts about state-sponsored Iranian hackers leveraging a Windows malware called CHOSEN BRICK to conduct surveillance operations against dissidents, activists, and journalists on a global scale.
The malware variant carries extensive espionage and data exfiltration capabilities. Its functionality includes harvesting email messages, Telegram and WhatsApp communications, capturing screen images, and recording audio from infected systems.
The campaign has primarily focused on individuals located in the United States, United Kingdom, and Netherlands. Cybersecurity agencies from these three countries collaborated with the FBI to release a coordinated advisory on the threat.
Attack methodology
Attackers initiate campaigns by sending social engineering messages through WhatsApp or Telegram. These messages impersonate either known contacts or representatives claiming to provide technical support.
Victims are manipulated into executing malicious files that masquerade as legitimate software. Common lures include applications such as Pictory, RunwayML, Norton Antivirus, Telegram, Adobe Flash Player, and KeePass. Attackers frequently suggest running these applications on personal devices to circumvent corporate security infrastructure.
In some instances, the agencies discovered that attackers employed medical-themed pretexts to increase credibility and success rates.
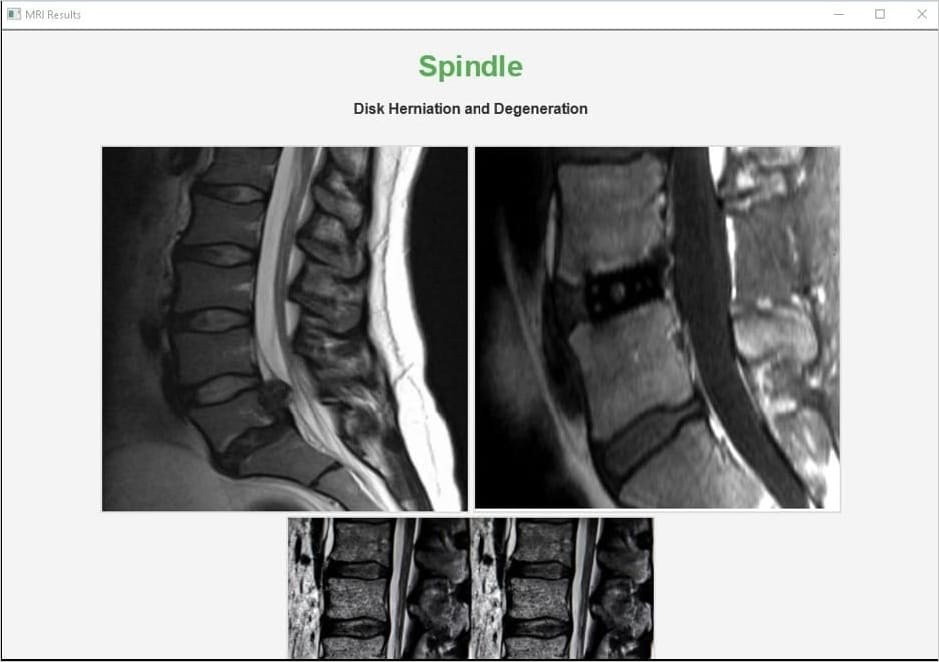
Upon execution, the malicious application displays a user interface matching the impersonated software while covertly deploying CHOSEN BRICK. The malware establishes persistence by creating entries in the Windows Registry Run keys.
To prevent detection, CHOSEN BRICK modifies Microsoft Defender settings to exclude itself from scanning. Command-and-control communication occurs through a dedicated Telegram bot configured with the victim's unique identifier.
Malware capabilities
Once installed, CHOSEN BRICK enables attackers to perform extensive operations on compromised systems:
- Retrieve system configuration details
- List active running processes
- Take screenshots of the display
- Capture audio via the system microphone
- Extract email messages
- Harvest Telegram and WhatsApp data stored in browsers
- Retrieve and execute additional malware payloads to the
C:\Windows\SysWOW64directory - Remove specific files
- Perform complete system destruction
Data exfiltration and impact
Stolen information is transmitted to attackers through Telegram or cloud storage platforms including VultrObjects and StorjShare. Newer versions of CHOSEN BRICK route communications through SOCKS5 proxies to obscure the data transfer.
The advisory highlights that harvested data frequently surfaces on websites aligned with Iranian interests, functioning as a harassment mechanism. This public disclosure increases physical danger for targeted individuals living outside Iran.
Iran almost certainly uses cyber activity to support the repression of individuals who are seen as a threat to the regime, such as dissidents, activists and journalists. In some cases, the Iranian intelligence services have plotted to kidnap or conduct lethal operations against individuals internationally, who they perceive as enemies of the regime.
U.S., U.K., and Dutch cybersecurity agencies
Detection and mitigation
Organizations and potential targets should conduct thorough reviews of Windows Registry Run entries to identify suspicious additions. System logs should be examined for indicators of compromise provided in the official advisory.
Network traffic patterns warrant investigation if they show unexpected connections to Telegram's API, Backblaze B2, VultrObjects, StorjShare, IPRoyal, or LightningProxies. Such connections may indicate active compromise or attempted data exfiltration.