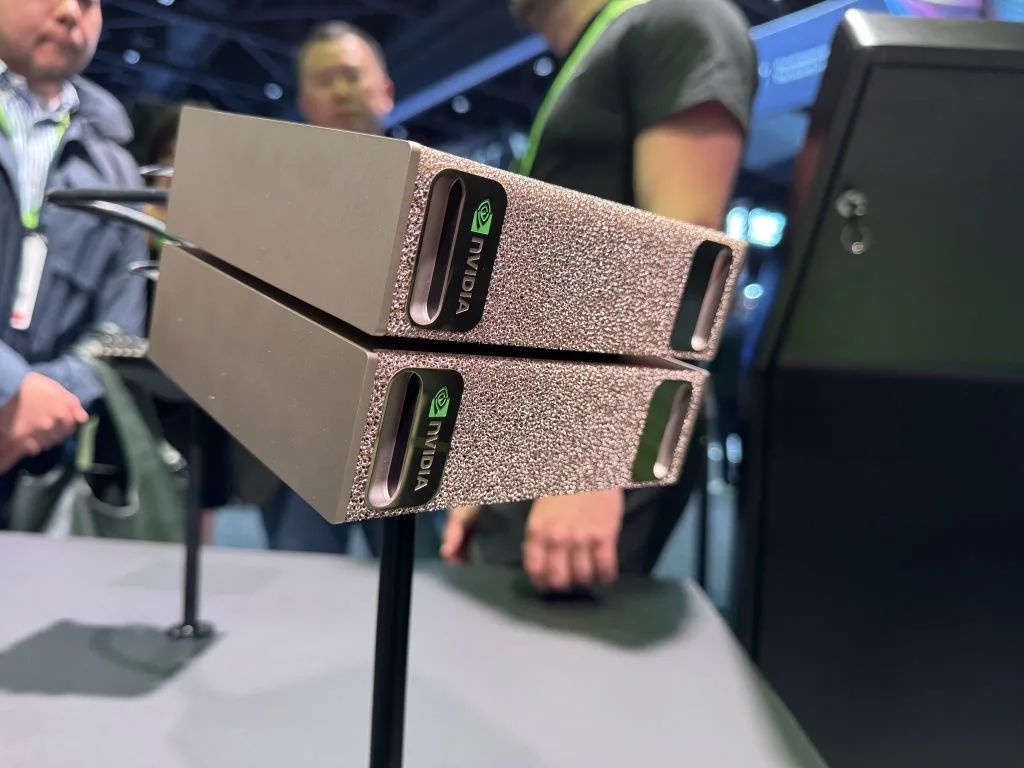
Nvidia transferred OpenShell to the Cloud Native Computing Foundation this week, positioning the open-source runtime for agent security and governance within the foundation's early-stage project tier. Teams operating OpenShell in production already depend on Kubernetes and other CNCF initiatives, according to Ali Golshan, Nvidia's senior director of AI software and the project's leader.
The announcement came Tuesday at KubeCon + CloudNativeCon North America in Salt Lake City. OpenShell, which Nvidia first unveiled at its GTC conference in March, entered the CNCF as a Sandbox project—the foundation's entry point for nascent initiatives. The CNCF formally approved the project in late September. Among the foundation's 262 hosted projects, 155 currently reside at the Sandbox level.
The Linux Foundation, which oversees the CNCF, also operates the Agentic AI Foundation (AAIF), home to agentgateway, the Model Context Protocol (MCP), and the Agent2Agent (A2A) protocol. Last month, the AAIF welcomed OpenSandbox, a sandbox environment for AI agents that Alibaba contributed. Yet Golshan saw the CNCF as the more fitting destination. He explains: "Securing and creating trust around AI is really infrastructure. That's really where you need to start."
Infrastructure as the operational anchor
OpenShell executes agents within a sandbox and applies policies governing which files, networks, credentials, and model endpoints each agent can access. The CNCF notes that this enforcement operates at the infrastructure layer, and OpenShell is adopting Cedar, a CNCF project, as its policy language.
Golshan contends that agent security demands a complete stack solution—something Nvidia could not assemble piecemeal. He states: "We can't go build OpenShell and then go build the next pieces of it. And a lot of those pieces, from an infrastructure standpoint, already existed in CNCF." He points to Kubernetes, the lightweight K3s variant, and service meshes as examples of complementary projects already in place.
During OpenShell's development, the team recognized who would ultimately operate it. The profile matched the DevSecOps engineer responsible for deploying a company's broader infrastructure stack. Golshan references SAP as an organization where DevOps and infrastructure teams provision large agent deployments. Though engineers or researchers may interact with agents directly, the operators are "the same teams that are spinning up Kube and Linux and that whole stack."
Ideally, end users remain unaware of OpenShell's presence. Golshan draws a parallel: "You don't really see Kubernetes. You just get that environment."
Jonathan Bryce, the CNCF's executive director, frames the placement decision differently: "where are the people who are going to be making the decision about deploying, using, contributing to a specific technology?" Agent development began with hobbyists running OpenClaw on Mac Minis, Bryce notes, but production-grade, SaaS-oriented agents resemble traditional data center software. Before OpenShell joined the CNCF, much early adoption came from neoclouds—GPU cloud providers seeking to govern customer workloads on their platforms. Since OpenShell integrates with Kubernetes and ecosystem projects, teams already running that infrastructure can readily incorporate it into their containment strategies.
Agent projects distributed across foundations
Agents will span the entire technology stack, Bryce says, with supporting open-source projects distributed across multiple foundations, each attracting distinct contributor bases.
The PyTorch Foundation hosts PyTorch, vLLM, DeepSpeed, and Ray—projects where engineers with deep AI expertise congregate. Bryce compares them to "the people who write Postgres." The CNCF, by contrast, draws "the very broad set of folks who understand how to take mature systems and deploy, scale, observe, secure them." The AAIF, with its MCP and A2A protocols, focuses on the agent front-end experience. Bryce likens these protocols to HTTP and JavaScript—standards that enabled millions of web applications.
The foundations operate as "Venn diagrams" rather than isolated silos, Bryce emphasizes, "and I think that's good." He points to KubeRay, which runs Ray workloads on Kubernetes, and llm-d, which pairs vLLM with Kubernetes. The AAIF's agentgateway also works with Kubernetes.
The CNCF maintains flexibility about project placement, allowing maintainers to "choose their own adventure to some extent," Bryce notes. Nvidia's perspective on how organizations deploy AI workloads is "unparalleled," he adds, and the company brings new projects grounded in that experience to each KubeCon. "Some of those end up in a foundation," he says. "Some of them don't."
Governance and security frameworks
Golshan joined Nvidia in 2025 following the company's acquisition of Gretel, the synthetic data startup he co-founded. Previously, he co-founded StackRox, the Kubernetes security firm that Red Hat acquired in 2021.
The OpenShell team's founders had contributed to CNCF projects and understood its governance structure firsthand. That model aligned with their vision: a focused mission for OpenShell within a larger ecosystem.
Security governance remains in development. OpenShell currently holds Sandbox status, and Golshan says the team is "spending a bunch of time thinking through" establishing an independent security committee. He elaborates: "One of the things that I think becomes very important is how do you manage things like disclosures, vulnerabilities." If OpenShell becomes critical infrastructure, it requires contributions from many participants, "not necessarily us."
Nvidia's engineers will continue stewarding the project's core, though Red Hat, Docker, and Canonical have been core contributors alongside Nvidia from inception. When Nvidia opened OpenShell for early access in March, roughly 10 to 15 companies participated. The project shed its alpha designation with the 0.1.0 release in September, and the CNCF's project page now lists approximately 380 contributing organizations.
Bryce observes: "There are a lot of people who will engage at a certain level without it being in neutral governance. But once it makes that move to fully neutral governance, then that engagement gets a lot deeper." Adoption timelines that once spanned two or three years now compress to six to 12 months, he notes, with neutral governance serving as "rocket fuel" for integration and adoption. He cites llm-d as an example: "llm-d came into CNCF in March of this year, and they now have their 1.0 release, and they have a whole set of companies that are actually running it in production, including some of the neoclouds."
Building the ecosystem around OpenShell
Golshan emphasizes that OpenShell requires a surrounding ecosystem of tools before it can operate at production scale. Approximately 50 to 60 companies—ranging from startups to established vendors—have built on it. OpenShell now defines extension points for compute, credential management, inference providers, and policy enforcement, and Golshan hopes the CNCF community will use them as a template for integrating OpenShell with the broader cloud native ecosystem.
He states: "It would be amazing if within the next six months we could support everything from Istio to Envoy to K3s for edge."
Since the 0.1.0 release, early adopters transitioning agents from research to production have requested guidance on security, privacy, and observability tools that integrate natively with OpenShell. They also seek assistance optimizing agents and the harnesses that contain them. During a recent conversation in Berlin, Golshan recalls speaking with someone already familiar with Datadog and distributed tracing: "I don't even know what to observe for an agent."
Golshan wants insights from those edge cases to feed back into OpenShell's core, mirroring how Kubernetes evolved. He reflects: "It's pretty easy these days to say I'm going to bet my company on Kube. Nobody's going to get fired for that." He aspires for OpenShell to reach that same status.
Settling an emerging agent architecture
The stack for model training is well-defined, and inference infrastructure has largely stabilized, Bryce observes, but the agent stack remains unsettled. He explains: "If there's not a clear stack, then the industry can't come together on the most significant problems and actually make really fast, rapid progress."
Over the next six to 12 months, Bryce expects experimentation to crystallize into concrete answers about how OpenShell integrates with Kata Containers, gVisor, Agent Substrate, and existing OpenTelemetry projects. Once that convergence occurs, he anticipates agents will accelerate the way inference has during the past eight months.
Two of those projects are recent CNCF additions. Google contributed Agent Substrate, its framework for running long-lived agents on Kubernetes, and the gVisor sandbox runtime at this week's KubeCon. Nvidia reports it is collaborating with Google on integrating OpenShell with Agent Substrate.