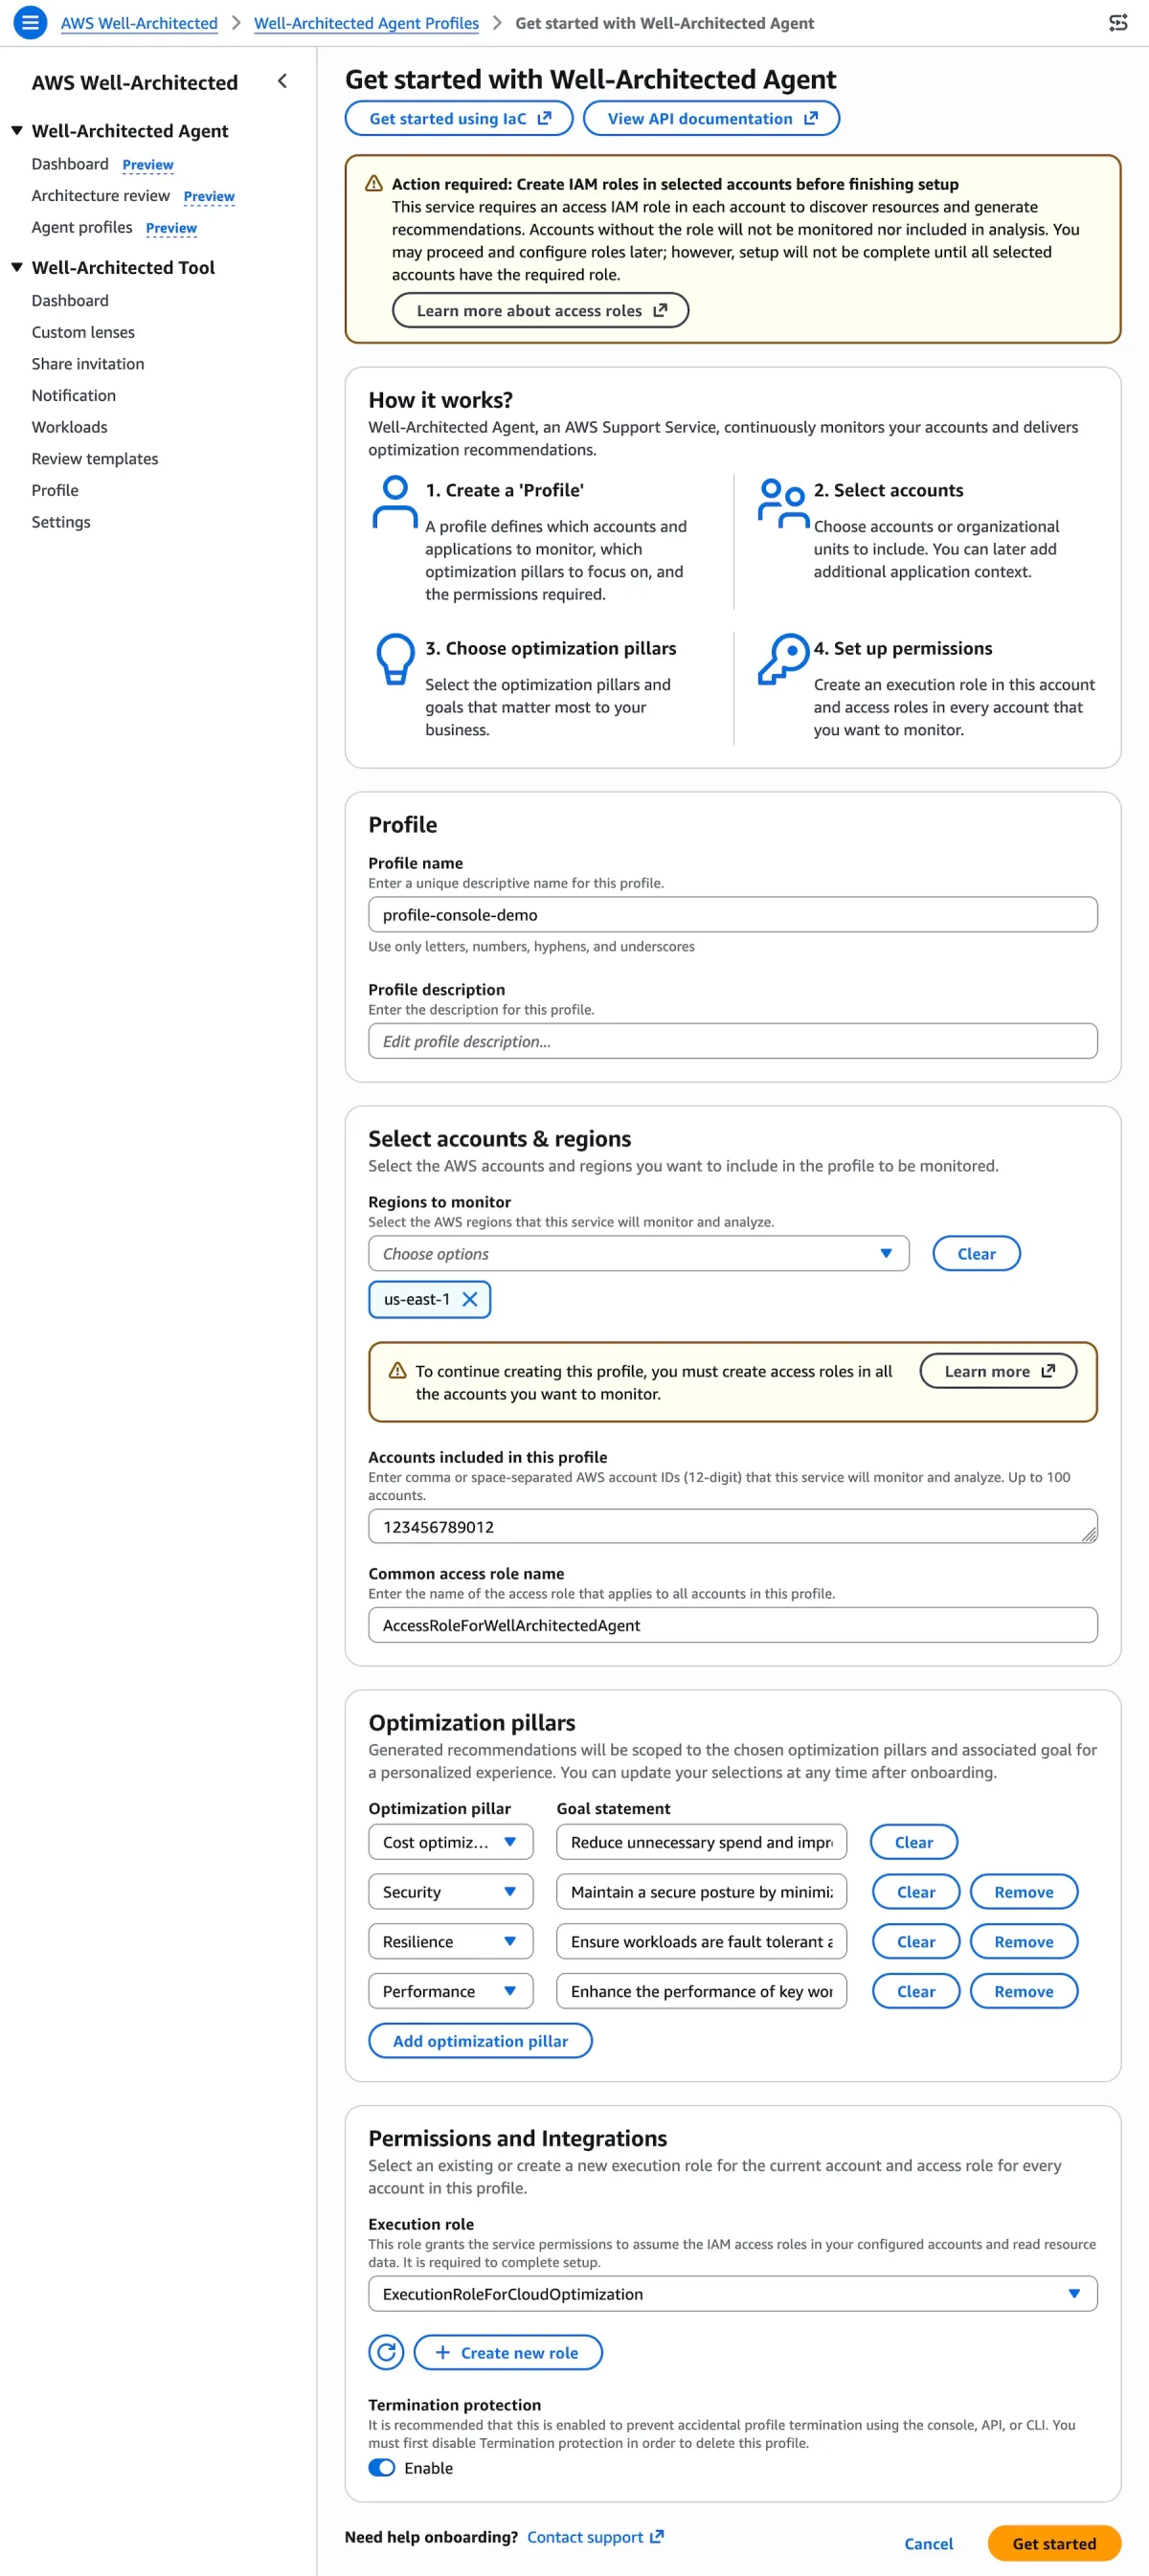
AWS has introduced the public preview of Well-Architected Agent, an artificial intelligence-driven service designed to examine AWS deployments and offer focused, situation-specific guidance for enhancing application cost efficiency, security posture, performance characteristics, and fault tolerance. The tool examines infrastructure layouts, incorporates understanding of distinct business priorities, and supplies actionable recommendations that come with implementation-ready solutions. This approach eliminates the need for hands-on architectural assessments or one-size-fits-all evaluation frameworks.
The agent functions similarly to how an experienced cloud architect would assess infrastructure. It automatically cross-references consumption patterns, setup details, and system architecture, then benchmarks findings against Well-Architected principles spanning 65+ AWS services. It tailors suggestions to match stated business priorities, bundles implementation guidance with each finding, and highlights trade-offs between optimization areas to streamline remediation efforts.
Core capabilities
- Goal-aligned intelligence: The agent moves beyond generic findings to deliver context-specific, ranked suggestions. Organizations specify business objectives and supply application specifics, enabling the agent to generate and rank recommendations based on their impact and implementation complexity relative to those goals.
- Three-level recommendations: The service offers individual resource-level findings with quantified cost implications (where available) plus step-by-step fixes, aggregated findings across resource groups scoped to particular applications, and system-wide architectural patterns with Infrastructure as Code (IaC) modifications required to meet Well-Architected standards.
- Remediation flexibility: Teams select their preferred remediation method with customized implementation steps: guided console procedures, refreshed IaC definitions for architectural-level changes, and AWS Command Line Interface (AWS CLI) operations.
Getting started
To begin using the service, users establish an agent profile specifying the scope of monitoring and recommendations, configure IAM role permissions to enable resource access, execute an architecture evaluation, and implement the suggested optimizations.
Profile creation and configuration
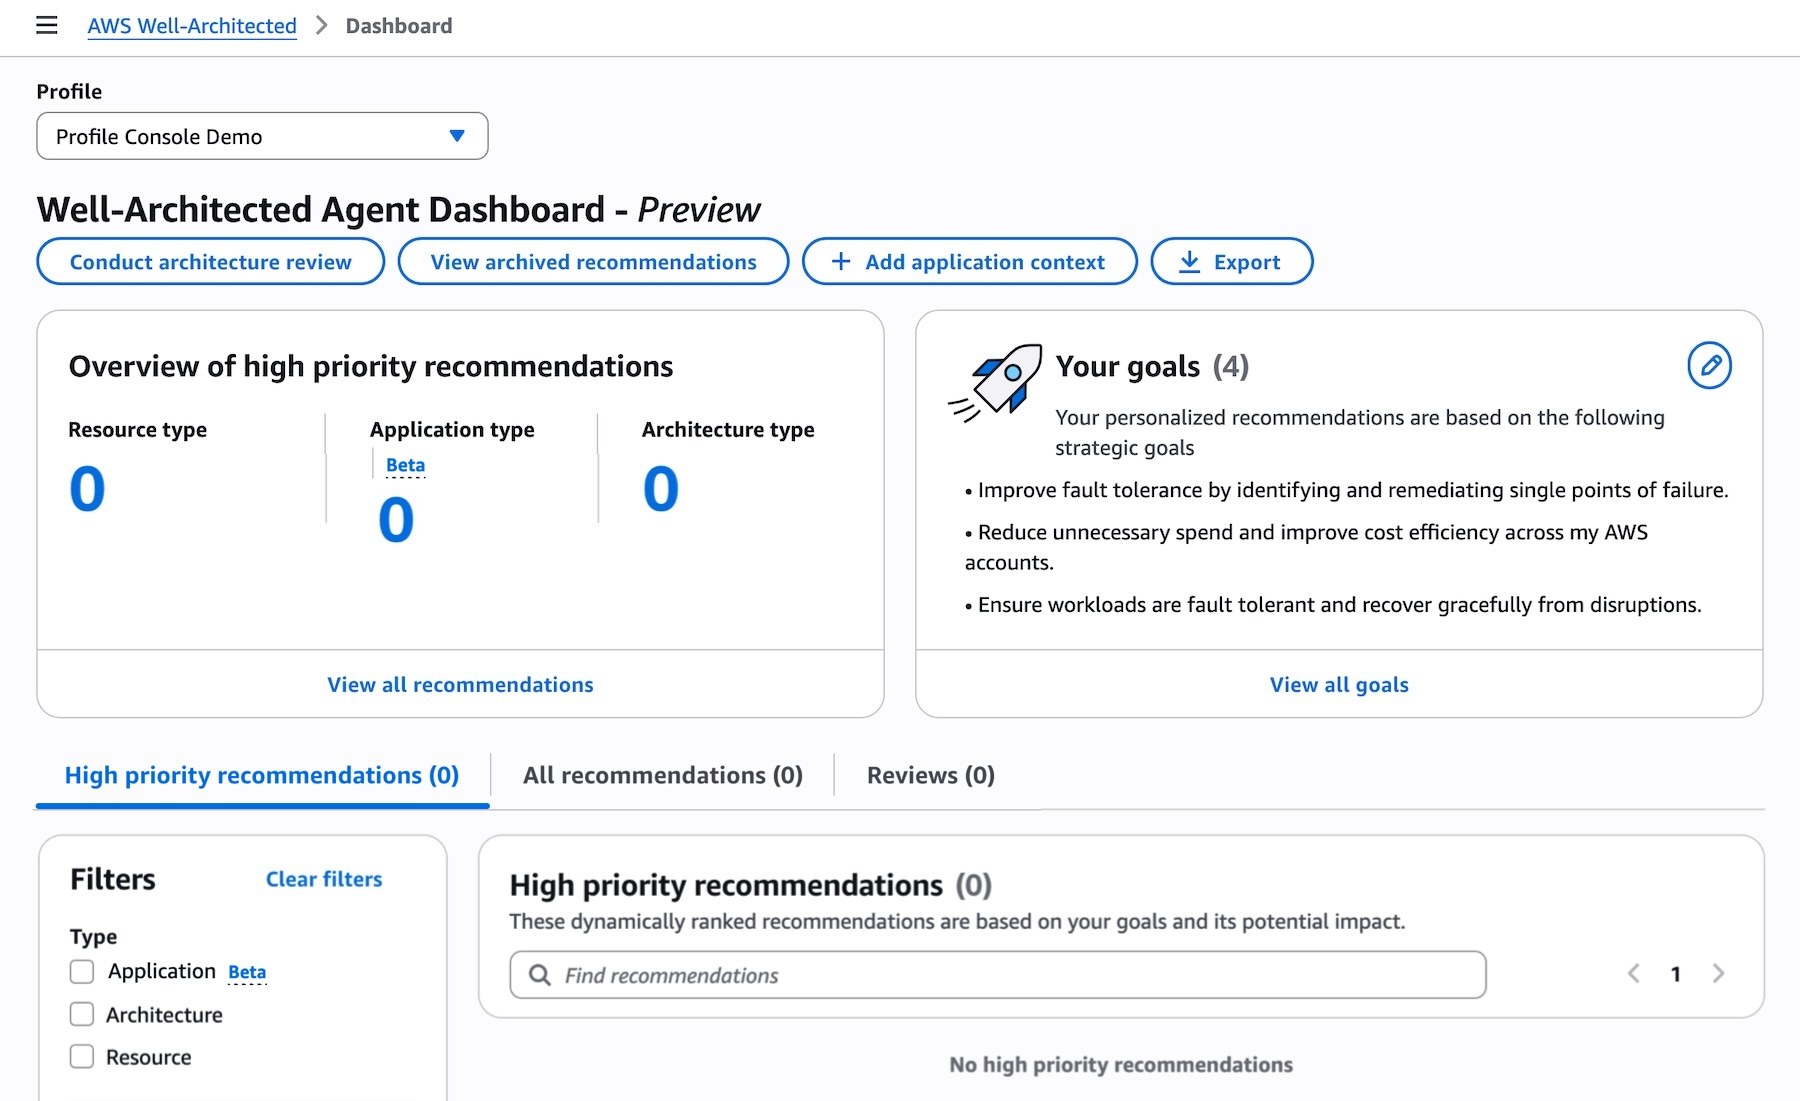
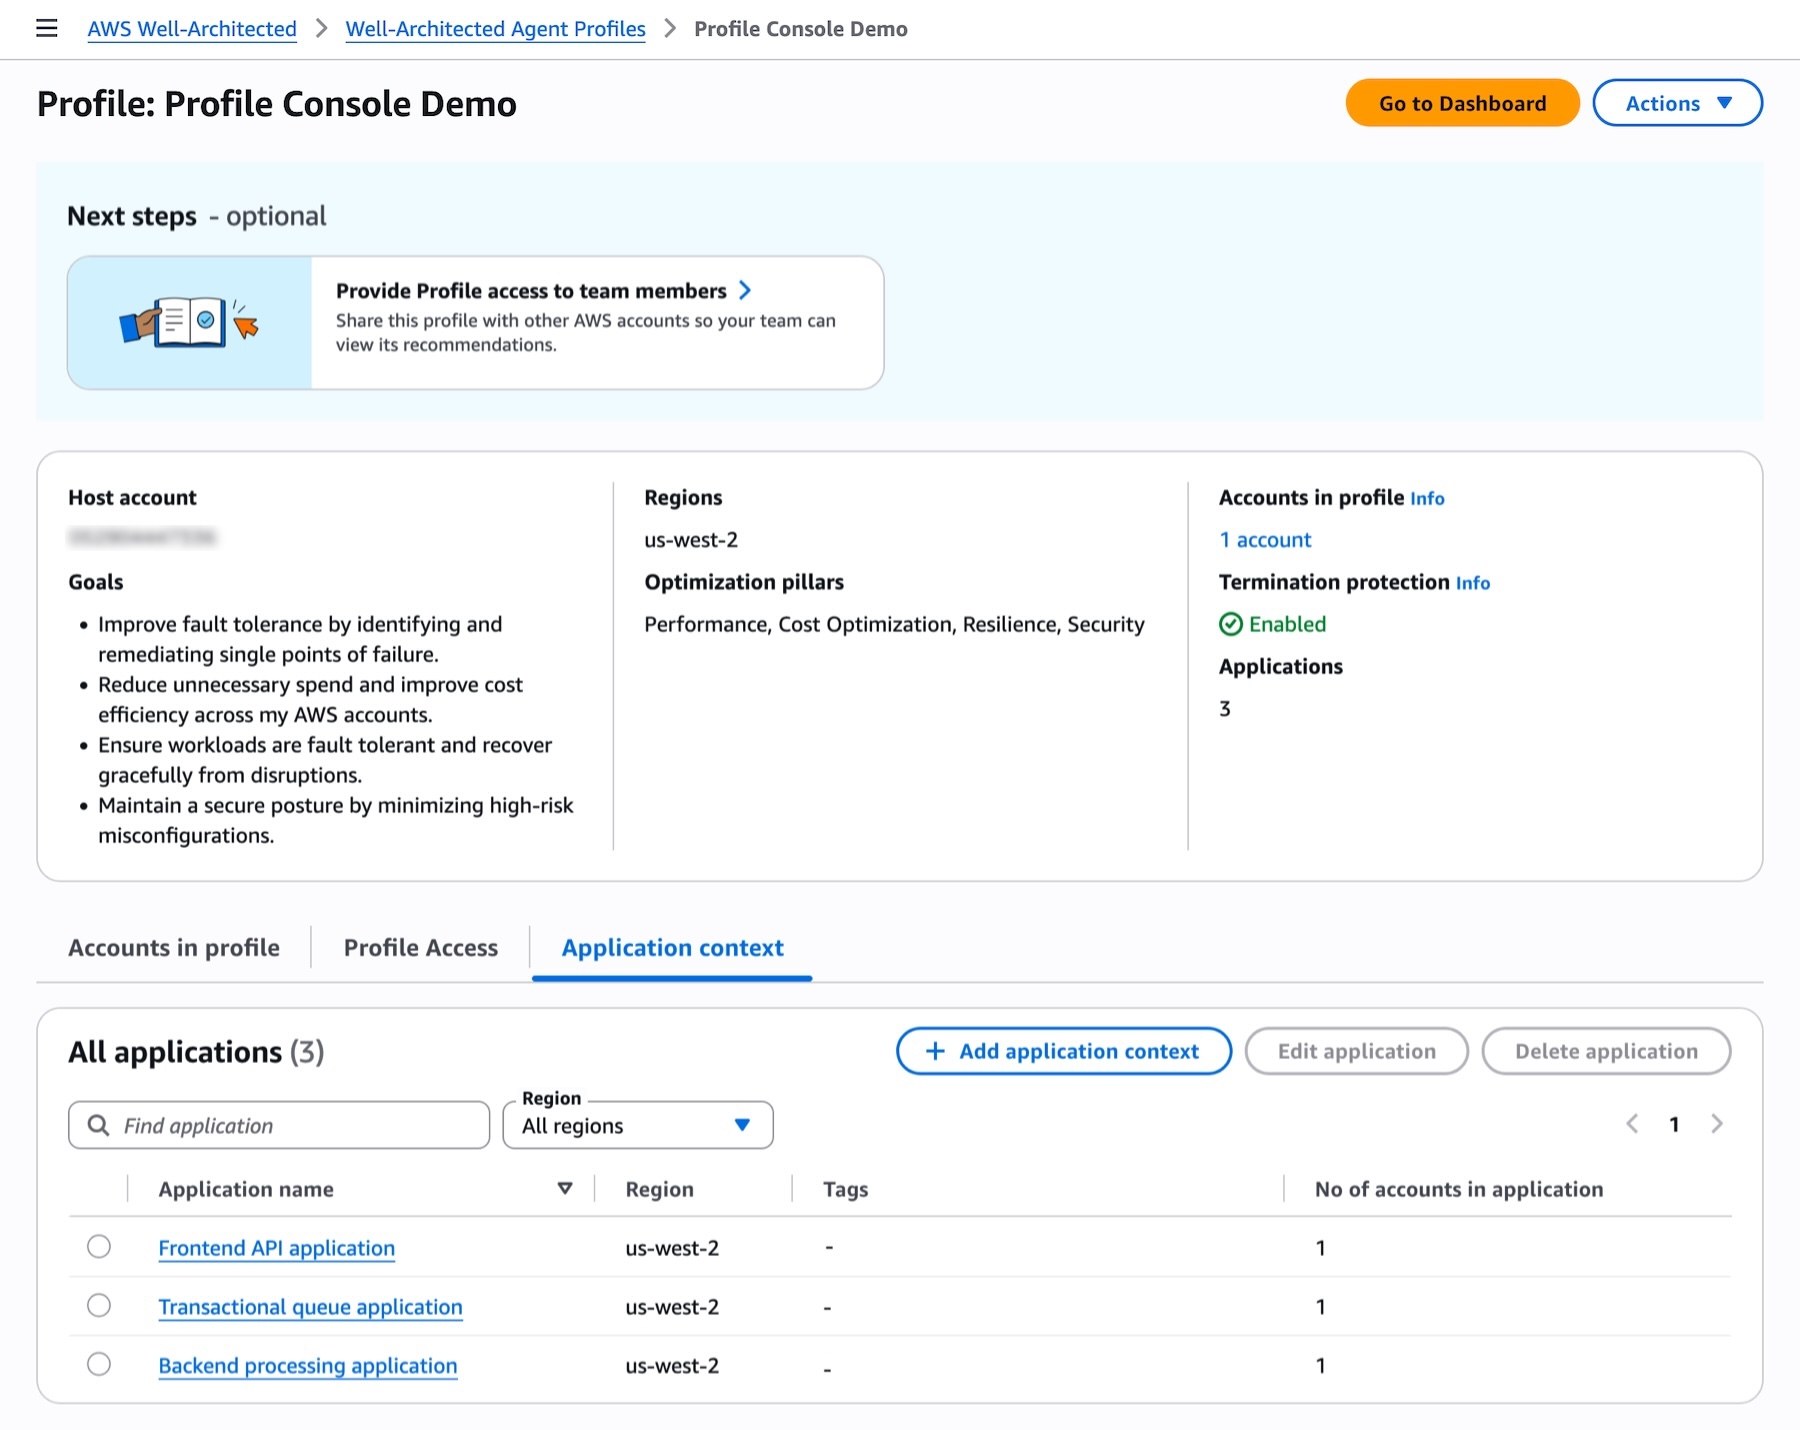
Within the AWS Well-Architected console, selecting Get started with Well-Architected Agent initiates profile setup. This profile determines which AWS accounts and applications receive monitoring, which optimization focus areas apply, and the required access permissions. Organizations can specify which accounts or regions to assess and which optimization pillars—cost optimization, performance, resilience, and security—take priority. The system generates resource and application recommendations within 24 hours of profile creation.
To grant the agent access to the AWS environment, teams must set up customer-managed IAM roles that permit the service to retrieve resource configurations, consumption data, and application topology information.
Pre-deployment analysis
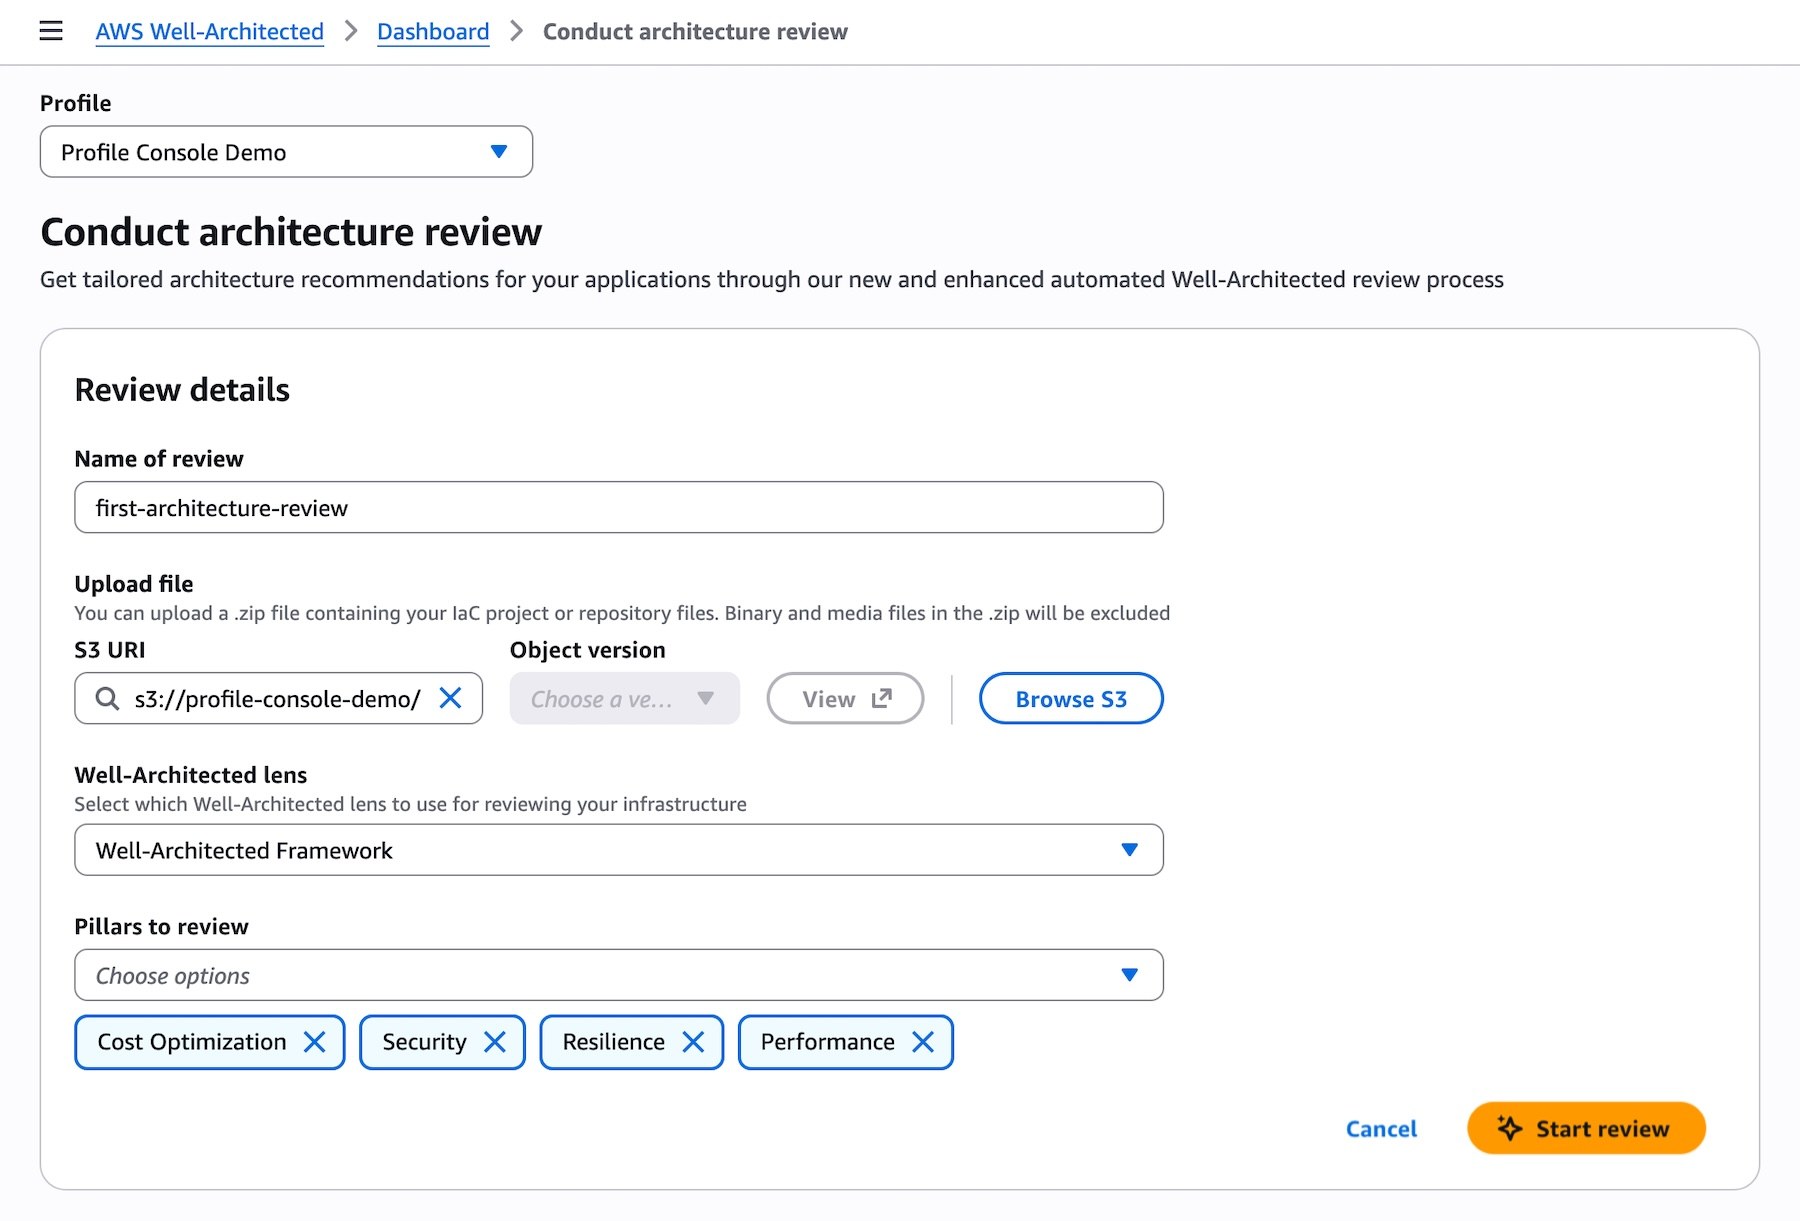
The agent can evaluate infrastructure before deployment by accepting IaC projects in Terraform, AWS CloudFormation, or AWS Cloud Development Kit (CDK) formats. Users upload a compressed file containing the IaC project or repository and select the appropriate Well-Architected lens for evaluation.
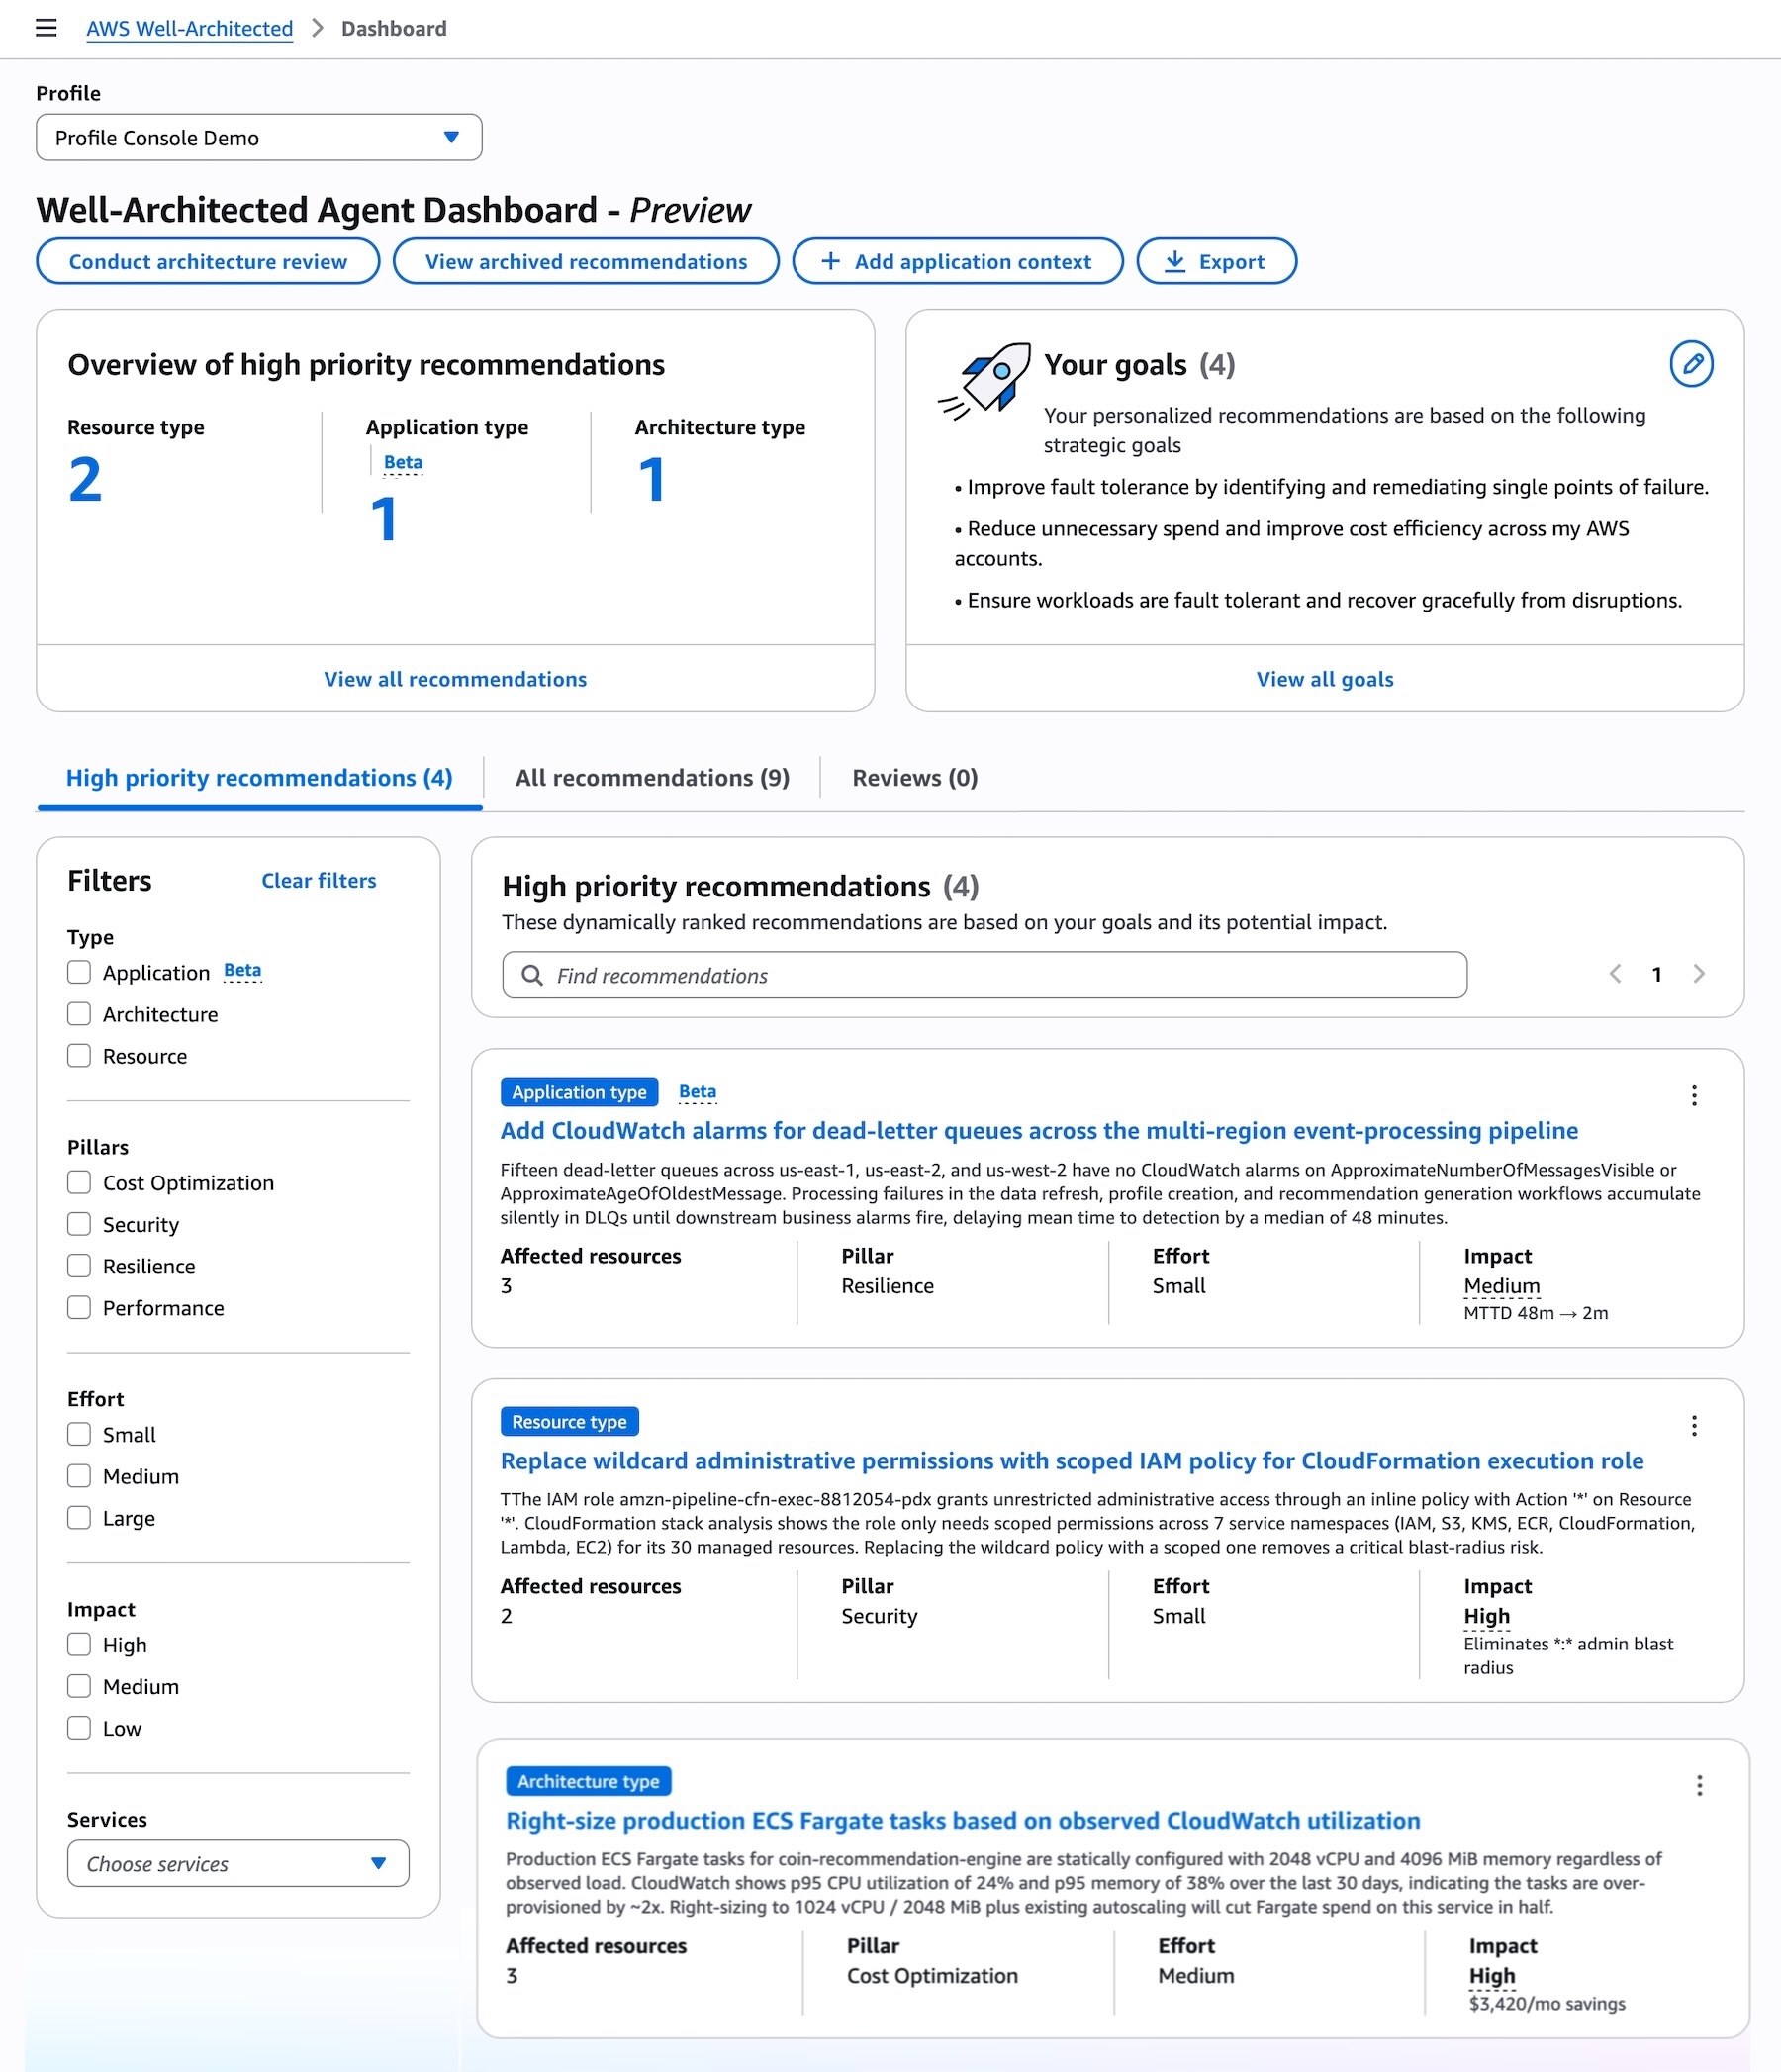
Application context and recommendation review
Adding application context improves recommendation specificity and relevance. Teams supply application details including associated AWS accounts, regions, services, and resource tags to narrow scope. Once configured, the dashboard displays ranked recommendations filtered by selected optimization areas and aligned with declared objectives, complete with automation-ready remediation paths.
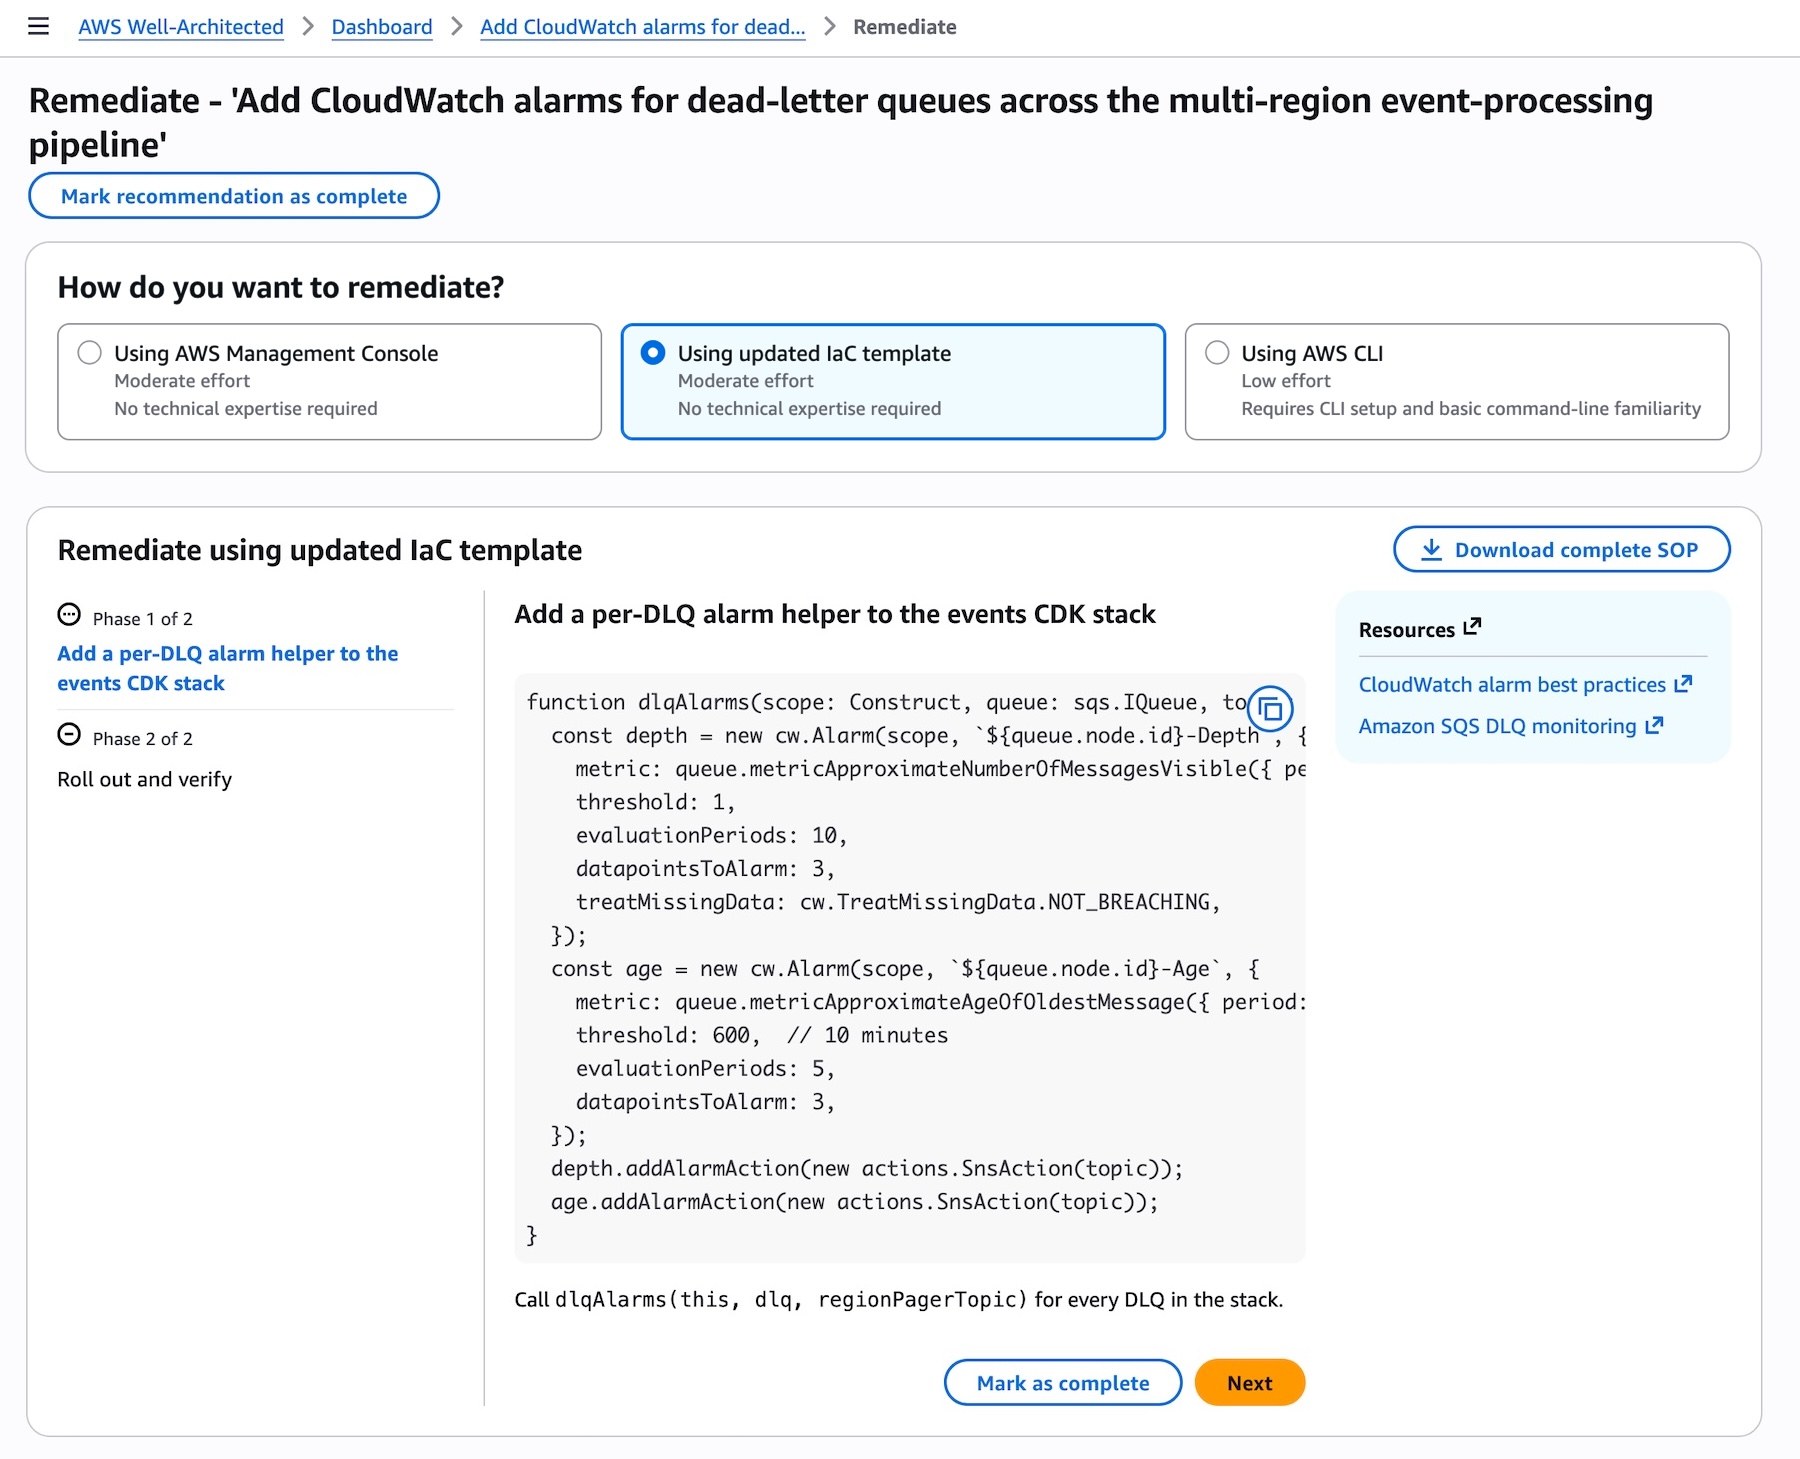
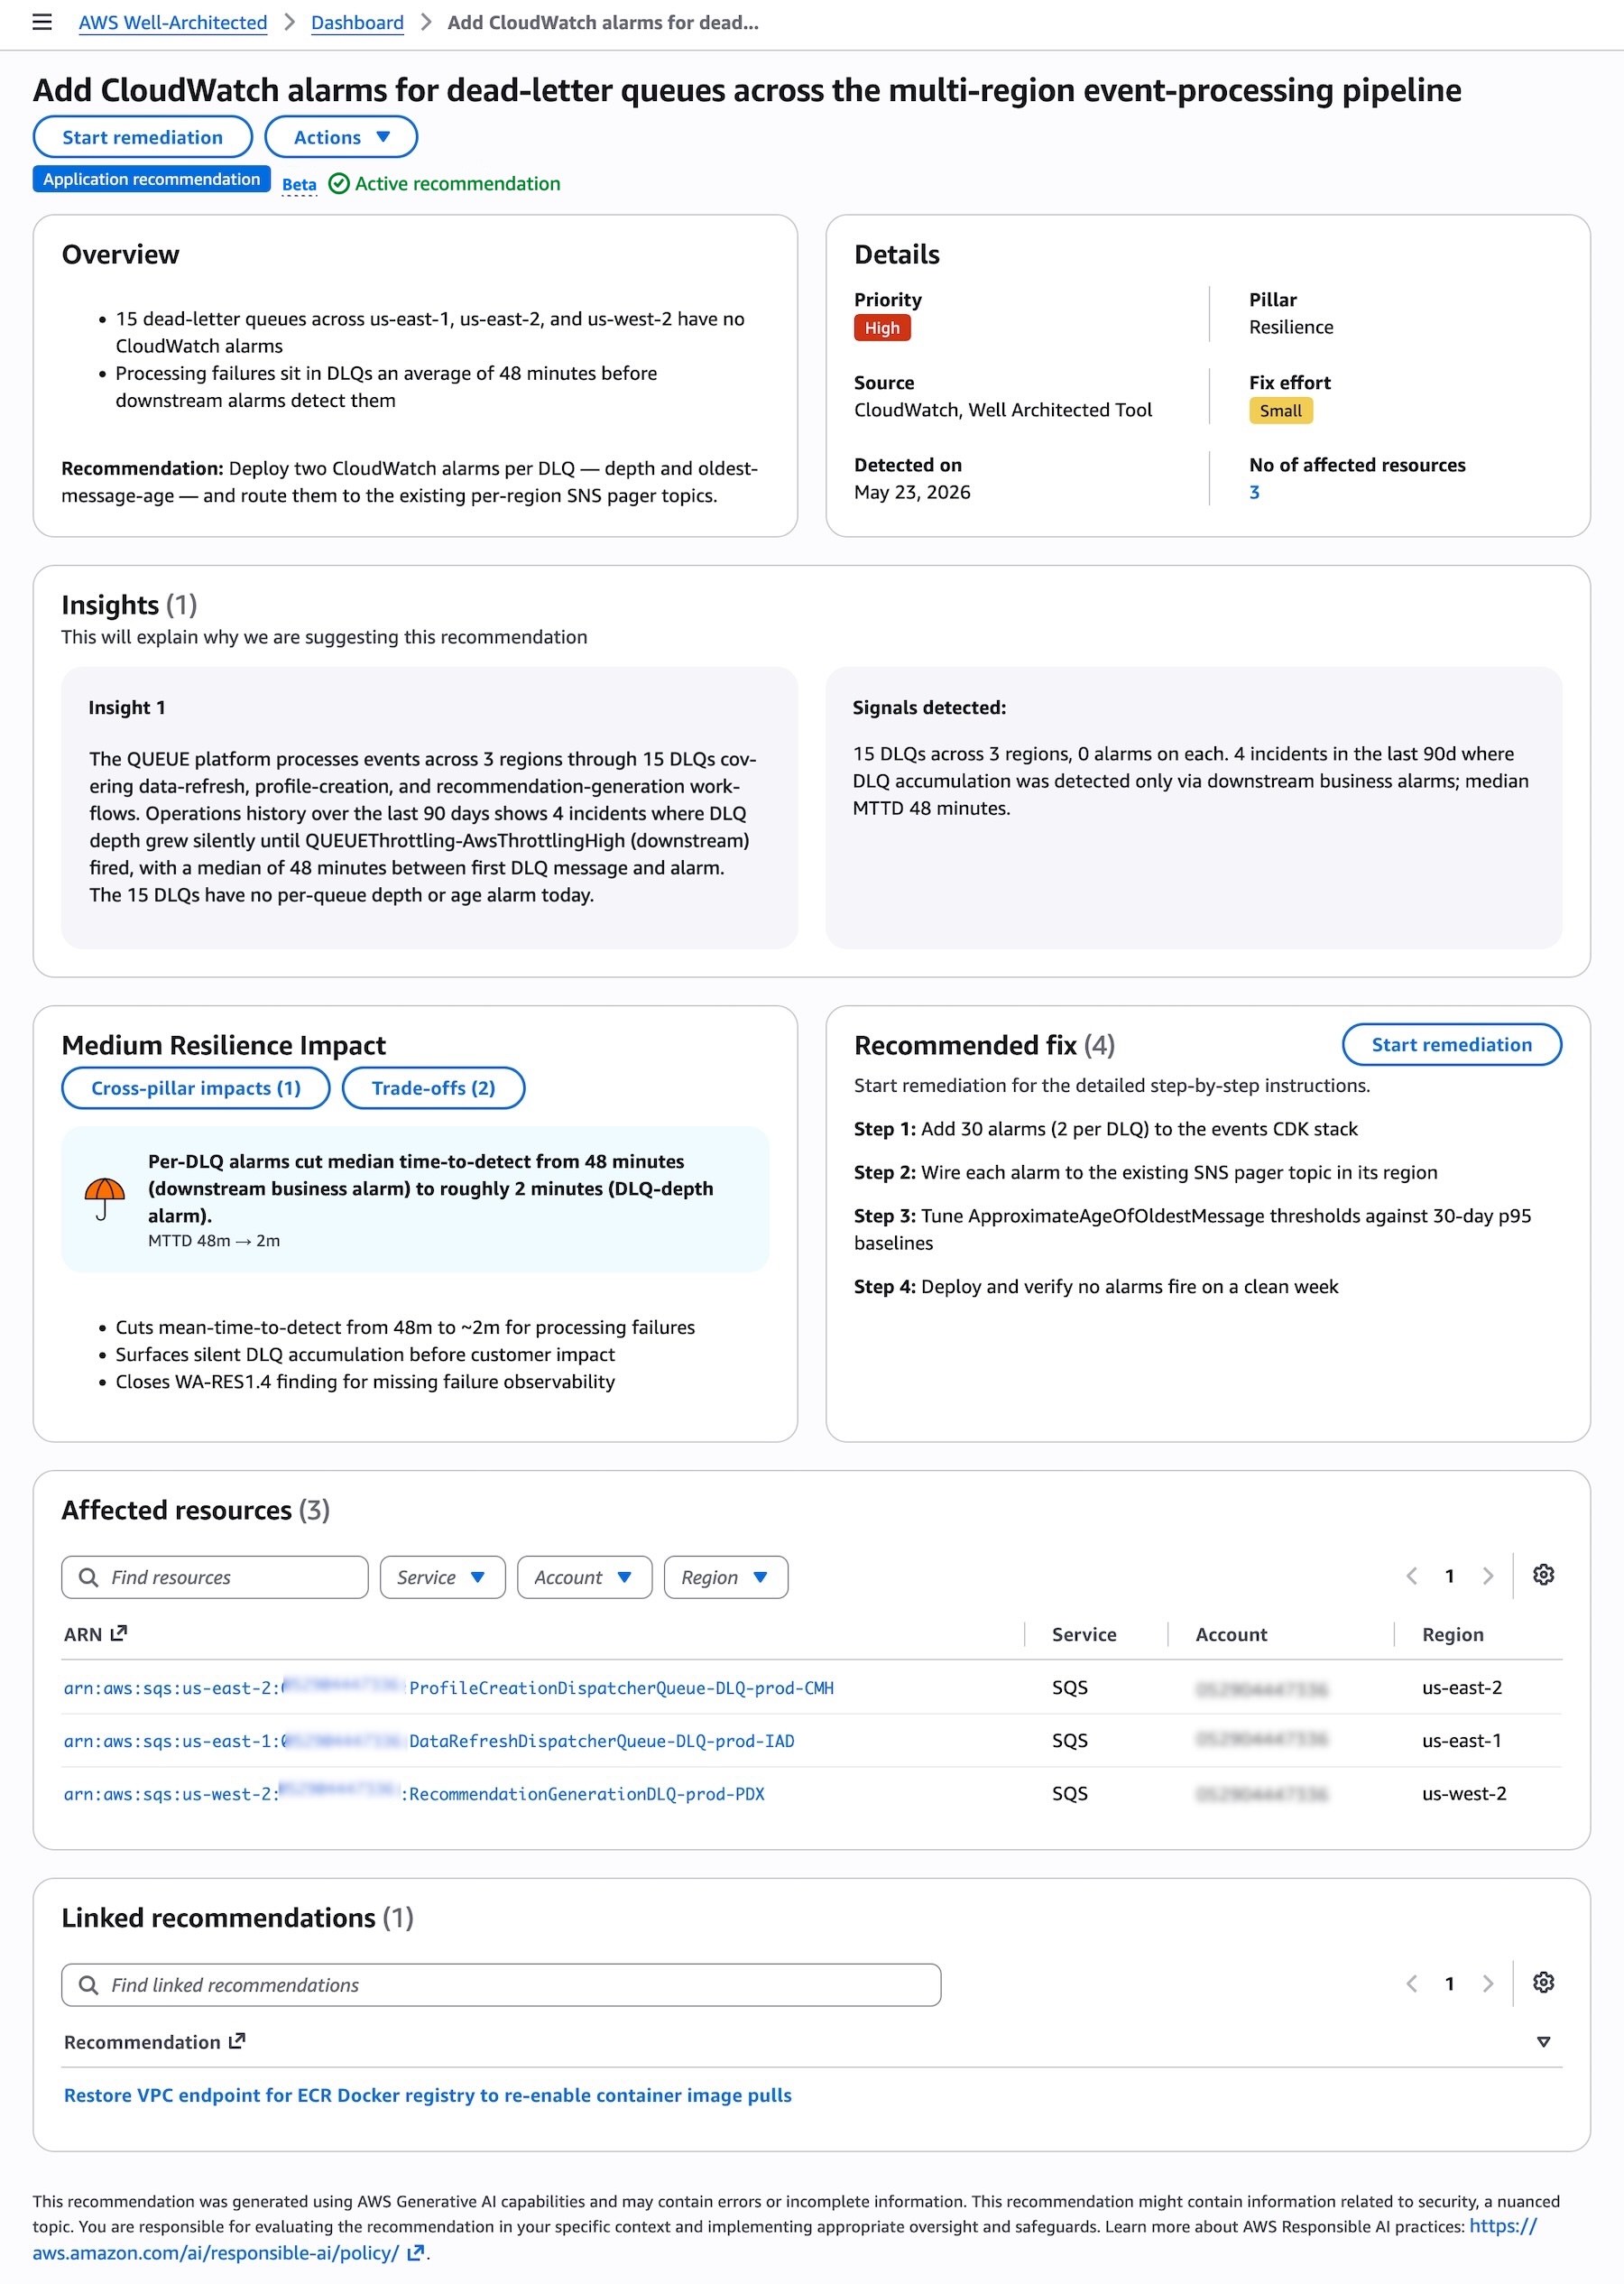
Selecting a specific recommendation reveals implementation details, the reasoning behind the suggestion, potential impacts and trade-offs, and proposed fixes across affected resources. Choosing Start remediation offers three implementation options: console-based steps, updated IaC templates with code changes ready to integrate into existing codebases, or CLI commands with detailed instructions for verification.
Teams can also enable API access to embed recommendations into existing development and operations systems. The AWS MCP Server and plugins allow programmatic interaction with the agent through preferred AI coding tools.
Important considerations
- Automation: Recommendations include exact IaC code modifications, risk identification by pillar, and early issue detection before production deployment. Suggestions reach teams through console and API interfaces without requiring context switching, and update periodically to reflect new optimization opportunities.
- Evaluation responsibility: Generative AI-produced recommendations may contain inaccuracies or gaps. Organizations must assess recommendations within their specific circumstances and implement appropriate oversight and safeguards. AWS provides guidance on Responsible AI practices for this purpose.
The existing AWS Well-Architected Tool remains available for manual cloud architecture evaluation using custom lenses based on organization-specific best practices.
Availability and access
AWS Well-Architected Agent preview access is currently available in US East (N. Virginia), US East (Ohio), and US West (Oregon), though workloads from any AWS commercial region can be onboarded. The service is delivered through AWS Support and requires an active AWS Support plan. Organizations can begin testing in the AWS Well-Architected console and submit feedback via their AWS Support contacts.