Zeabur, a developer hosting and deployment platform, has revealed details of a security incident in which attackers exploited leaked internal credentials stored without encryption to breach its infrastructure and obtain over 3.2 million environment variable records alongside data from 321,810 customer accounts.
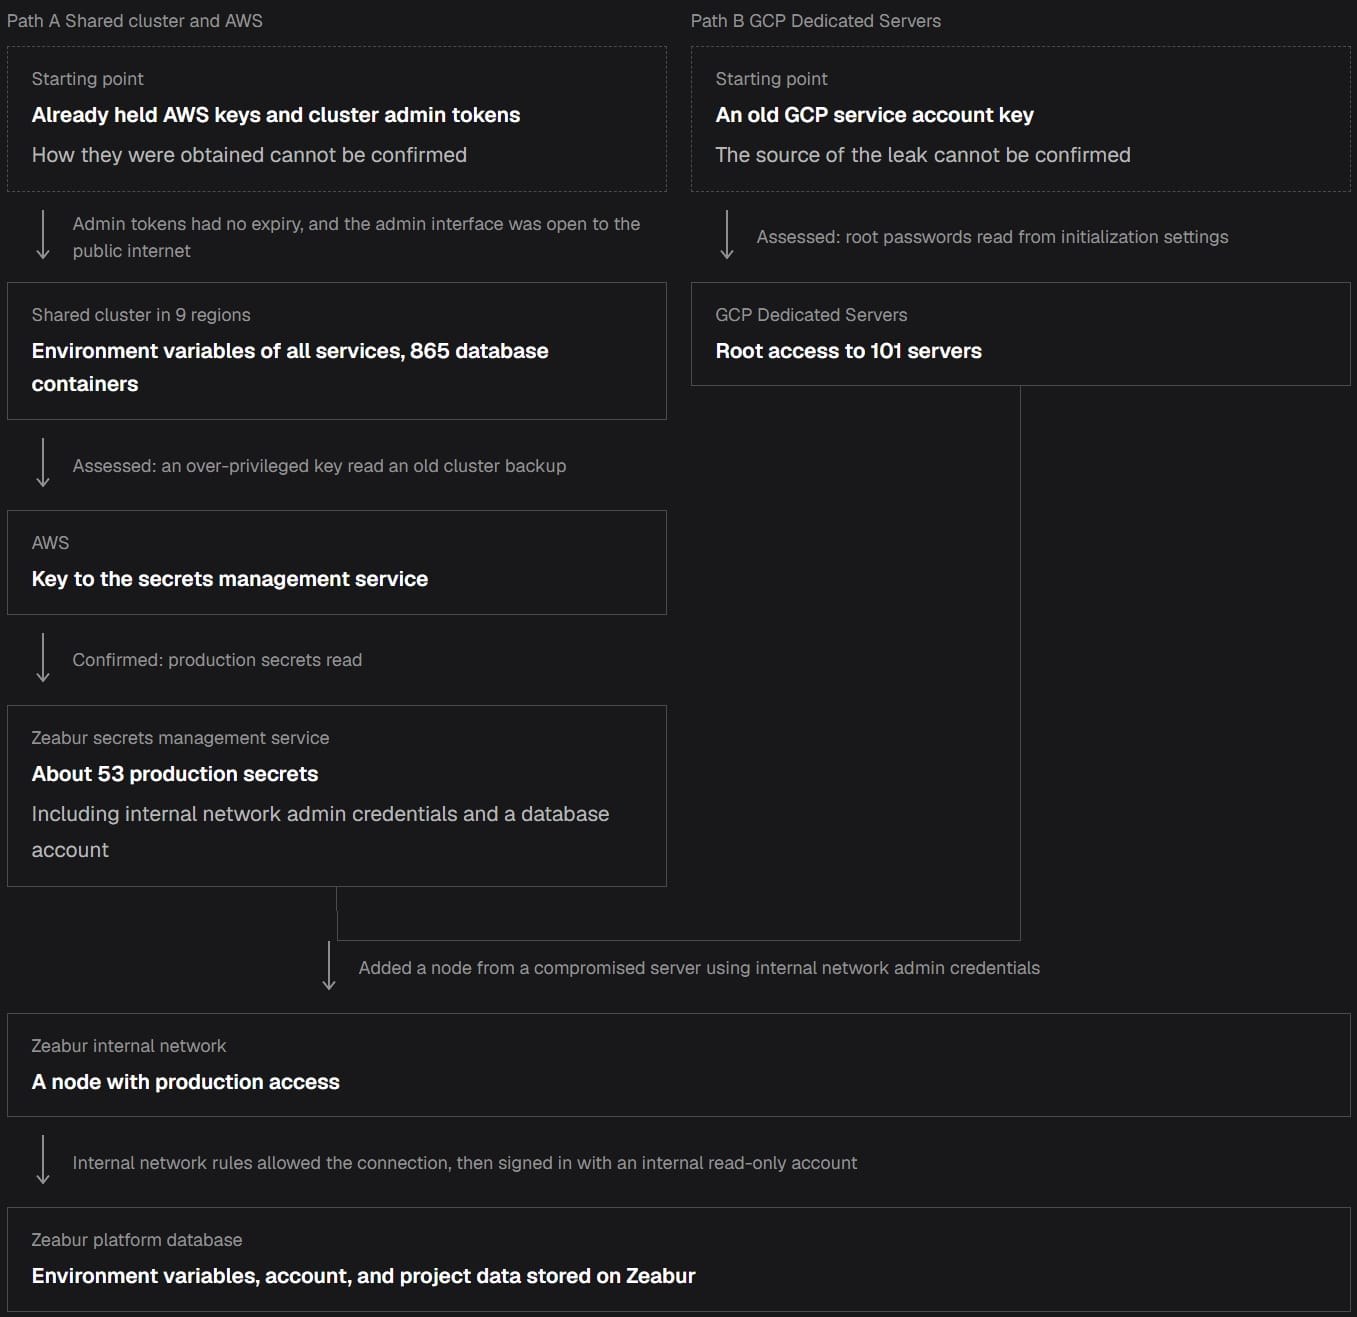
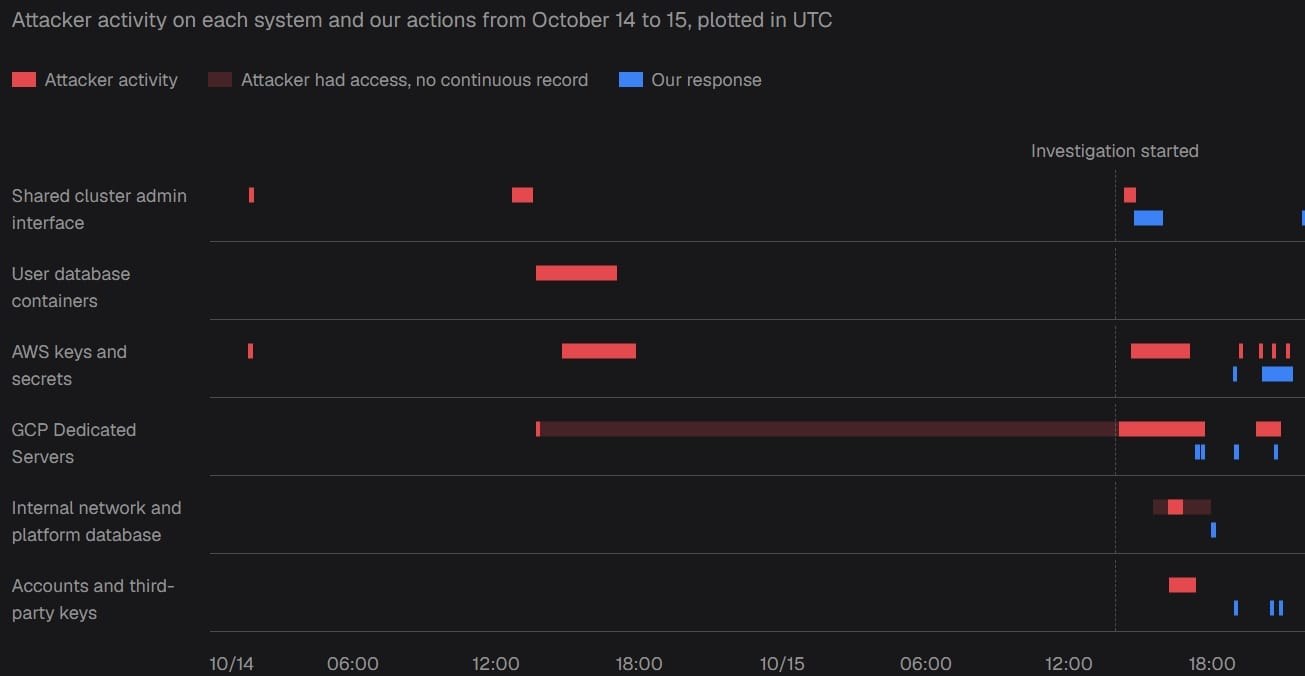
The threat actors leveraged compromised administrator credentials and cloud access keys to penetrate Zeabur's shared hosting infrastructure and dedicated servers, ultimately reaching the production database. Zeabur's statement indicated that "On October 14–15, 2026, an attacker used leaked Zeabur internal credentials to break into the shared cluster, some Dedicated Servers, and Zeabur internal systems, and eventually read the platform database."
Zeabur operates as a platform enabling developers to connect GitHub repositories for automated deployment, database provisioning, HTTPS configuration, and infrastructure administration.
Second incident in two months
This represents the second significant security event for the company in as many months. During August 2026, Zeabur experienced a prior breach when attackers exploited a vulnerability in a customer-deployed NextChat application and subsequently navigated through inadequately segmented internal systems. That incident resulted in AWS credential theft and database access, compromising account information, API keys, and stored secrets.
The October breach proved more extensive in scope, impacting shared clusters spanning nine geographic regions, 321,810 accounts, and approximately 3.2 million environment-variable records.
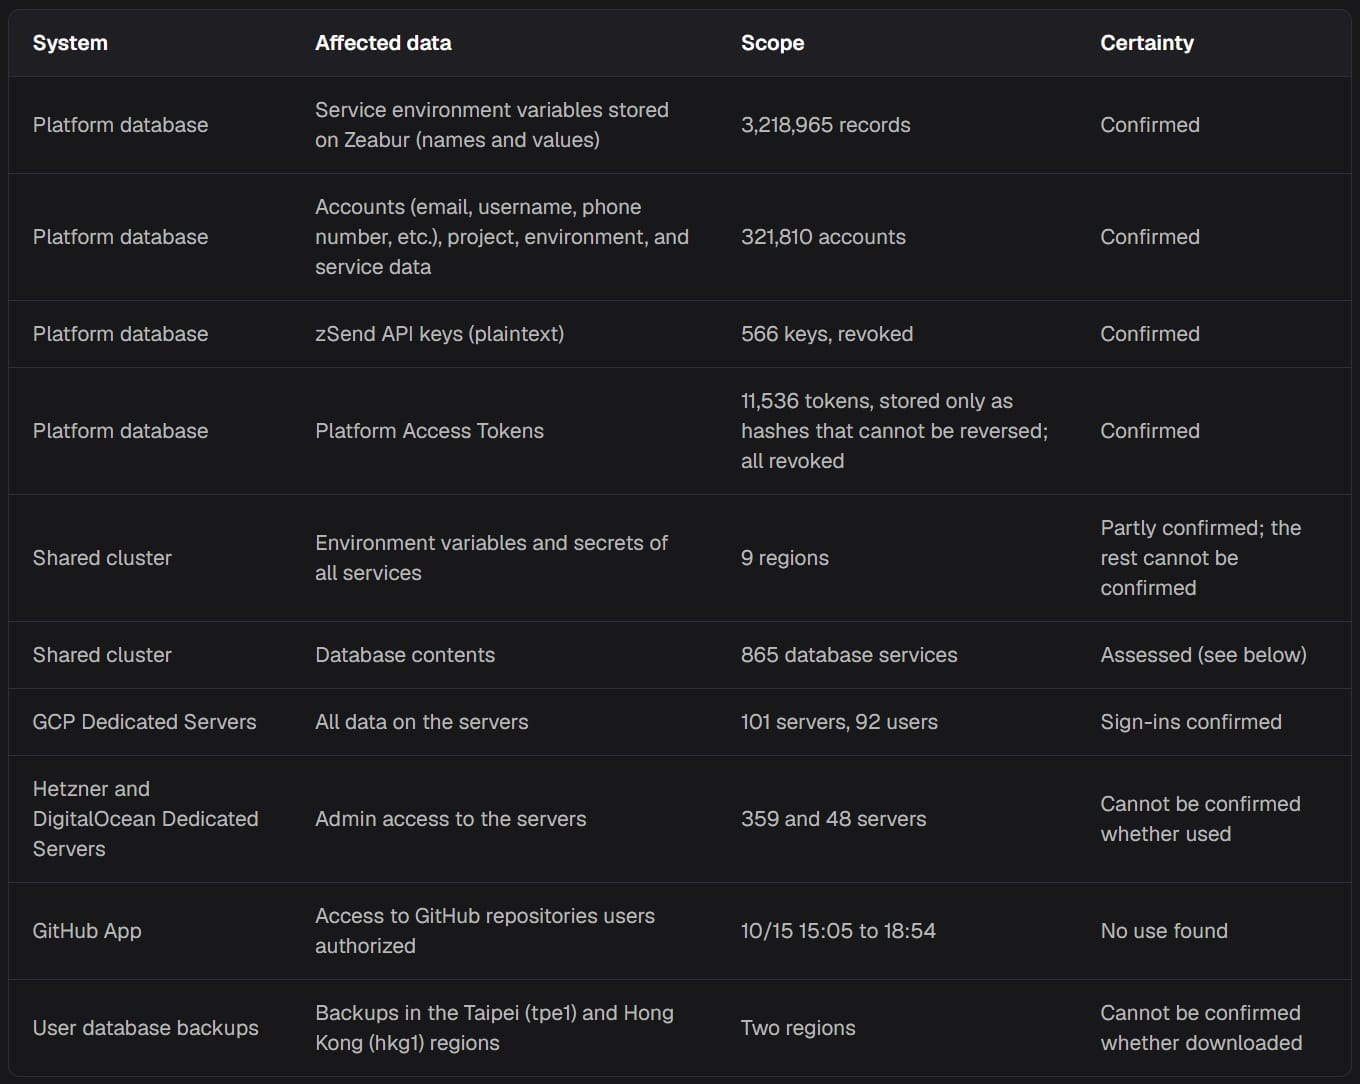
Zeabur documented root-level sign-ins across 101 GCP servers by 92 distinct users, with attackers establishing SSH keys on 50 servers and attaching 16 customer disk copies to their own virtual machines. The company suspects attackers obtained the credentials used in this second attack during the August incident, though definitive confirmation has not been provided.
Security failures and credential management
Beyond the failure to encrypt credentials, Zeabur neglected to rotate all administrator account credentials following the August breach, and administrator portals remained exposed to public internet access. According to Zeabur, "The admin tokens had no expiry, had not been rotated since they were created in January 2024, and were not included in the post-August rotation."
The company has instructed users to immediately rotate all exposed credentials and secrets, revoke all active sessions, and rebuild any compromised GCP servers. Environment variables that had been transferred to customer-controlled servers as part of the August incident response were not affected by this latest database compromise, though hosts that were compromised could potentially still expose them.
Platform shutdown announced
In response to the latest security incident, Zeabur announced this past weekend that it will cease operations, with the shutdown commencing December 1, 2026, and concluding by December 31, 2026.
The company attributed the decision to scaling challenges that have made the platform increasingly difficult to maintain despite 3.5 years of growth and a strong 2026 performance. Zeabur stated: "After the August incident, we spent a long time discussing and struggling with what to do next. Following this latest incident, we reassessed what it would take to keep operating and the responsibilities our team could carry. We ultimately decided to wind down."
Starting December 1, the platform will disable service renewals and pause all running services on shared clusters. By year-end, all dedicated servers will expire and shut down, and shared clusters will cease operation. Zeabur indicated that users may receive additional time for data migration, though specific timelines have not yet been established.