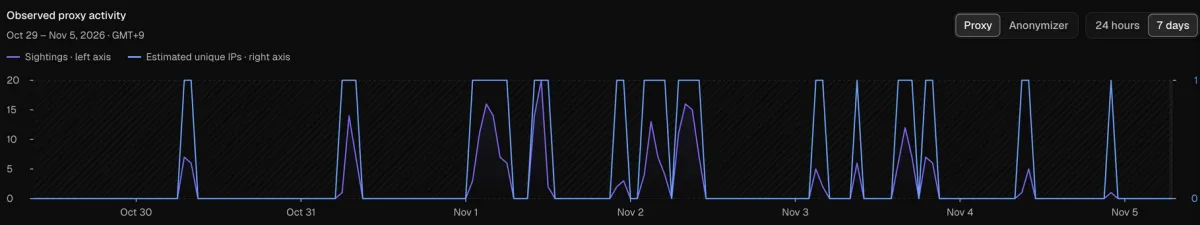
Multiple employees at the White House have been operating computers and mobile devices running residential proxy services, according to security researchers who raised alarms this week. These services allow third parties to rent access to the affected internet addresses. The situation is particularly troubling because one proxy provider involved is a Russian firm whose founder previously ran a hosting operation that served as a staging ground for attacks on election infrastructure in Arizona and Illinois during 2016.
Layer3 Intel identified multiple residential proxy nodes transmitting data from the internet address block assigned to the Executive Office of the President (AS2650). The firm documented consistent proxy activity spanning from October 5 through November 3, with proxy services exiting the White House network 236 times during this window.
Synthient, a company that tracks proxy activity, identified the traffic as originating from multiple Windows 11 machines running Infatica, a proxy application frequently bundled into ostensibly free software for mobile and desktop platforms. Infatica's founder Vladimir Fomenko operates King Servers, a Russian hosting provider that previously hosted six of the eight internet addresses leveraged by Russian state security services to breach election databases in Arizona and Illinois in 2016.
The residential proxy sector encompasses dozens of providers with varying levels of legitimacy, many headquartered in China or Russia. These services fundamentally operate by allowing customers to route traffic through rented internet addresses, masking the true origin of requests and spoofing geographic location. From the perspective of receiving websites, traffic appears to come from the rented address rather than the actual proxy customer.
Layer3 Intel determined that proxy exit nodes from the White House originated from six distinct internet addresses appearing on 26 of the 30 days monitored, with peak activity concentrated between 5 p.m. and midnight.
The scope of the problem extends beyond Infatica alone. Layer3 Intel documented that 28 separate residential proxy services had successfully routed traffic through the White House network.
This is public access. Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services.
Layer3 Intel team
The White House has not yet provided a response to inquiries about the matter.
Broader Security Implications
Residential proxy services have emerged as a significant vector for malicious activity, spanning account compromise, cybercriminal operations, advertising fraud, and large-scale data harvesting for artificial intelligence systems.
These services also pose substantial security hazards. Late 2025 saw the discovery of widespread exploitation of a vulnerability affecting these services, enabling attackers to scan proxy endpoints' local networks for systems vulnerable to malware infection. In January 2026, numerous proxy providers were compelled to deploy patches after Synthient Founder Ben Brundage demonstrated how criminals were leveraging vulnerabilities in residential proxy infrastructure to commandeer devices within the local networks of unsuspecting users.
Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte, that means for less than a dollar you can gain access into some of the most confidential and trusted networks. The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes.
Ben Brundage, Synthient Founder
A common vector for proxy infiltration involves application developers embedding software development kits from residential proxy networks into their applications. This monetization approach generates modest revenue per installation while introducing security risks to end users.
Despite the dangers, residential proxies remain prevalent across government and corporate infrastructure. A January 2026 webinar by Spur, another proxy tracking service, identified residential proxies operating within nearly 300 government networks, 318 utility companies, 166 healthcare organizations or hospitals, and 141 financial services and banking firms. Infoblox, a security vendor, reported in an earlier blog post that 65% of its customer base was accessing domains associated with residential proxies.