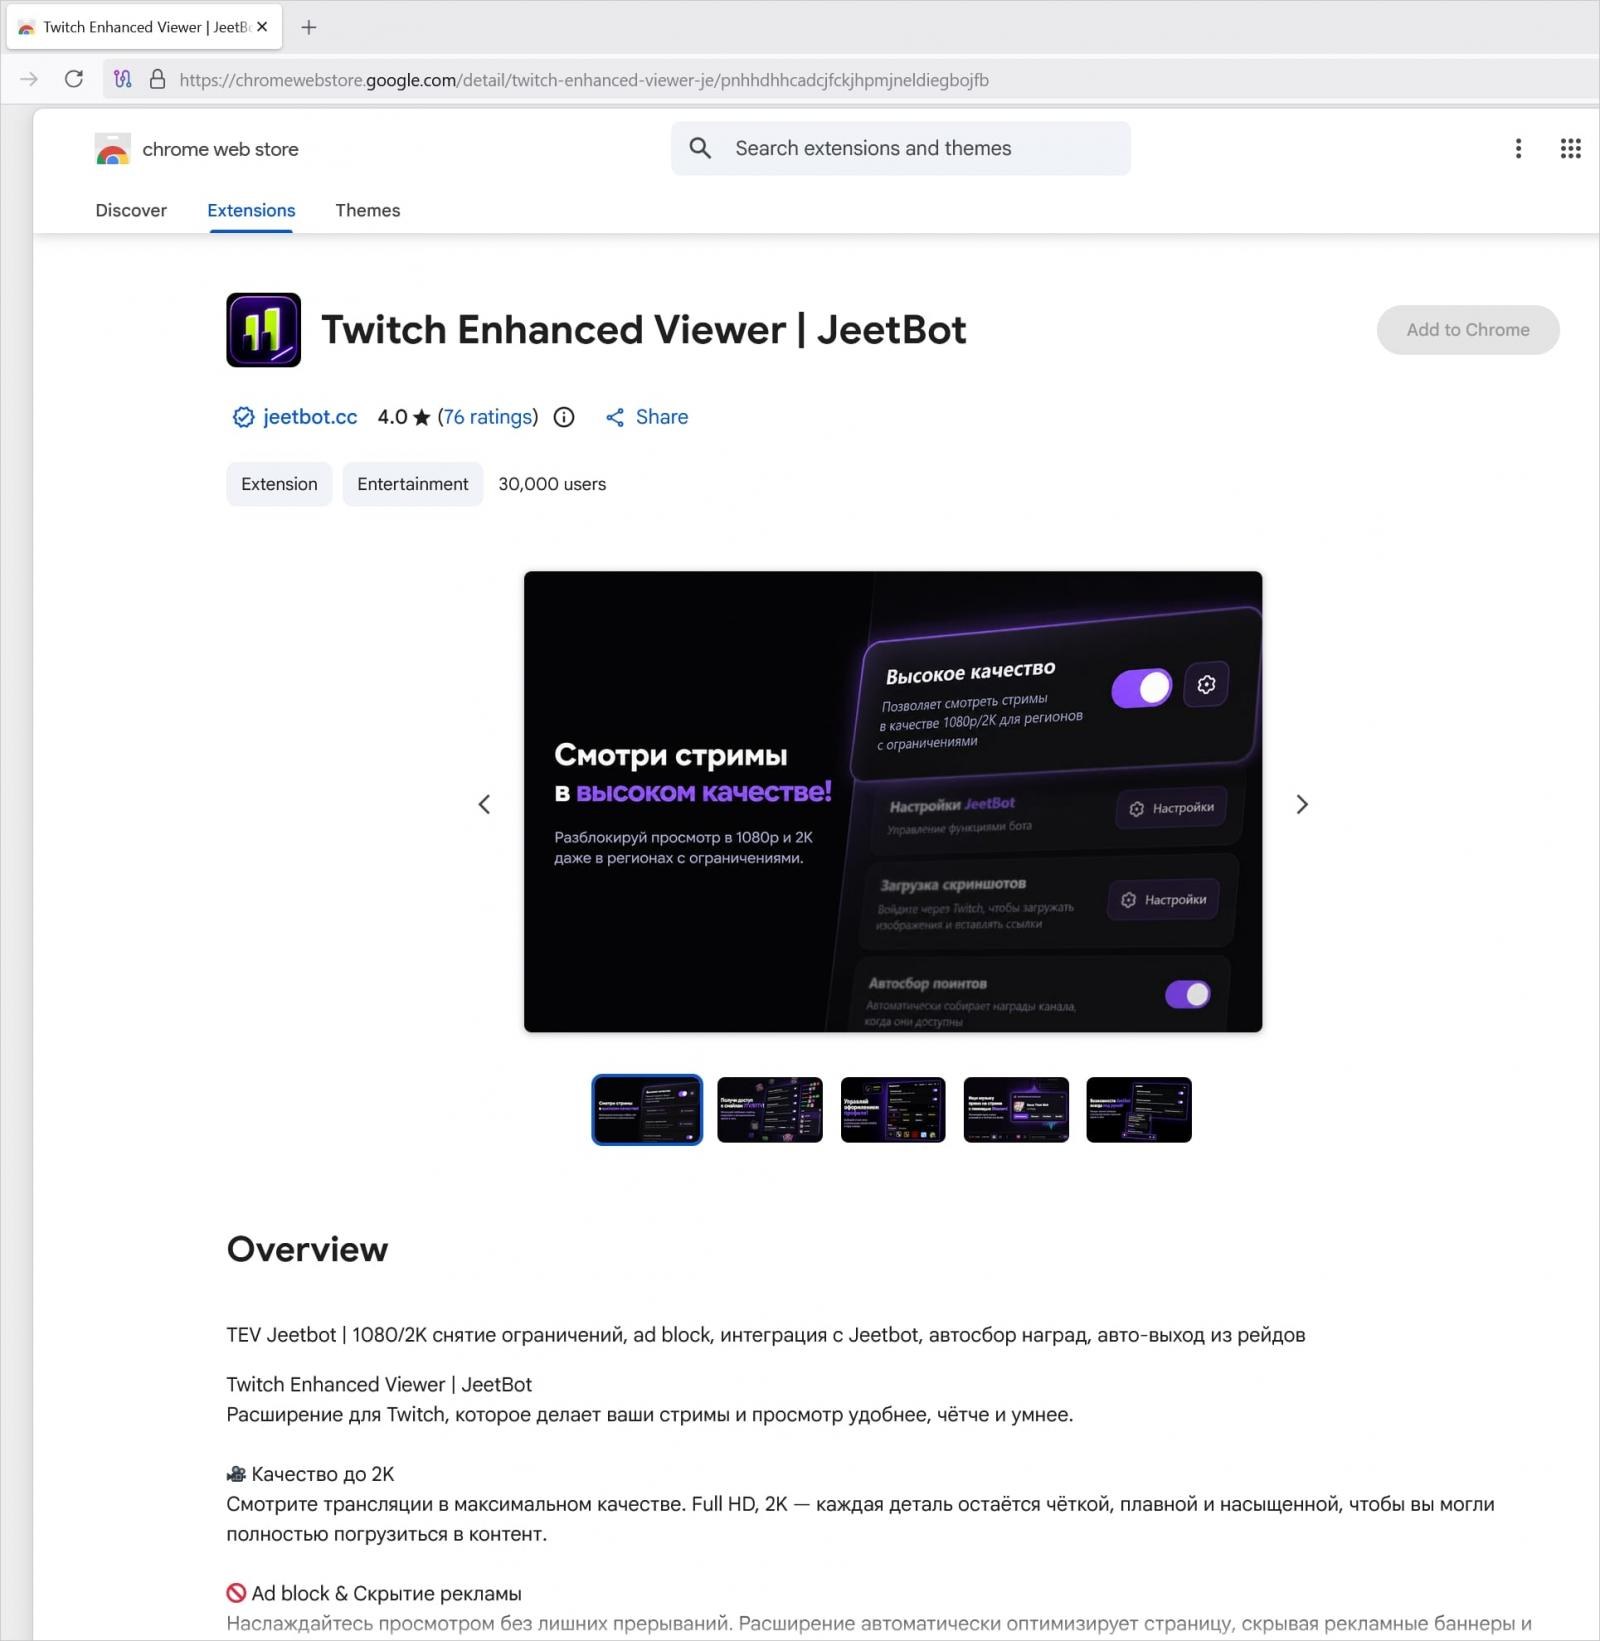
A widely distributed browser extension marketed as a Twitch enhancement tool is funneling users' authentication credentials to an external service. Twitch Enhanced Viewer | JeetBot, distributed through both the Chrome Web Store and Firefox Add-Ons marketplace, has accumulated more than 30,000 installations while promising features including ad blocking, forced 1080p video playback, region restriction bypass, and automated channel-point collection.
Security researchers at Socket uncovered that the extension intercepts the authorization header from Twitch's web client, extracts the user's OAuth token, and routes it through proxy infrastructure controlled by JeetBot, a Russian-language service offering streaming and chatbot tools for Twitch, Kick, and VK Live platforms.
Tokens Exposed in Plain Text Logs
The mechanism used to transmit credentials creates a significant exposure risk. Current versions of the extension append the OAuth token directly to proxy requests as an auth= URL parameter. This placement in the query string means the token appears in cleartext within the proxy server's request logs, making it trivial for the service operator to retrieve.
When the extension redirects Twitch's video playlist request (to usher.ttvnw[.]net) through that proxy, it appends the token as an &auth= query parameter. Because the token is placed in the URL query string, it is written in cleartext into the proxy server's request logs.
Socket
This token exfiltration happens for every Twitch channel a user watches, with a notable exception: the extension's code contains a hardcoded list of ten Russian-language channels that bypass this process.
Earlier Versions Used More Explicit Theft
Socket's analysis revealed that previous iterations of the extension employed even more direct credential-theft tactics. In the Firefox Add-Ons store listing, the developer included a disclaimer acknowledging this earlier behavior:
Previous versions of the extension transmit your OAuth-twitch token to our server. This is necessary for the stream to run in 1080/1440p.
Extension developer, machine translated
Meanwhile, the Chrome Web Store listing contains a privacy declaration stating that the developer "disclosed that it will not collect or use your data." The same declaration purports to prohibit selling user information to third parties except in approved circumstances, transferring data outside the product's "core functionality," or using it "to determine creditworthiness or for lending purposes."
Remediation Steps
At the time of reporting, the extension remained available in both distribution channels. BleepingComputer contacted JeetBot via the email address listed in the Chrome Web Store but received no response before publication.
Socket researchers recommend that affected users take immediate action to protect their accounts. Users should uninstall the extension, log out of all active Twitch sessions, and then log back in to invalidate any tokens that may have been transmitted to the proxy servers. Developers integrating third-party services are advised to avoid routing requests containing authentication headers or tokens through external servers.