The ShinyHunters extortion collective has penetrated Clop's (also known as Cl0p) ransomware operation's data leak site on Tor, replacing its contents with defacement and asserting they have obtained server data and the private keys for the onion service.
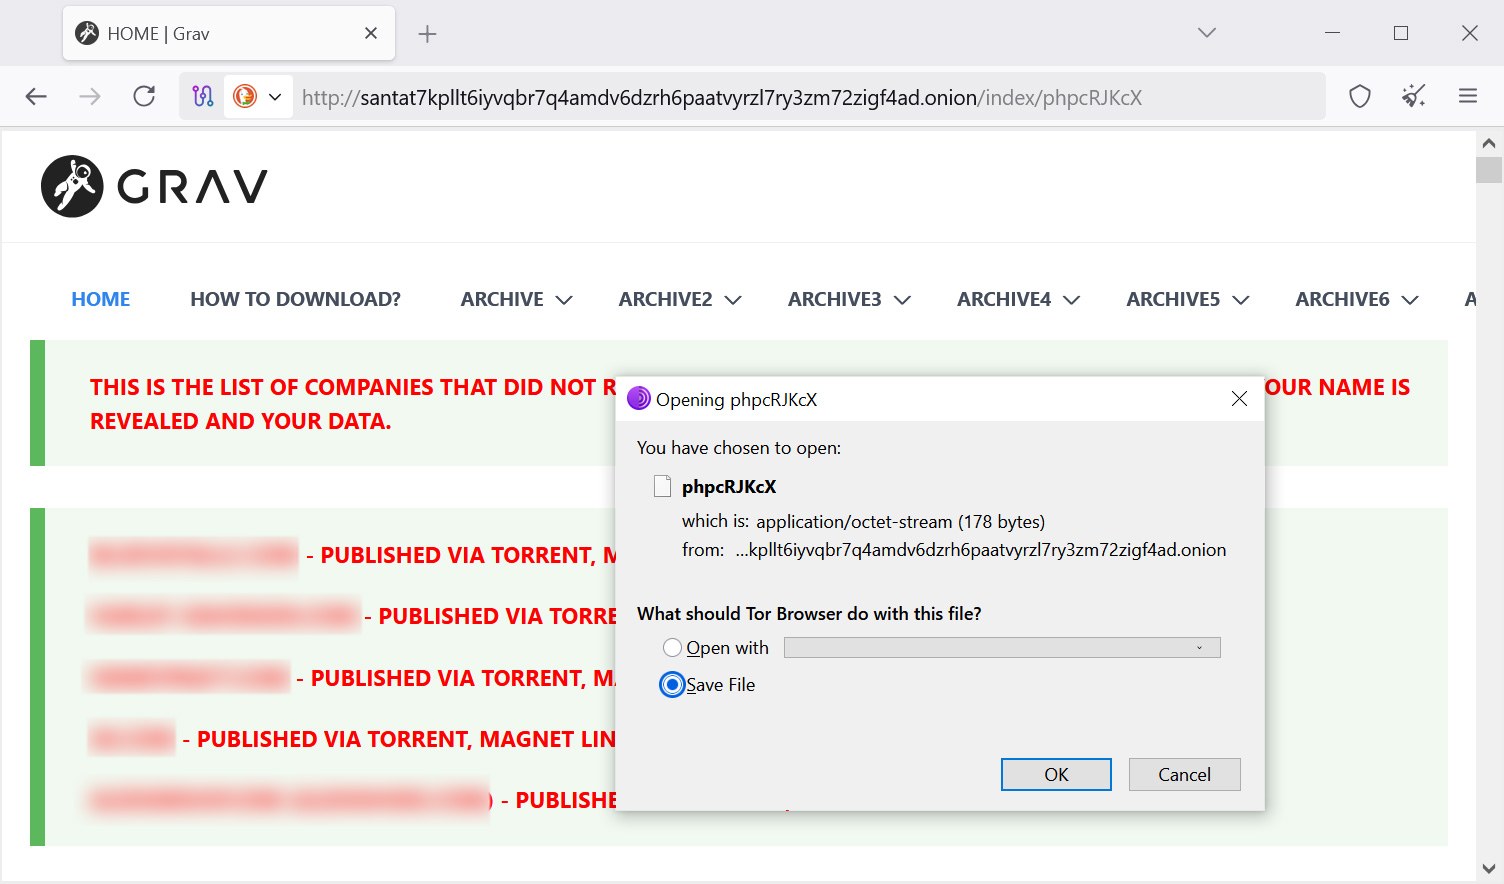
According to ShinyHunters, the intrusion started Friday evening by exploiting an unauthenticated file upload flaw in Grav CMS. The group uploaded a text file containing a message directed at the Clop ransomware operation, cautioning them against making threats and providing a link to ShinyHunters' own leak site.
THIS SITE HAS BEEN PWN3D BY SHINYHUNTERES #Skids10p - Maybe don't try to threaten us next time
message in the uploaded file
BleepingComputer verified that the file was successfully placed on Clop's server and remained downloadable from the ransomware gang's Tor infrastructure. Hours afterward, ShinyHunters informed BleepingComputer that they had "completely defaced" the Clop site.
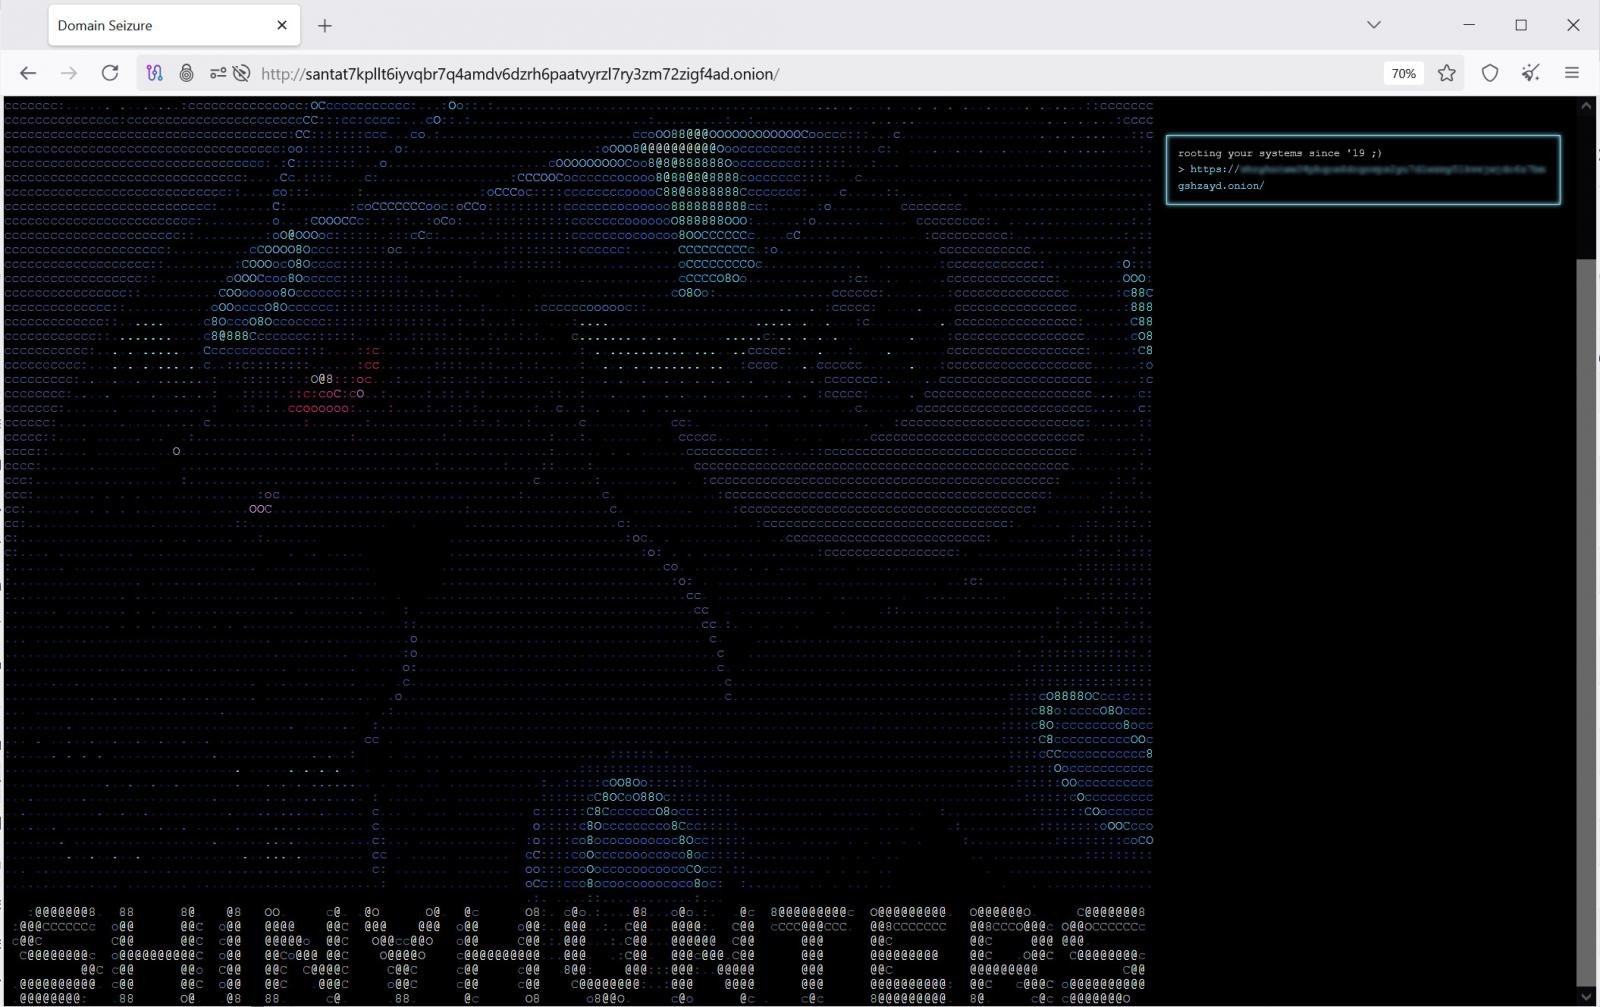
The compromised site now displays ASCII art depicting Umbreon, the Pokémon character that serves as ShinyHunters' emblem. The defaced page includes a hyperlink to the group's Tor site and the text "rooting your systems since '19 ;)". According to ShinyHunters, the altered page continues to be served from Clop's own infrastructure.
Alleged data theft
ShinyHunters claims to have obtained "full access" to the server and exfiltrated source code, Grav CMS plugins, system logs, and additional data. The group stated to BleepingComputer: "The data we stole includes source codes, gravCMS plugins, and other things. We are still downloading and reviewing them."
The attackers also assert they obtained all files from the /var/log directory, which typically contains system activity records, authentication logs, and potentially IP addresses of individuals who accessed the server.
ShinyHunters further claims possession of the private keys that secure Clop's Tor onion service. The threat actors stated: "We have their onion keys. So if they kick us out it wouldn't matter at all because we control the private keys to host the same exact onion URL."
If accurate, these keys would permit the threat actors to operate a Tor site using Clop's existing onion address from their own infrastructure. BleepingComputer has independently confirmed the defacement and the earlier uploaded file but has not independently verified ShinyHunters' assertions regarding stolen server logs, source code, or Clop's onion private keys.
When asked about their intentions for the stolen information, ShinyHunters responded: "Going to extort them." The group intends to post a message on its leak site directing Clop to make contact within 72 hours.
Cybersecurity researcher VXDB noted that the Umbreon artwork currently displayed on Clop's leak site matches the imagery used in an August 2020 defacement of the HackForums website, which ShinyHunters also claimed responsibility for at that time.
Dispute between criminal organizations
ShinyHunters characterizes the breach as retaliation for threats allegedly issued by a Clop representative amid an ongoing conflict between the two criminal groups. ShinyHunters asserts that a Clop representative threatened to identify group members and made violent threats following ShinyHunters' interference with a Clop data theft operation.
The conflict traces back to Clop's 2025 Oracle E-Business Suite data theft campaign. In October 2025, Clop exploited multiple Oracle E-Business Suite vulnerabilities, including a zero-day flaw designated CVE-2025-61882, to extract data from organizations for extortion purposes.
Around the same period, threat actors identifying themselves as "Scattered Lapsus$ Hunters," which includes ShinyHunters, released a proof-of-concept exploit that Oracle subsequently confirmed matched the exploit deployed in the Clop attacks. ShinyHunters told BleepingComputer the exploit originally belonged to them and that Clop obtained it without permission.
ShinyHunters contends that tensions intensified following the Oracle campaign, with a Clop representative allegedly making threats against group members. ShinyHunters stated: "During the Oracle EBS campaign they ran and stole from me last year, someone from cl0p personally messaged me and said, and I quote (translated from Russian): I have more money than you and all of your people combined, I'll kill you soon."
BleepingComputer has not independently verified these allegations. The outlet has reached out to Clop regarding the breach and the claims made by ShinyHunters and will provide updates if a response is received.