A team at Eye Security identified and patched a severe vulnerability in Time4Popcorn, an unmaintained fork of the Popcorn Time BitTorrent application, by leveraging the same insecure update channel that exposed the flaw. The researchers gained control of the update domain and deployed remediation code to disable the vulnerable updater on approximately 2 million Windows machines and hundreds of thousands of macOS systems before transferring domain ownership to The Shadowserver Foundation.
The flaw, designated CVE-2026-30612, stemmed from the Time4Popcorn updater's reliance on unencrypted HTTP connections to the domain popcorntimeupd.xyz and its failure to validate digital signatures on downloaded executables. An attacker with the ability to intercept or control traffic to this domain could inject malicious code that would run with SYSTEM-level privileges on Windows or root access on macOS.
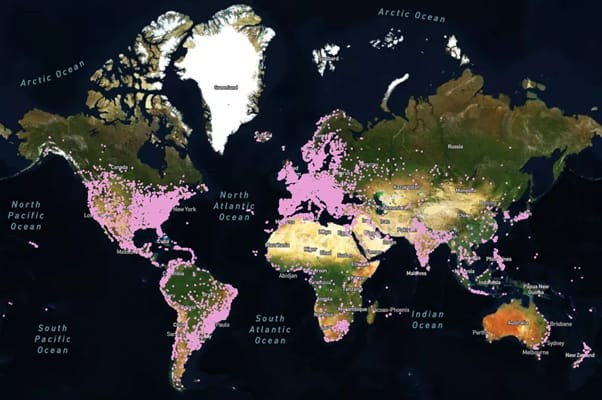
Eye Security discovered the vulnerability after registering the abandoned update domain and observed substantial traffic from both consumer and institutional networks. The researchers logged up to 3 million connections from Windows clients and approximately 350,000 from macOS devices, originating from residential internet service providers as well as corporate, government, and military networks. Evidence suggested most installations were dormant rather than actively in use.
If we were able to send an update, we could potentially get code execution on millions of systems. The impact would be severe if this were to fall into the wrong hands.
Eye Security
Remediation Campaign
Starting in November 2025, Eye Security executed a remediation operation spanning four months. The researchers crafted a payload that disabled the updater service without collecting system data, transmitting telemetry, or modifying files on affected machines. During testing, the team had to refine the payload to prevent antivirus software from flagging the remediation code itself.
The campaign achieved substantial results: approximately 2 million systems downloaded the remediation update. By March 1, 2026, traffic to Eye Security's update domain had declined by 98 percent, indicating successful suppression of the vulnerable updater across the majority of affected machines. The researchers subsequently registered 14 additional domains tied to the Time4Popcorn service to prevent their misuse.
Remaining Risks
Despite the successful remediation effort, significant security concerns persist for Time4Popcorn users. Android installations remain vulnerable because the update mechanism requires user interaction, preventing remote disabling of the updater on mobile devices. Additionally, the application relies on a heavily outdated Chromium engine from 2014 that lacks sandbox protections, creating additional attack surface for exploitation.
The researchers recommend that users completely uninstall Time4Popcorn from their systems rather than relying on the remediation patch alone.