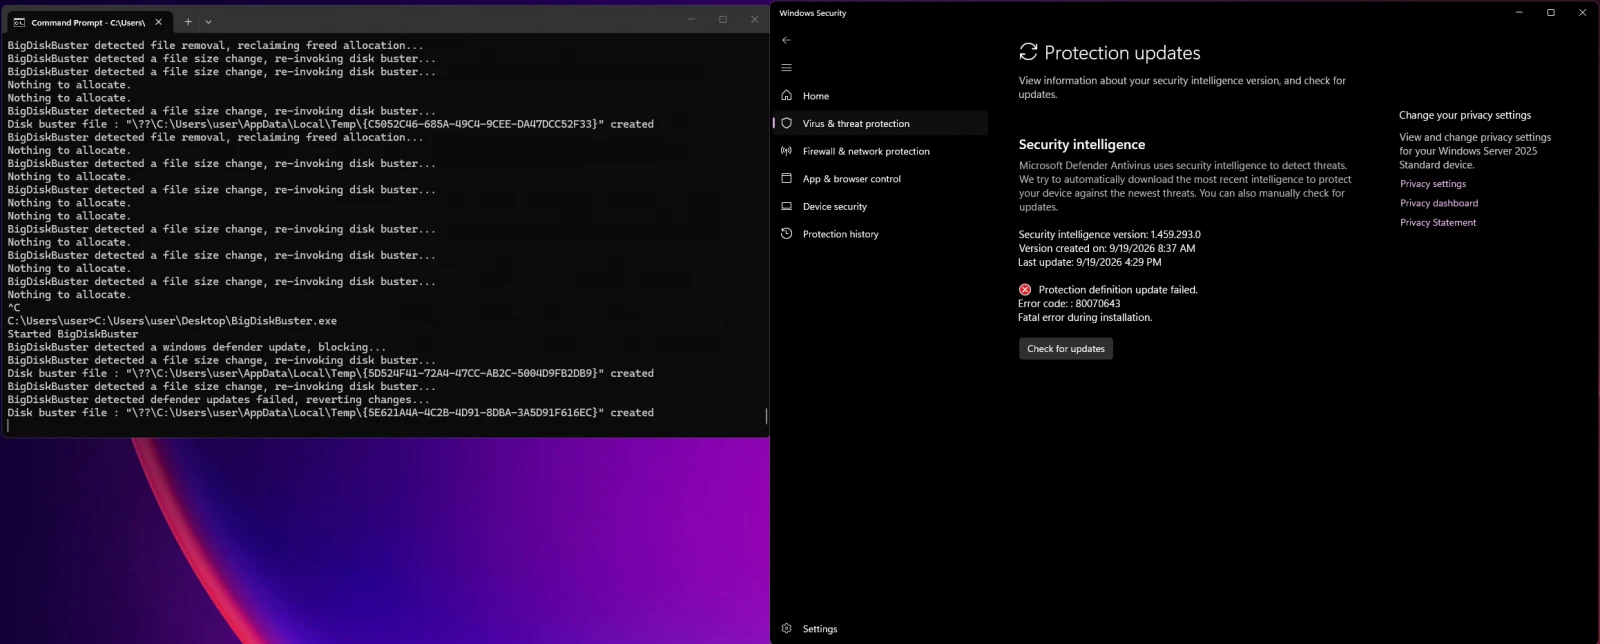
Over the weekend, researcher Abdelhamid Naceri, who operates under the alias Nightmare Eclipse, unveiled a previously unknown vulnerability affecting Microsoft Defender that prevents antivirus updates from being deployed.
Naceri designated the flaw as BigDiskBuster and noted its similarity to UnDefend, another Defender zero-day he disclosed in April that enabled standard-privilege users to stop definition updates from being installed.
According to the researcher, BigDiskBuster affects all currently supported Windows versions and requires continuous background execution to interrupt Defender's update mechanism. "Made a funny tool, completely denies defender from updating so you're stuck with your current version if the tool is running in the background," Naceri stated.
In a more detailed description, Naceri elaborated: "This proof of concept is similar to UnDefend, it prevents windows defender from performing platform/signature updates. Seems to work on all supported windows versions but PoC is a bit buggy and needs some rewritting but you get the idea."
Since April 2026, Naceri has disclosed nearly a dozen zero-day vulnerabilities as part of an ongoing conflict with Microsoft stemming from what the researcher characterizes as an unfair termination in March 2025.
Fourteen days prior, Naceri unveiled ShieldCrash, another Defender zero-day granting SYSTEM-level access, released immediately following Microsoft's monthly Patch Tuesday updates. According to Naceri, ShieldCrash circumvents ShieldBreak, a Defender privilege escalation vulnerability that Microsoft patched one week earlier. ShieldBreak itself bypassed RoguePlanet, a Defender flaw Naceri disclosed in June that Microsoft addressed in July.
Throughout 2026, Naceri's disclosures have encompassed LegacyHive, BlueHammer, RedSun, YellowKey, GreenPlasma, MiniPlasma, and UnDefend, targeting Microsoft Defender, BitLocker, and additional Windows components.
Microsoft's initial response included threats of legal action against parties engaged in "malicious activity causing real harm" to its customer base, prompting segments of the security community to interpret this as a direct warning directed at Naceri.
While Microsoft has remediated certain vulnerabilities disclosed by Naceri—including ShieldBreak, RoguePlanet, YellowKey, GreenPlasma, and MiniPlasma—several other reported security issues remain unpatched.
A Microsoft representative declined to provide immediate comment when contacted by BleepingComputer regarding the BigDiskBuster denial-of-service vulnerability.