Threat actors are conducting reconnaissance against deployments running Rejetto HFS, targeting CVE-2026-61500, a flaw that permits session forgery, account takeover, and remote code execution. VulnCheck's VP of Security Research Caitlin Condon reported on LinkedIn that the firm's Canary Intelligence honeypots detected probes aimed at this vulnerability during the past weekend.
According to Condon's observations, the scanning activity appears limited in scope, originating from a single China Telecom IP address and targeting systems in Japan and the United States.
Rejetto HFS (HTTP File Server) is a free, open-source file-sharing application available for Windows, Linux, and macOS that enables users to host their own file-sharing infrastructure.
Technical Details of the Vulnerability
The flaw, disclosed on July 13, 2026, stems from improper session-cookie signing practices and information leakage in Rejetto HFS versions 3.0.0 through 3.2.0. The vulnerability was patched in version 3.2.1.
Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs of the same generator to unauthenticated clients during login. A remote attacker can collect a small number of login responses, reconstruct the generator's state, recover the signing key, and forge a valid administrator session cookie, leading to full administrative access and remote code execution via the server_code configuration feature.
NIST NVD
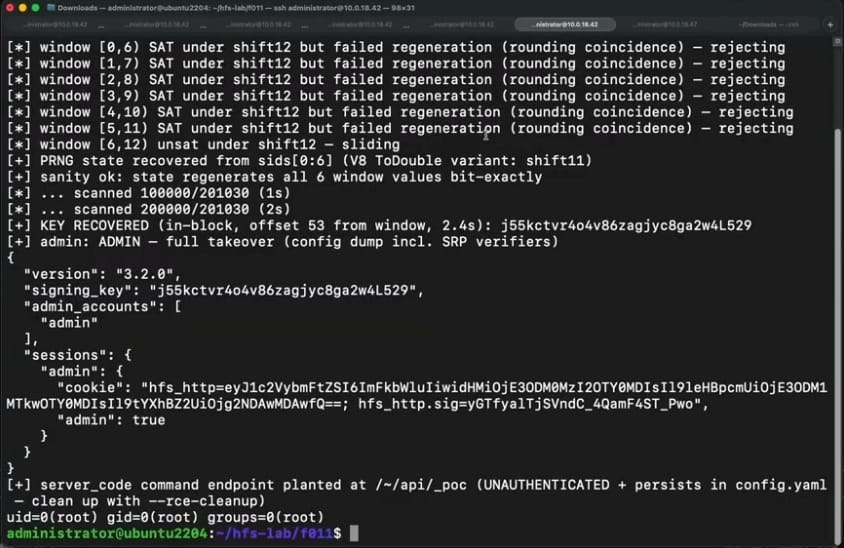
Researchers at Horizon3 identified the vulnerability using Anthropic's Mythos model, which detected both the weak key generation mechanism and the information leak that made key recovery possible. The team published detailed technical analysis and a proof-of-concept exploit on September 30, 2026.
Mythos didn't just flag the insecure PRNG in isolation – it simultaneously identified that the application leaked raw Math.random() outputs through a separate code path, recognized those two facts as a chain, and determined the leak produced exactly the observations needed to make state recovery feasible.
Horizon3
The Horizon3 exploit demonstrates how attackers can leverage HFS's native support for executing custom server-side JavaScript code to achieve remote code execution on compromised systems.
Potential Impact and Remediation
The public release of technical exploitation details likely triggered the observed scanning activity. Successful attacks could result in unauthorized file access, data theft, file deletion, malware installation, or lateral movement into internal networks.
VulnCheck has not disclosed evidence of successful exploitation attempts or post-compromise activity at this time.
Administrators running Rejetto HFS should upgrade immediately to version 3.2.1 or, preferably, to the latest stable release, version 3.3.4.