The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced Wednesday that ransomware operators have begun exploiting a critical vulnerability in JetBrains TeamCity that received patches in July. The flaw, designated CVE-2026-63077, was addressed by JetBrains on July 25 for TeamCity On-Premises versions 2025.11.7 and 2026.1.3 as a critical authentication bypass that permits attackers with HTTP(S) connectivity to run arbitrary operating system commands.
According to JetBrains, "An unauthenticated attacker could exploit the vulnerability via the TeamCity agent polling protocol to bypass authentication checks and execute arbitrary operating system commands with the privileges of the TeamCity server process." The vendor further warned that "Depending on the privileges granted to the TeamCity server process, a successful attack could expose TeamCity data, configurations, and stored credentials, modify server state, and potentially compromise the integrity of build artifacts and downstream CI/CD pipelines."
CISA added CVE-2026-63077 to its Known Exploited Vulnerabilities Catalog on August 5, mandating that U.S. federal agencies remediate their systems within three days. JetBrains confirmed active exploitation in the wild on August 7, releasing indicators of compromise and recommending that customers unable to deploy patches immediately restrict access to trusted networks only.
Ransomware gangs now targeting the flaw
Although CISA had not disclosed specific ransomware attack details when it first flagged the vulnerability, the agency updated its KEV catalog again on Wednesday to indicate that ransomware operators are now abusing CVE-2026-63077. Since October 2023, CISA has designated four separate TeamCity security issues as exploited in active attacks, with all four subsequently appearing in ransomware campaigns.
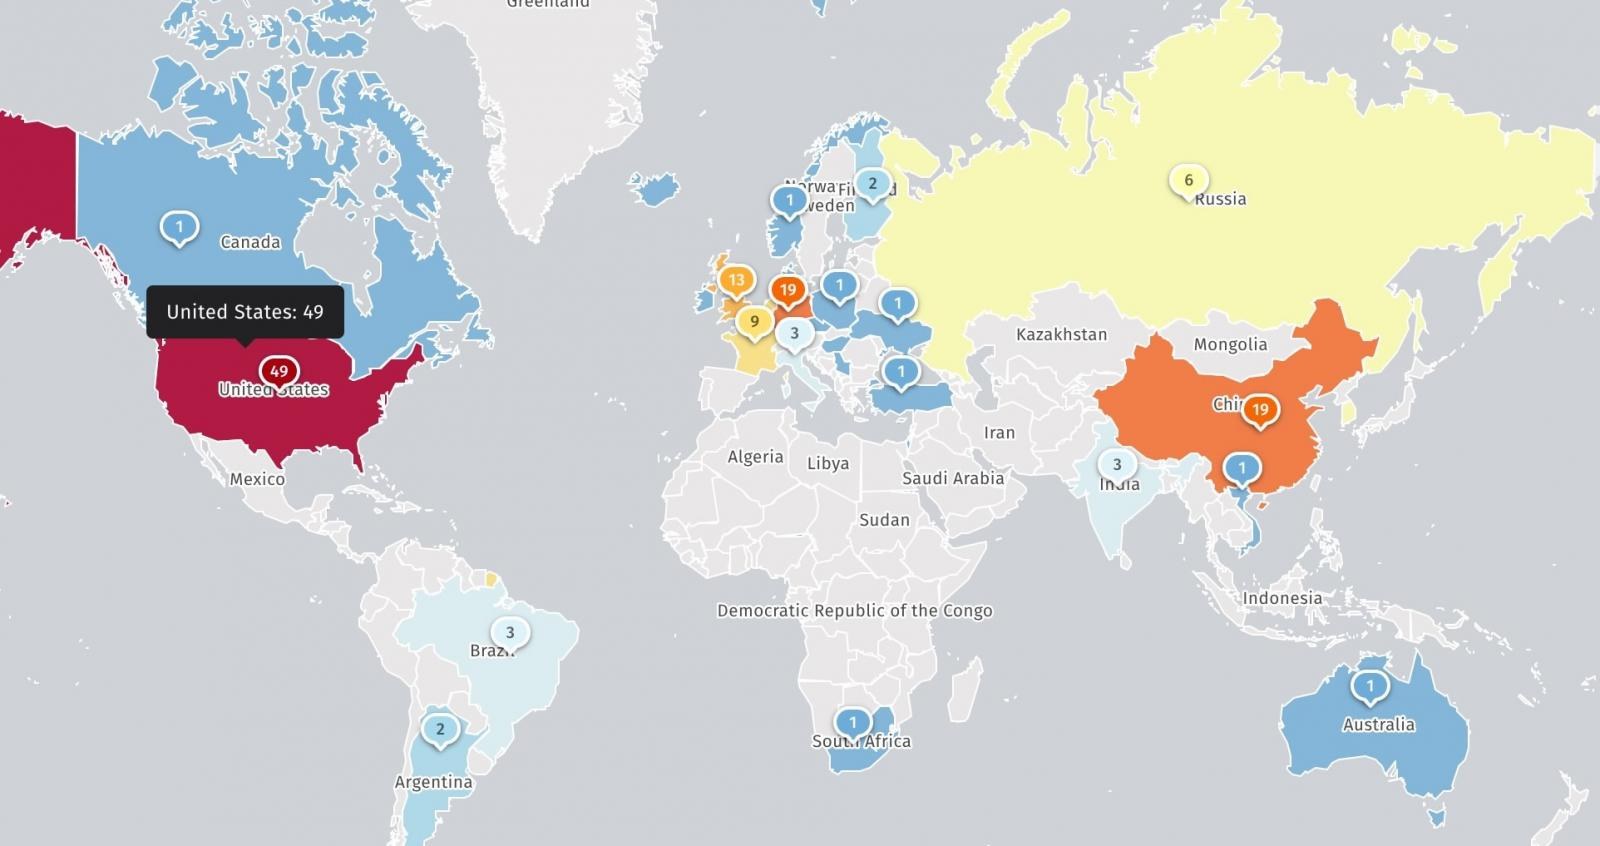
Security monitoring organization Shadowserver is currently tracking approximately 160 unpatched TeamCity servers exposed to the CVE-2026-63077 vulnerability, a significant decline from the initial 700 Internet-accessible systems identified as vulnerable immediately following the patch release.
Given that both state-sponsored hacking groups and ransomware operators have repeatedly weaponized TeamCity vulnerabilities, infrastructure teams should prioritize patching Internet-exposed instances without delay. In October 2024, U.S. and U.K. authorities cautioned that APT29 operatives, attributed to Russia's Foreign Intelligence Service (SVR), were conducting mass-scale attacks against vulnerable JetBrains TeamCity and Zimbra deployments.
TeamCity functions as a Continuous Integration and Continuous Deployment (CI/CD) platform enabling software developers and DevOps teams to streamline code building, testing, and deployment workflows. JetBrains reports that more than 30,000 DevOps teams operate TeamCity across numerous enterprise organizations, including Citibank, Amazon Games, Tesla, and Samsung.