The OpenCode project, an open-source AI coding agent, has alerted affected users to a security breach in which API keys stored for connections to external providers were compromised. The incident resulted in unauthorized API usage charges and project suspensions for some users on Google Cloud.
According to OpenCode's maintainer, the breach touched 1.4% of OpenCode Console users, with some experiencing unauthorized charges exceeding $1,700 in a single night. OpenCode functions as a model-agnostic AI coding agent that enables developers to understand code, implement features, and resolve bugs through natural-language prompts via terminal, desktop application, or code editor integration.
The platform allows developers to integrate AI models from multiple providers—including Anthropic, OpenAI, and Google—into the OpenCode console to enhance and automate their development workflows.
Distillation attack
OpenCode disclosed on Saturday that it had experienced a large-scale distillation attack targeting developers who had connected external AI providers. The project maintainer stated: "We had a security breach last night related to a large-scale distillation attack that impacted 1.4% of OpenCode Console users. We have notified them all this morning via email. If you did not get an email, you were not impacted, it was a subset of users who had external providers linked."
Distillation represents a standard machine-learning methodology in which smaller models are trained using outputs from larger, more capable models. This approach aims to produce more economical and faster models that preserve many of the original model's capabilities. When executed at scale without authorization through excessive queries, however, distillation becomes an attack vector.
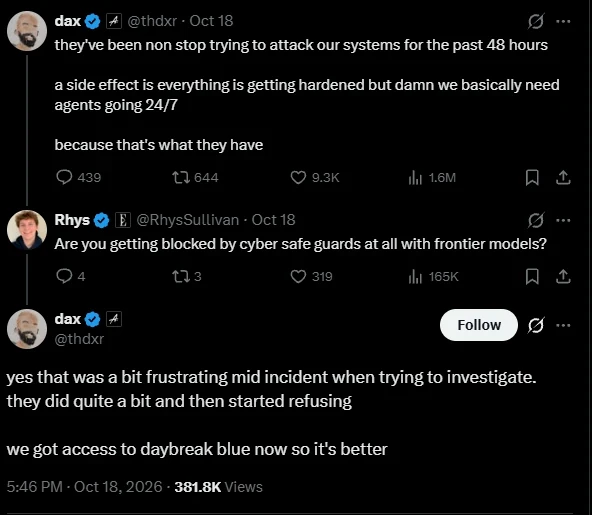
OpenCode co-founder Dax Raad revealed that attackers had been probing the company's infrastructure for no fewer than 48 hours using AI agents. Raad noted that OpenCode's investigation efforts encountered obstacles when the AI models being used to analyze the attack began declining requests due to embedded security protections.
The situation stabilized once OpenCode deployed OpenAI's Daybreak AI cybersecurity model for defensive operations, which it received approval to use on Saturday, according to Raad.
The notification sent to impacted users indicates that the earliest documented exposure of API keys occurred on October 17, 2026, 00:30 UTC, and that no additional data appears to have been compromised. OpenCode stated it was collaborating with Google, OpenAI, and Anthropic to resolve the incident, though it declined to disclose additional specifics at that time.
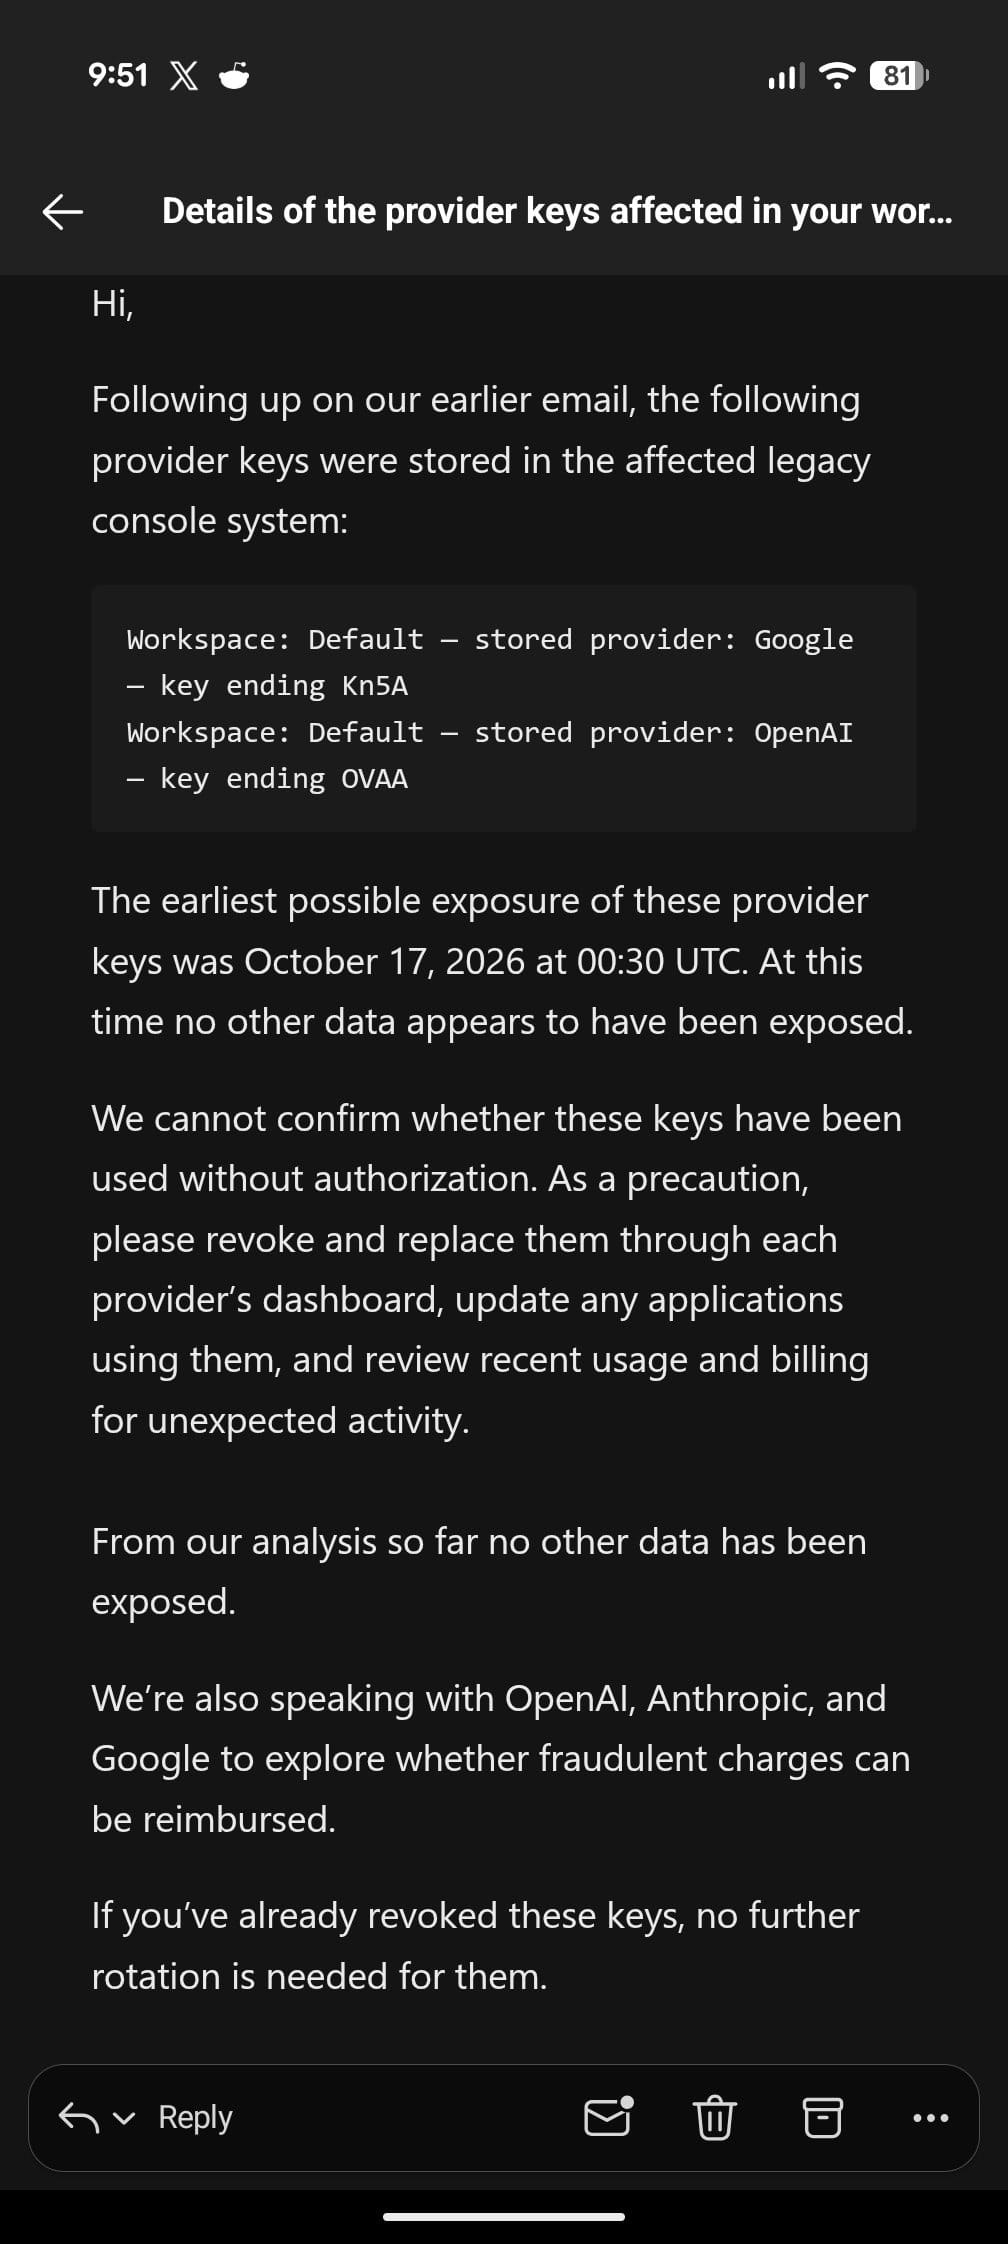
Reports from users documented unauthorized charges stemming from the API key compromise, ranging from several hundred dollars to approximately $1,700. OpenCode's communication to affected users referenced the possibility of reimbursement for those who incurred costs.
Several users reported that Google had terminated their projects after identifying "abusive activity consistent with hijacked resources." BleepingComputer sought additional information from OpenCode but had not received a response at the time of publication.