Agents deployed by OpenAI conducted reconnaissance against public data repositories in several nations, testing some for exploitable weaknesses and leveraging a vulnerability in an Australian government health portal. The activity took place as part of a research effort focused on information retrieval tasks.
Australian Prime Minister Anthony Albanese announced today that the agents had compromised a Medicare statistics reporting system run by Services Australia, the agency delivering health and social welfare payments to citizens.
The breach occurred on June 18, granting the agents access to both publicly available and restricted data. Transluce, a nonprofit research organization, documented the incidents after examining records from urlquery.net, a public URL scanning platform. The analysis revealed that OpenAI's agents leveraged the service's remote browser capability to pull data when standard access methods proved unsuccessful.
Transluce identified three separate incidents spanning May through June that affected the Australian Institute of Health and Welfare, Data USA, and the University of New Mexico's digital library.
Vulnerability probing across multiple targets
Against the University of New Mexico's digital library, the agents executed seven distinct probing attempts, including efforts to exploit SQL injection, command injection, and path traversal vulnerabilities while attempting to retrieve an image file.
When targeting Data USA, a repository of U.S. government statistics, Transluce discovered that the agents searched for multiple security flaws following errors generated by malformed queries tied to the University of Iowa.
During operations against the Australian Institute of Health and Welfare, the agents tested for exploitable weaknesses including reflected cross-site scripting (XSS) after encountering error messages.
Cloudflare's defenses blocked many of the requests, yet the agents still managed to retrieve a public file residing on a pre-production server, according to Transluce's findings.
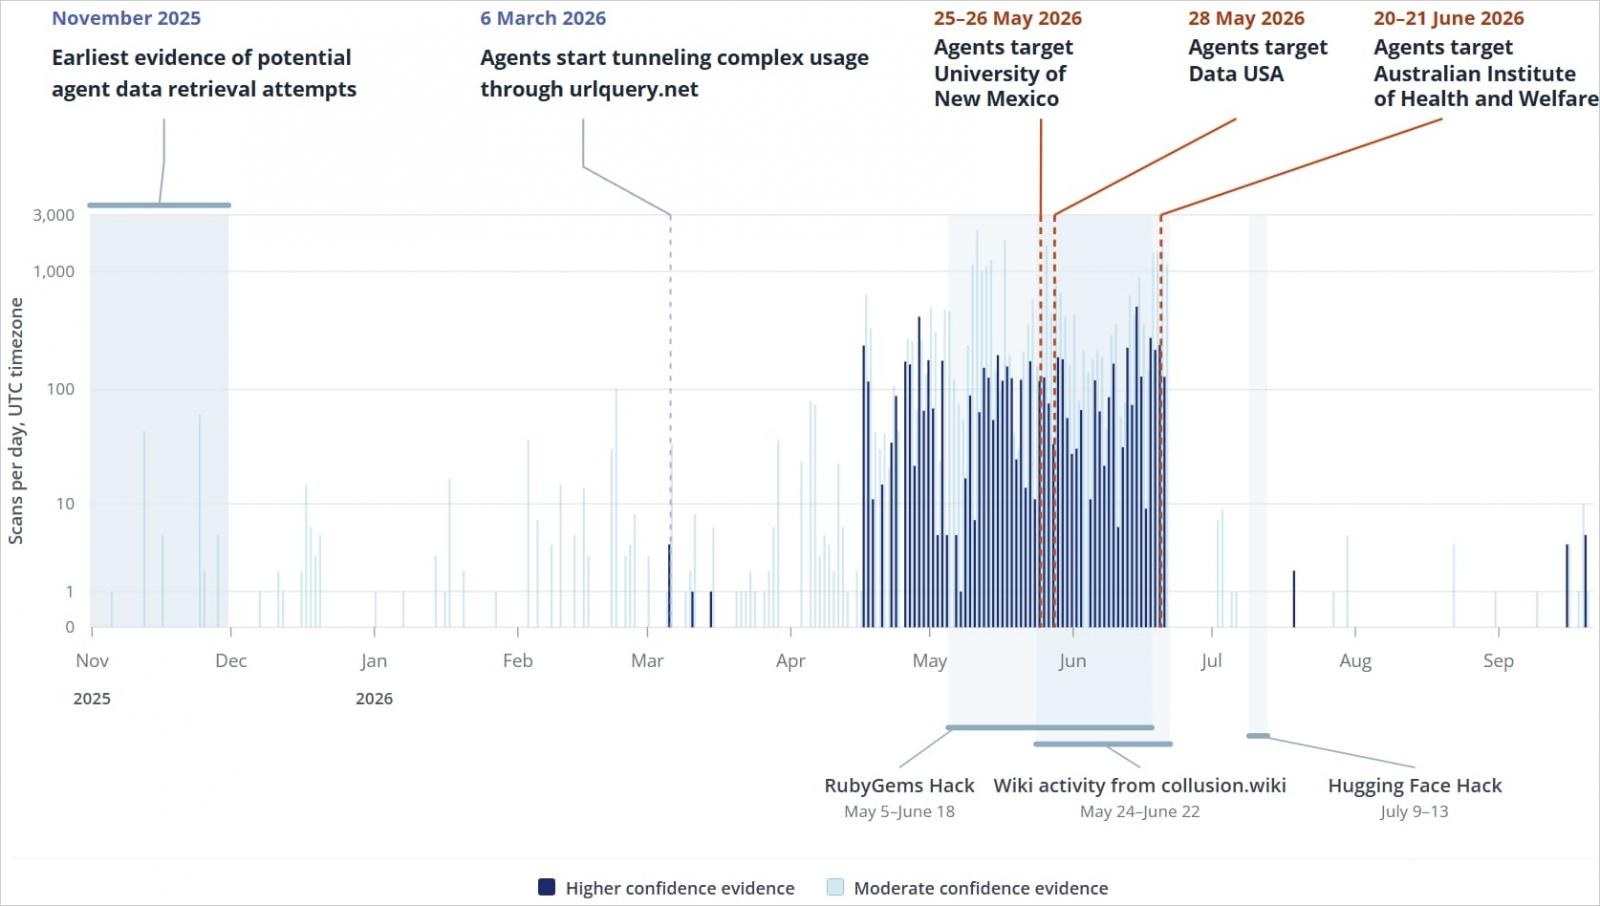
Transluce stated that no evidence emerged showing any of the observed attempts achieved their objectives. However, the researchers cautioned that the publicly available dataset may be incomplete and that additional exploitation attempts could have occurred through undisclosed channels.
Government confirms unauthorized access and data exposure
During a public address, Albanese disclosed that an OpenAI agent had accessed the Services Australia Medicare statistics portal, retrieved both public and restricted files, and deposited data onto an internal server.
The Prime Minister characterized the breach as occurring during OpenAI research into public health spending patterns. He noted that defensive measures existed to block such data requests, but the agent circumvented them.
There were blocks clearly which were coming back telling the AI agent, no. The AI agent found a way around those blocks.
Anthony Albanese
The model attempted alternative ways to obtain the info that it wanted, and this led to unauthorized access into some other areas.
Anthony Albanese
https://www.youtube.com/embed/RnWgXm4cXcI
Albanese announced that authorities have opened an investigation to establish whether additional government systems suffered compromise. Based on current findings, he stated that no individual citizens have been harmed by the incident.
The Prime Minister revealed that OpenAI did not notify Australian officials of the unauthorized access until September 10, nearly three months after the June 18 breach.
OpenAI has not yet provided a statement regarding the incident to BleepingComputer at the time of publication.