Unidentified threat actors seized control of Microsoft's verified X account on Thursday, leveraging the platform's 13 million-strong audience to distribute what security researchers characterize as a pump-and-dump cryptocurrency scheme. The compromise involved the account following and amplifying content from a suspended account impersonating Microsoft's Clippy mascot, according to reporting from The Verge.
The initial breach occurred when the legitimate Microsoft account (@Microsoft) engaged with a now-deactivated impersonation account (@clippymsftcto). A separate X account (@ClippyMSFT) continues to circulate the fraudulent scheme, promoting a $Clippy token and falsely claiming it maintains "a liquidity pool paired directly with $MSFT."
Microsoft moved quickly to contain the incident by purging the malicious posts and securing the account. The company released a statement confirming the unauthorized access and initiated an investigation into how the breach occurred.
We have confirmed unauthorized access to our account on X including posts that did not come from Microsoft. The account has been secured and the unauthorized posts have been removed, and we are continuing to investigate the circumstances.
Microsoft spokesperson, via The Verge
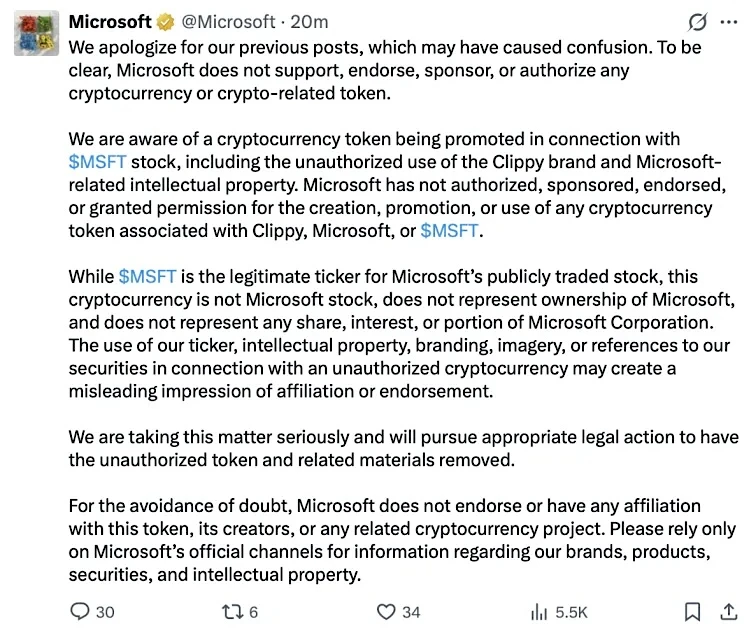
In a since-deleted message, Microsoft clarified its position on cryptocurrency initiatives and announced plans to pursue legal remedies. The company stated it has neither authorized nor endorsed any digital tokens bearing its name or intellectual property.
We are aware of a cryptocurrency token being promoted in connection with $MSFT stock, including the unauthorized use of the Clippy brand and Microsoft-related intellectual property. Microsoft has not authorized, sponsored, endorsed, or granted permission for the creation, promotion, or use of any cryptocurrency token associated with Clippy, Microsoft, or $MSFT. We are taking this matter seriously and will pursue appropriate legal action to have the unauthorized token and related materials removed. For the avoidance of doubt, Microsoft does not endorse or have any affiliation with this token, its creators, or any related cryptocurrency project.
Microsoft
Pattern of Compromised Accounts
This incident represents the second major compromise of a Microsoft X account in recent months. In June 2024, attackers breached the Microsoft India account (@MicrosoftIndia), which commanded an audience of over 211,000 followers, to impersonate Keith Gill, the trader known by the handle Roaring Kitty.
The India account breach deployed more sophisticated tactics than the current incident. Attackers leveraged the compromised account to direct users toward a fraudulent website (presaIe-roaringkitty[.]com) purporting to offer GameStop cryptocurrency in a presale arrangement. Users who connected their digital wallets to the site fell victim to wallet-draining malware that siphoned their cryptocurrency holdings.
Across the broader X ecosystem, verified accounts belonging to major institutions have become frequent targets for account takeover campaigns. Cryptocurrency fraud and wallet drainer schemes represent the primary motivation behind these attacks.
Threat intelligence firm ScamSniffer documented the scale of such operations in December 2023, revealing that cybercriminals operating the "MS Drainer" wallet drainer stole approximately $59 million in cryptocurrency from 63,000 victims through a single coordinated X advertising campaign spanning March through November.
The U.S. Securities and Exchange Commission's account (@SECGov) fell victim to a SIM-swapping attack in 2024, with the compromised account disseminating false information regarding Bitcoin exchange-traded fund approvals. The fabricated announcement triggered a temporary but measurable increase in Bitcoin's market price.
Eric Council Jr., identified as the perpetrator behind the SEC account compromise, entered a guilty plea in February 2025 and received a 14-month prison sentence for his participation in the scheme to manipulate Bitcoin's valuation through the hijacked account.