A.P. Moller–Maersk, the Danish shipping and logistics operator, has acknowledged that attackers compromised systems at a firm the company had previously taken over, resulting in data theft. WhiteArmor, a ransomware collective, announced the breach over the weekend and threatened to publish roughly 100GB of material allegedly taken from the company's logistics and supply-chain infrastructure.
Legacy system compromise
While investigations remain underway, Maersk's preliminary findings suggest that "no sensitive data has been disclosed." The company stated it foresees no operational disruptions and assured customers they may proceed with booking and administering shipments normally.

"The incident is isolated to a local system, and we have found no indication that there has been any impact on other Maersk systems or customer and partner systems that connect to Maersk through integrations such as APIs and EDI," Maersk states.
Maersk operates as one of the world's foremost container carriers, running ocean freighters, port facilities, warehouses, and air and ground transport operations across 130 nations. The firm maintains a fleet of 700 container vessels representing approximately 13.5% of worldwide fleet capacity, manages 60 terminals in 35 countries, and employs 100,000 workers. In the previous year, the company generated $54 billion in revenue with $2.9 billion in net profit.
The company disclosed that the intrusion was contained but withheld specifics regarding the compromised system, the nature of stolen information, or the timing of the attack. Maersk did not respond to follow-up inquiries at the time of publication.
Ransomware gang claims 100GB data theft
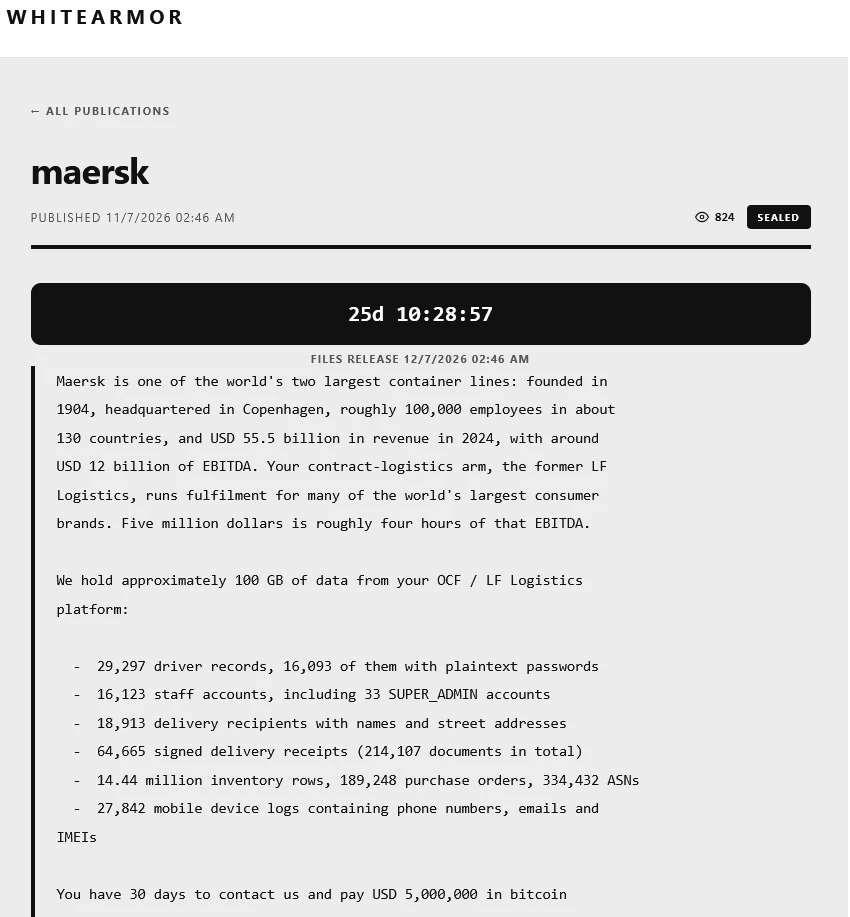
WhiteArmor posted Maersk on its public leak portal over the weekend, making a ransom demand of $5 million.
Your contract-logistics arm, the former LF Logistics, runs fulfilment for many of the world's largest consumer brands. Five million dollars is roughly four hours of that EBITDA. You have 30 days to contact us and pay USD 5,000,000 in bitcoin.
WhiteArmor
The gang asserts possession of approximately 100 GB of material purportedly extracted from Maersk's OCF/LF Logistics platform, which it is leveraging to back its extortion scheme. Maersk acquired LF Logistics, the original creator of the OCF/LF Logistics platform, from the Li & Fung Group in 2022.
According to the threat actor's claims, the stolen material encompasses nearly 30,000 driver records, passwords stored in plaintext, 33 SUPER_ADMIN accounts representing the highest system privileges, signed delivery receipts, and 14.44 inventory rows containing purchase orders and Advance Shipping Notice (ASNs). The attacker additionally claims to possess 27,842 mobile device logs containing phone numbers, email addresses, and IMEI (International Mobile Equipment Identity) numbers.
Maersk reiterated in its statement that "the incident is isolated to a local system" and pledged to update customers "as more relevant information becomes available, and if we identify any need to inform impacted parties of any further findings."
"As always, please treat any unexpected communications claiming to relate to this matter with caution and verify them through your usual Maersk contact," the company advises.
Maersk's latest incident echoes a 2017 attack involving NotPetya ransomware, which forced the company to reconstruct infrastructure comprising more than 4,000 servers and 45,000 workstations. That incident left the organization without IT capabilities for ten days and resulted in damages estimated at up to $300 million.