Jordanian authorities have detained a suspected member of the ShinyHunters hacking collective who operates under the alias Rey, according to Reuters reporting. The suspect, identified as Saif al-Din Khader, was taken into custody on Tuesday of this week. Multiple sources with knowledge of the arrest indicate that Khader is now assisting the FBI and other international law enforcement agencies in tracking down additional group members.
According to one source briefed on the matter, Khader is providing law enforcement access to his electronic devices and digital communications records to help identify and locate his alleged co-conspirators. A person familiar with the investigation told Reuters, "His cooperation is critical to ongoing efforts to arrest these hackers."
The detention follows an intensified FBI campaign against ShinyHunters in the wake of a cyberattack targeting the bureau itself. In September, the group claimed to have compromised FBI infrastructure by exploiting an alleged Oracle PeopleSoft zero-day vulnerability, then moving laterally into FBI-managed AWS GovCloud systems. ShinyHunters stated it obtained between 2TB and 3TB of data, encompassing records of current and former FBI staff, job applicants, and sensitive medical and psychiatric files from internal services. BleepingComputer has not independently confirmed the zero-day exploit, the lateral movement, or the data volume. The FBI acknowledged investigating unauthorized access claims but stopped short of confirming data theft.
Dutch law enforcement arrested a 24-year-old Amsterdam resident on September 15 as part of a ShinyHunters investigation. KrebsOnSecurity and DataBreaches identified the suspect as Pepijn van der Stap, who previously operated under the online handle Umbreon. Following that arrest, the FBI publicly urged remaining ShinyHunters members to surrender voluntarily.
Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who's left. The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out first while the choice is still yours.
FBI Cyber Division Assistant Director Brett Leatherman
On the same Tuesday when Khader's detention was reported, ShinyHunters operations began showing signs of disruption. An alleged ShinyHunters associate who had previously contacted BleepingComputer and other news organizations regarding the FBI attack and a recent Clop ransomware gang data breach suddenly deactivated their messaging account. The group's primary data leak site subsequently went offline, and the ShinyHunters representative ceased responding to media inquiries from BleepingComputer and Reuters. The connection between Khader's arrest and these operational disruptions remains unclear.
By Thursday, however, a new ShinyHunters data leak site had appeared online, suggesting that other members are continuing the extortion operation. BleepingComputer reached out to ShinyHunters regarding Rey's reported detention but received no reply.
Who is Rey?
The threat actor operating as Rey has been implicated in numerous data theft and extortion campaigns spanning the past two years. In January 2025, Rey was among four threat actors claiming responsibility for breaching Telefónica's internal Jira ticketing system, where approximately 2.3GB of documents, tickets, and related materials were allegedly exfiltrated. BleepingComputer reported that Rey and two other attackers involved in that incident were members of the then-emerging HellCat ransomware operation. The threat actor subsequently became linked to a broader campaign targeting Jira servers across multiple organizations worldwide.
In February 2025, Orange confirmed that its Romanian division experienced a cyberattack after Rey disclosed approximately 6.5GB of stolen data. Rey stated to BleepingComputer at that time that while he was a HellCat member, he had executed the Orange breach independently. Rey was later connected to the ShinyHunters extortion group and was observed holding administrative access within Telegram channels managed by Scattered Lapsus$ Hunters.
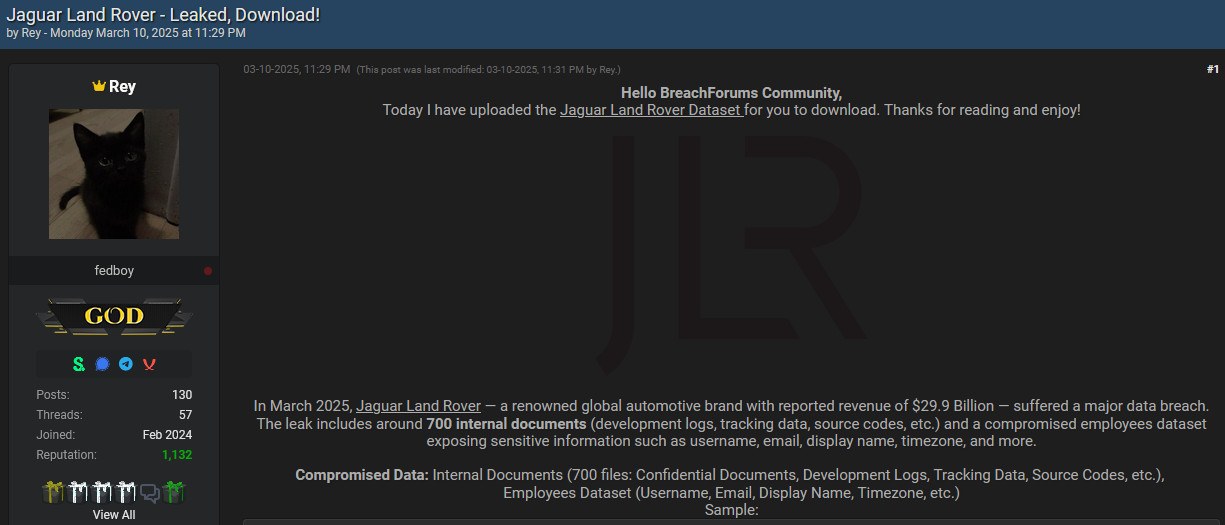
Scattered Lapsus$ Hunters emerged in 2025 and claimed to comprise former operatives from the Lapsus$, Scattered Spider, and ShinyHunters cybercriminal organizations. The collective claimed responsibility for the September 2025 cyberattack on Jaguar Land Rover that halted production for multiple weeks and ultimately inflicted damages exceeding $220 million on the automaker. Rey was also linked to an earlier March 2025 breach of Jaguar Land Rover, during which the threat actor leaked gigabytes of material including Jira issues, source code, employee records, and development logs.
In November 2025, security journalist Brian Krebs identified Rey as Saif Al-Din Khader after examining infostealer logs and conducting direct communication with Khader via Signal. According to Krebs's reporting, Khader stated he was attempting to separate himself from Scattered Lapsus$ Hunters and asserted that he had been working with law enforcement since at least June.
I'm already cooperating with law enforcement. In fact, I have been talking to them since at least June. I have told them nearly everything. I haven't really done anything like breaching into a corp or extortion related since September.
Saif Al-Din Khader, as reported by Brian Krebs
Krebs noted that he was unable to independently verify these claims made by Khader.