On Tuesday, Ivanti notified customers to deploy urgent patches addressing an actively exploited zero-day flaw in the Connect Secure (ICS) remote access gateway. The ICS SSL VPN—previously marketed as Pulse Connect Secure and originally developed as Juniper Pulse—serves as an enterprise-grade platform enabling remote workers, third-party contractors, and distributed teams to securely reach internal systems and cloud infrastructure.
The vulnerability, designated CVE-2026-104935, represents a high-severity authentication bypass affecting ICS versions 22.8R2.4 and earlier, 25.1.2.2 and earlier, and 25.1.1.1 and earlier. Cybersecurity researchers at Volexity discovered and reported the flaw. Unauthenticated remote attackers can leverage this vulnerability through straightforward exploitation methods requiring no user participation to run arbitrary code on vulnerable ICS appliances.
At the time of disclosure, Ivanti is aware of limited exploitation in the wild. We are working directly with those organizations while making information, updates and remediation available to the broader customer community. If you are running one of the impacted versions, Ivanti recommends you act immediately.
Ivanti
Ivanti further advised that "Customers should review the security advisory, upgrade to the fixed version as soon as possible, and run the Integrity Checker Tool regularly."
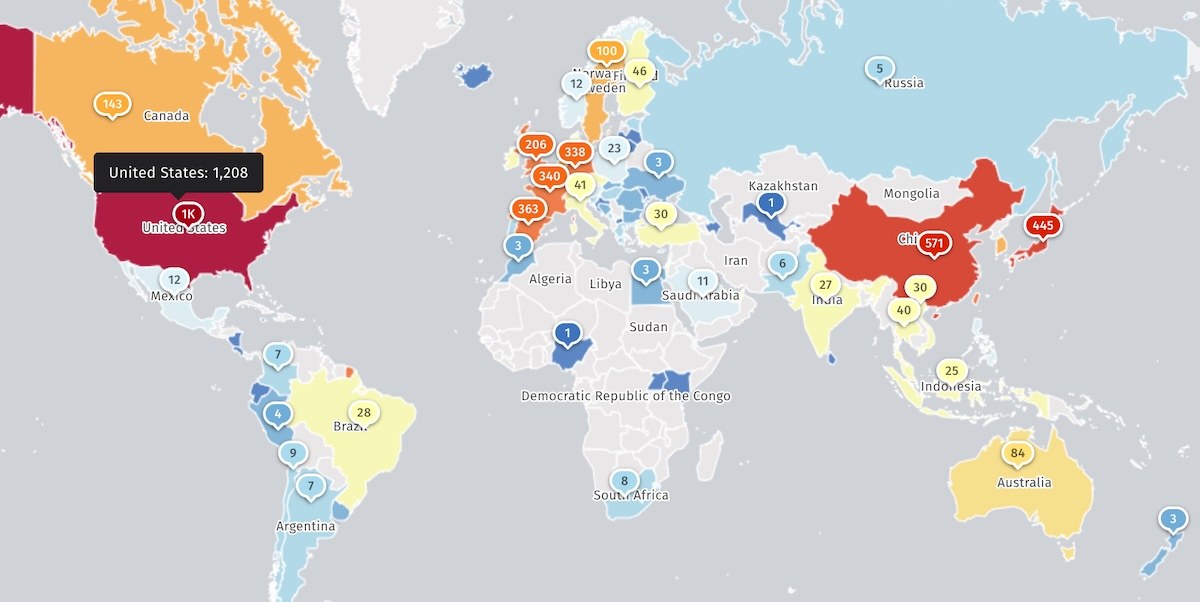
According to Shadowserver, a prominent internet threat monitoring service, over 5,500 ICS instances remain publicly accessible online. The organization has not disclosed whether this count includes honeypots or systems that have already been hardened against current attack campaigns.
Attackers have consistently targeted Ivanti vulnerabilities—particularly zero-days—as a means to rapidly penetrate corporate networks and exfiltrate sensitive business and customer information. The company has released patches for multiple Connect Secure zero-days that saw real-world exploitation over recent years, with some vulnerabilities chained together in coordinated campaigns to distribute malicious software.
In early January 2024, Ivanti resolved an authentication bypass (CVE-2023-46805) and a command injection flaw (CVE-2024-21887). Two weeks later, the company patched a server-side request forgery vulnerability (CVE-2024-21893). During January 2025, Ivanti addressed a remote code execution flaw (CVE-2025-0282), followed by a second RCE vulnerability (CVE-2025-22457) that Chinese state-sponsored threat actors have weaponized since at least mid-March 2025.
The Cybersecurity and Infrastructure Security Agency (CISA) has documented 36 Ivanti product vulnerabilities experiencing active exploitation since November 2021, with ransomware operators abusing 12 of these flaws.
Ivanti operates with approximately 3,000 employees and maintains relationships with more than 7,000 partners globally. The company serves over 40,000 customers worldwide who depend on its IT asset management offerings.