Security researchers at Bitdefender have identified a malware operation dubbed Midnight Mimosa that arrives pre-installed on budget Android smartphones, bypassing user consent entirely. The malicious code sits in the device firmware itself, providing attackers with system-level privileges to deploy applications silently, execute remote code, modify permissions, and repurpose phones as residential proxies for routing internet traffic.
The campaign has compromised thousands of devices across more than 150 countries over roughly two years, with the heaviest concentration of infections in Mexico, France, Italy, the United States, Germany, Brazil, and Spain. Researchers discovered the malware on phones bearing model names tied to legitimate brands such as Doogee S200 X and Cubot KINGKONG X, alongside devices masquerading as Samsung and Apple products.
The exact point at which the firmware was compromised remains unknown. Bitdefender has determined that the malware was introduced somewhere within the device supply chain, but the responsible party and the stage at which tampering occurred have not been identified. Some users reported that official firmware updates from manufacturers later resolved the infections, though the companies have not disclosed how the malicious code entered their builds in the first place.
System-level persistence and evasion
Unlike conventional Android malware requiring user installation, Midnight Mimosa ships as part of the system partition on affected devices. The malicious components masquerade as legitimate Android system services using names such as com.android.system.lite, com.android.sys.prot, and com.android.sys.gmsprot. Because these applications run with elevated system privileges and are cryptographically signed, standard Android uninstall procedures cannot remove them.
Bitdefender's App Anomaly Detection system first flagged the campaign after observing com.android.system.lite silently deploying and removing other applications. Investigation revealed a larger malware framework that downloads additional modules from command-and-control servers to execute various malicious functions. The researchers catalogued approximately 32 applications distributed through this framework, disguised as weather utilities, file managers, app lockers, OCR tools, and audio editors.
The malware employs several techniques to evade Android's built-in security. Before deploying malicious applications, it temporarily disables the Google Play Store app (com.android.vending) to prevent Google Play Protect from detecting the installation. Once deployment completes, the malware re-enables the Play Store to avoid triggering alerts. Some variants also falsify Android's installer records to make malicious applications appear as if they came from Google Play, despite being directly deployed by the malware framework.
Ad fraud and residential proxy abuse
The primary revenue mechanism relies on generating fraudulent advertising impressions and clicks. According to Bitdefender, "The system app itself doesn't register the fraudulent impressions and clicks. The revenue engine is driven by the dropped cover apps, including real-looking weather, app-lock, note, and OCR apps, which load genuine ads through a legitimate ad SDK. The goal is simple: to load an invisible window on top of apps that registers ads being shown."
The malware displays advertisements in hidden windows or automatically interacts with ads without device owner awareness. Additionally, the framework includes functionality to convert infected phones into residential proxies. Researchers identified a malicious application disguised as an app locker, com.mobile.applock.en, containing a TCP proxy component that registers infected devices with remote command servers. Once registered, the malware can receive instructions to connect to specified hosts and relay traffic through the infected device, potentially allowing attackers to mask the origin of malicious traffic or access systems reachable from the compromised phone.
Bitdefender confirmed that the proxy command-and-control infrastructure remained operational and accepting device registrations. However, during testing, newly registered test devices did not receive relay targets, preventing confirmation of whether attackers were actively forwarding traffic at the time of investigation.
Google Play Store distribution and removal challenges
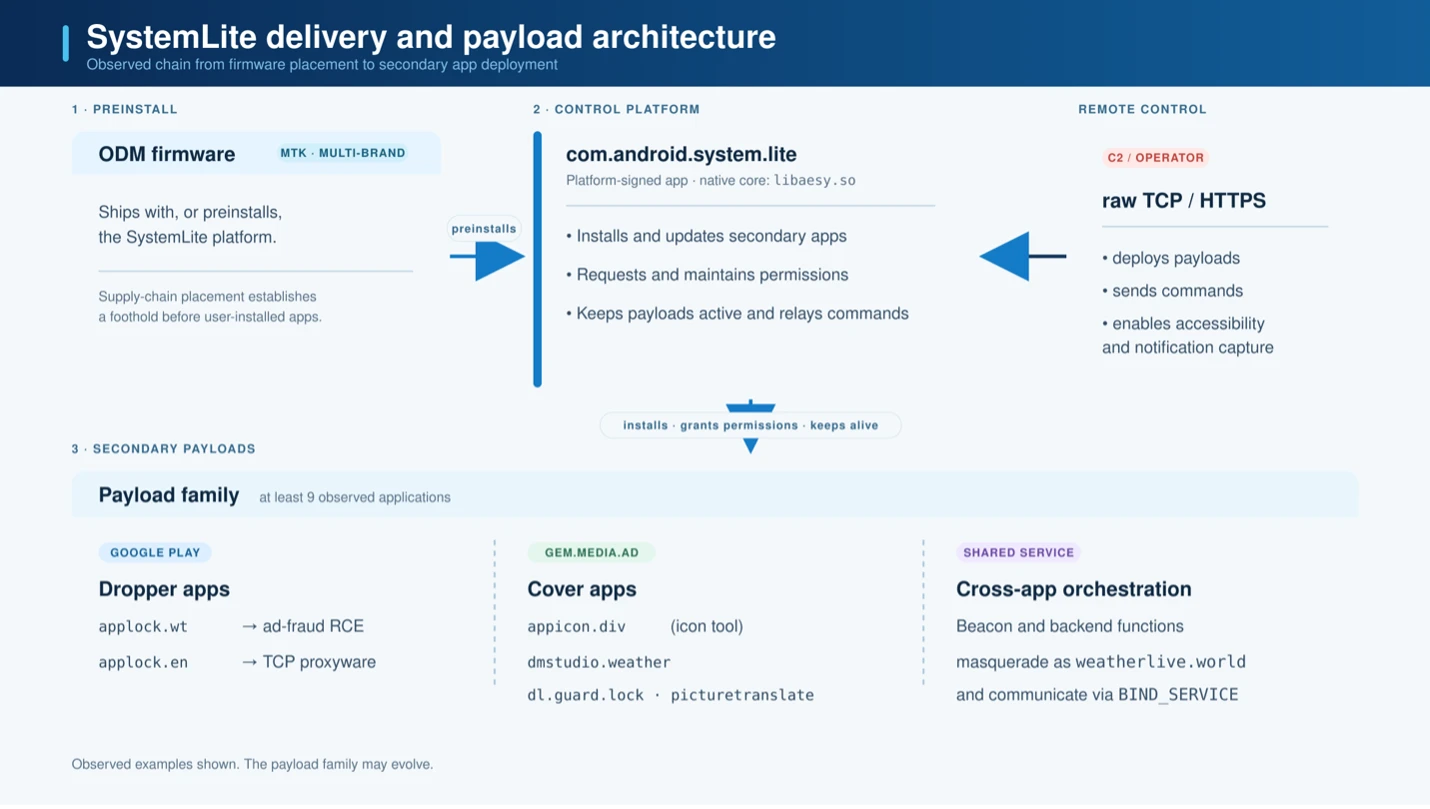
Beyond pre-installed firmware malware, researchers discovered 13 Android applications on the Google Play Store containing identical advertising fraud code and communicating with known Midnight Mimosa infrastructure. These applications were distributed using 13 different signing certificates and at least two developer accounts identified as fivedev and CPS Developer. Unlike the system-level components, these applications lack the elevated privileges needed to silently deploy other software, but they can still display advertisements outside their user interface, including when the phone is idle.
Researchers also identified firmware signed with certificates associated with Chinese device manufacturer Shenzhen Zediel, though it remains unclear whether the company participated in the campaign.
Removing Midnight Mimosa presents significant challenges for affected users. Because the malware operates as a high-privileged system application, complete removal requires firmware-level remediation or disabling malicious components via Android Debug Bridge (ADB)—a process too complex for most consumers. Users on XDA forums reported that suspicious applications repeatedly reinstalled themselves after removal, and one Doogee Fire 3 Max owner documented that an official firmware update reintroduced the malware after it had been cleaned by reverting to an older firmware version.