U.S. law enforcement has dismantled the online infrastructure behind two hacking platforms employed by Chinese state-sponsored actors known as Flax Typhoon. The FBI seized seven domains that supported MicroScan and FishHub, tools allegedly run by Integrity Technology Group, a Beijing-based firm with government contracts, to conduct widespread attacks against critical infrastructure and other targets across multiple countries.
The domain seizures targeted the operational backbone of platforms used to identify vulnerabilities and penetrate networks belonging to U.S. and international organizations. According to the Department of Justice, Integrity Tech supplied China-linked threat actors with the technical means to scan for security weaknesses and breach critical systems.
Integrity Technology Group provided China-linked threat actors with capabilities used to conduct widespread vulnerability scanning and, in some cases, intrusions targeting U.S. and foreign critical infrastructure
Brett Leatherman, assistant director of the FBI's Cyber Division
Leatherman noted that the Chinese government relies on outside contractors to expand its cyber reach, and that dismantling these support networks constrains the ability of state-linked hackers to strike American infrastructure.
MicroScan: Scanning for Weaknesses
Integrity Tech developed MicroScan as a vulnerability-scanning platform designed to locate security flaws in target networks. According to FBI court filings, the tool operated alongside a botnet of Mirai-infected internet-connected devices to probe potential victims.
Targets identified in the affidavit included a power utility in South Carolina, airports serving Japan and Poland, Taiwanese natural gas and power operators, and educational institutions. The scanning activity in some cases preceded successful network breaches; two Taiwanese universities whose networks were scanned via MicroScan in August 2022 and March 2023 were subsequently compromised.
The FBI confirmed that the hacking tools enabled intrusions into critical infrastructure but did not specify whether the particular power companies, airports, and energy providers mentioned were successfully penetrated. Law enforcement seized the domain c0cc.cc, which Integrity Tech used to access MicroScan and which was confirmed active in September 2026.
FishHub: Phishing and Data Theft
The second platform, FishHub, served a different purpose: conducting spear-phishing campaigns and deploying additional malware into already-compromised networks. Once installed, the malware granted attackers unauthorized remote access, enabled them to locate and extract sensitive files, and transmitted stolen data to servers controlled by Integrity Tech.
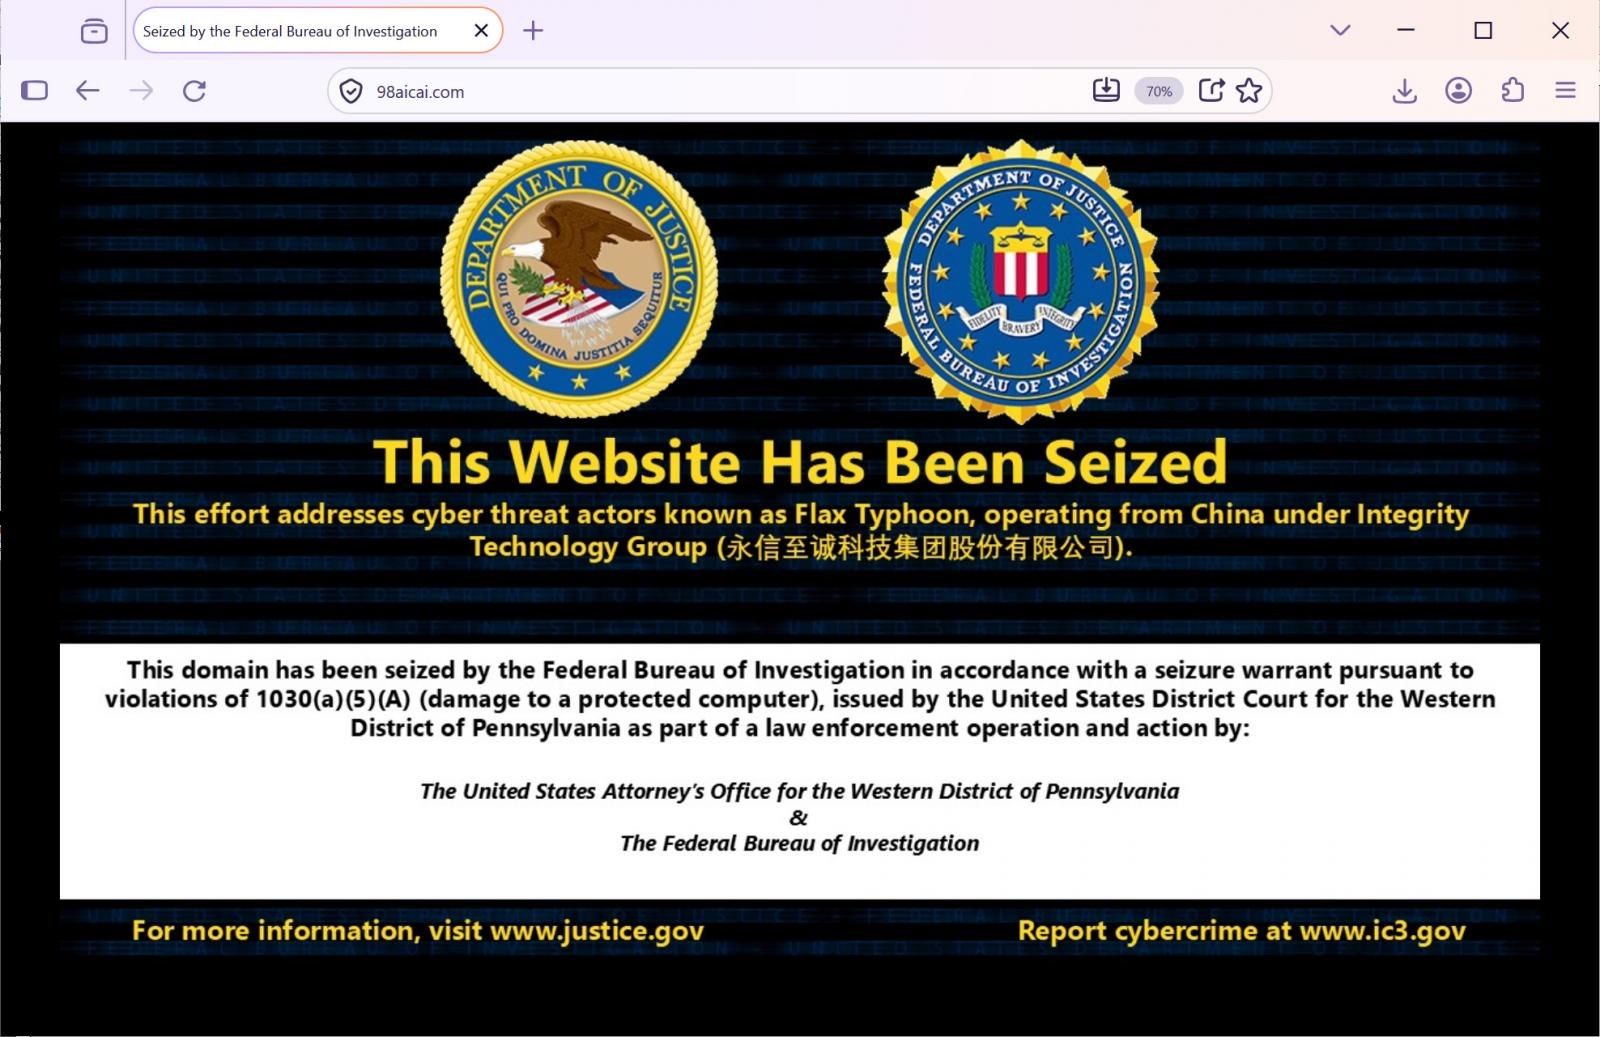
Court documents reveal that investigators discovered data and files from more than 20 organizations stored on a server connected to the FishHub tool, including six Taiwanese universities. Law enforcement seized five domains used to distribute the malware: 98aicai.com, 98aicode.com, outlook3650.com, youtubecard.com, and linkedinns.net.
A seventh domain, 98aiblog.com, was linked to SoftEther VPN software deployed on compromised systems to maintain persistent remote access. All seized domains now display FBI seizure notices identifying the Flax Typhoon group and Integrity Technology Group.
Joint Advisory and Vulnerability Details
In parallel with the domain seizures, the FBI, CISA, NSA, and international law enforcement partners released a coordinated cybersecurity advisory documenting how Chinese government-linked hackers leveraged Integrity Tech's infrastructure to compromise organizations and exfiltrate sensitive data. The advisory identifies targets across U.S. government agencies, critical manufacturing, healthcare, information technology, law enforcement, educational institutions, and religious organizations, as well as entities in Southeast Asia, Africa, and North America.
The activity overlaps with operations tracked under the names Flax Typhoon, Ethereal Panda, and Red Juliett, though authorities note that not all activity may necessarily connect to Integrity Tech.
According to the advisory, MicroScan is a Python-based scanner containing more than 1,300 penetration-testing scripts designed to uncover security flaws in websites and services. The scripts targeted widely deployed software including Oracle WebLogic, Apache Struts, WordPress, Jenkins, and similar applications.
Investigators identified eight specific vulnerabilities that the attackers regularly exploited:
- CVE-2015-3306: ProFTPD unauthorized file read vulnerability
- CVE-2015-5477: ISC BIND denial-of-service vulnerability
- CVE-2016-3081: Apache Struts remote code execution vulnerability
- CVE-2021-3199: ONLYOFFICE DocumentServer unauthorized file write vulnerability
- CVE-2023-22894: Strapi information disclosure vulnerability
- CVE-2014-6278: GNU Bash (Shellshock) remote code execution vulnerability
- CVE-2019-11510: Pulse Secure VPN arbitrary file read vulnerability
- CVE-2021-22205: GitLab remote code execution vulnerability
Beyond MicroScan and FishHub, the attackers deployed the open-source EBurst tool to conduct password-spraying attacks against Microsoft Exchange servers. They also used additional tools to steal emails, harvest Active Directory credentials, and move stolen data off victim networks.
Investigators uncovered a custom web application that permitted third parties to browse stolen emails without requiring direct access to the compromised accounts themselves.
Recommendations and Prior Actions
The joint advisory includes indicators of compromise—IP addresses, domains, malware hashes, and tool specifications—to assist organizations in detecting potential intrusions. Authorities recommend that organizations review these indicators, apply patches to vulnerable systems, disable unnecessary exposed services, and implement multifactor authentication to defend against such attacks.
This disruption represents the second major law enforcement action against Integrity Tech's infrastructure. In September 2024, the Justice Department dismantled a Mirai botnet operated by Integrity Tech that consisted of more than 200,000 compromised consumer devices worldwide.
International authorities have also targeted the company. The UK government imposed sanctions on Integrity Tech in 2025, and the European Union followed with sanctions in 2026, citing the firm's involvement in cyberattacks against Europe and allied nations.