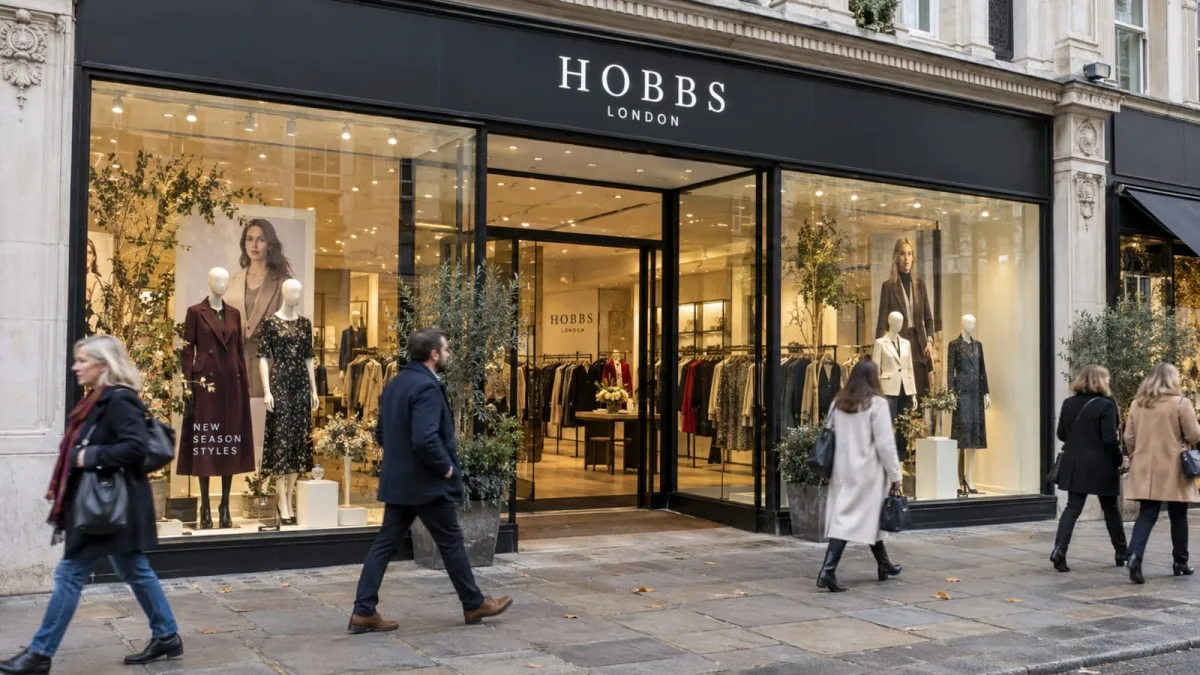
TFG London, the British arm of South Africa's The Foschini Group, disclosed a cybersecurity incident affecting its premium fashion operations. The attack disrupted IT infrastructure serving Phase Eight, Hobbs, and Whistles, though physical retail locations continued operating normally.
The company identified the intrusion on October 11 and mobilized incident response protocols alongside external cybersecurity specialists. Other brands within the group—Inside Story and White Stuff—escaped impact, as did operations across Australia and Africa.
TFG London operates 649 retail outlets worldwide and recorded £488 million ($646M) in annual revenue as of mid-2026. The organization is currently examining whether attackers accessed customer data and pledged to inform impacted parties if information was compromised.
No threat actor has publicly claimed responsibility for the TFG London incident. Customers of the three affected brands face heightened risk from phishing and social engineering campaigns while investigations continue.
The TFG London attack arrives amid a broader security crisis in the fashion retail sector. ASOS, another major UK retailer, recently suffered a breach when attackers deployed malicious push notifications through its mobile application, exploiting stolen employee credentials obtained via social engineering to access customer records including names, contact information and account details.
Swedish clothing giant H&M is also facing scrutiny following claims this week of a cyberattack attributed to the ShinyHunters group, with threats to release stolen data. An H&M representative told BleepingComputer: "We are aware of information circulating online regarding a potential cyber security incident and are currently investigating the claims. At this time, we have not found any indications that our data environment has been compromised."