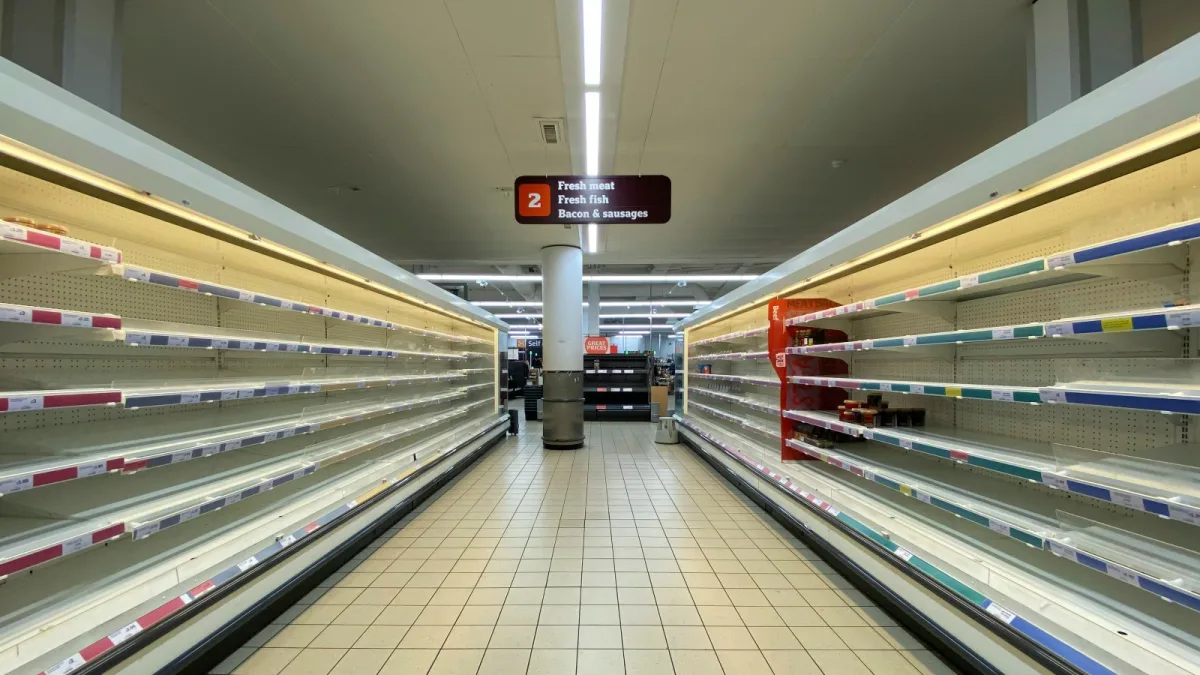
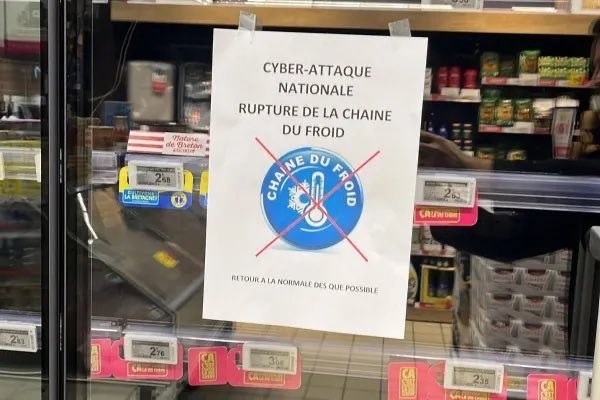
A coordinated cyberattack targeting refrigeration infrastructure struck French supermarket operators over the weekend, with attackers gaining control of Danfoss refrigeration controllers and deliberately warming storage units. The incident impacted Intermarché, Coopérative U, Carrefour Market, Monoprix, Leclerc, and Super U, according to French media reports indicating that somewhere between 250 and 350 retail locations experienced disruptions, resulting in substantial inventory losses and financial harm.
The attackers exploited older iterations of Danfoss control software to access refrigeration controllers and activated the built-in automatic defrosting mechanism, causing temperatures inside supermarket refrigerators to rise uncontrollably on Sunday evening.
Dominique Schelcher, president of Coopérative U, acknowledged the breach in a statement released today, confirming that the attack had compromised refrigeration systems across multiple locations within the chain's network. He stated:
I can confirm that, since last night, a cyberattack has been affecting the refrigeration systems in several stores within our @CooperativeU network. Our teams are fully mobilized, working alongside refrigeration specialists, to resolve the situation as quickly as possible. An investigation will be conducted to shed full light on this attack.
Dominique Schelcher, Coopérative U president
Schelcher further characterized the attack as unprecedented and unacceptable, stating: "Targeting equipment essential for preserving fresh produce and supplying food to the French people is an extremely serious matter and is unprecedented. It is unacceptable."
The incident has drawn attention from European leadership. Christophe Hansen, the EU's agriculture and food commissioner, publicly denounced the attack and identified Leclerc, France's largest supermarket operator, as among the affected victims.
Prosecutors in Paris have initiated a formal investigation into what they describe as "the large-scale cyberattack affecting the refrigerators of several major food retail chains across France." The inquiry aims to identify all affected parties and establish connections between the attack and reported losses of foodstuffs and fire incidents.
The specific method by which attackers compromised the Danfoss refrigeration controllers remains unclear. However, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued a warning in May 2025 regarding a high-severity authentication bypass flaw (CVE-2025-41450) affecting the Danfoss AK-SM 8xxA Series hardware platform, which manages refrigeration and HVAC systems commonly deployed in food retail environments. While no confirmed connection has been established between this vulnerability and the current attack, the timing and targeting raise questions about potential exploitation.
Separately, retail conglomerate Ahold Delhaize, one of the world's largest food retail operators, disclosed on Monday that it had taken certain systems offline following a "cybersecurity incident," though details regarding any connection to the French supermarket attack remain unavailable.