Security alerts do not typically surface in isolation. A single detection can trigger a cascade of related signals across an environment, forcing human analysts to determine which ones connect and what they collectively indicate. When dozens arrive together, the workload can paralyze even experienced security teams. Cloudflare has addressed this challenge with a built-in, multi-AI-agent security operations harness designed to operate at its scale.
The Cloudflare Managed Defense AI agent harness accelerates the work of pulling data, correlating detections, and identifying blind spots as fresh alerts continue flowing in. The system leverages the OpenAI Daybreak Defense Network and a partnership with Anthropic, using approved models including GPT-5.6 Cyber and Mythos for in-depth analysis. Cloudflare's open-source decision model, Clef, handles initial assessment and scoring.
Extracting meaning from each alert demands substantial analyst time. Even sophisticated Security Information and Event Management (SIEM) systems leave too much work for human review. Analysts must pull data, correlate detections, and account for missing sources while new alerts keep arriving. The harness addresses the core questions analysts face: Which alerts warrant silencing? What action fits? Which should be ignored? Which are false positives versus true positives? Which should escalate to incident response? By consolidating these decisions, the system gives Managed Defense Analysts a unified view showing related alerts, collected evidence, visible gaps, and suggested next steps. The outcome is faster analysis and faster resolution and mitigation deployment.
Why a single agent fails
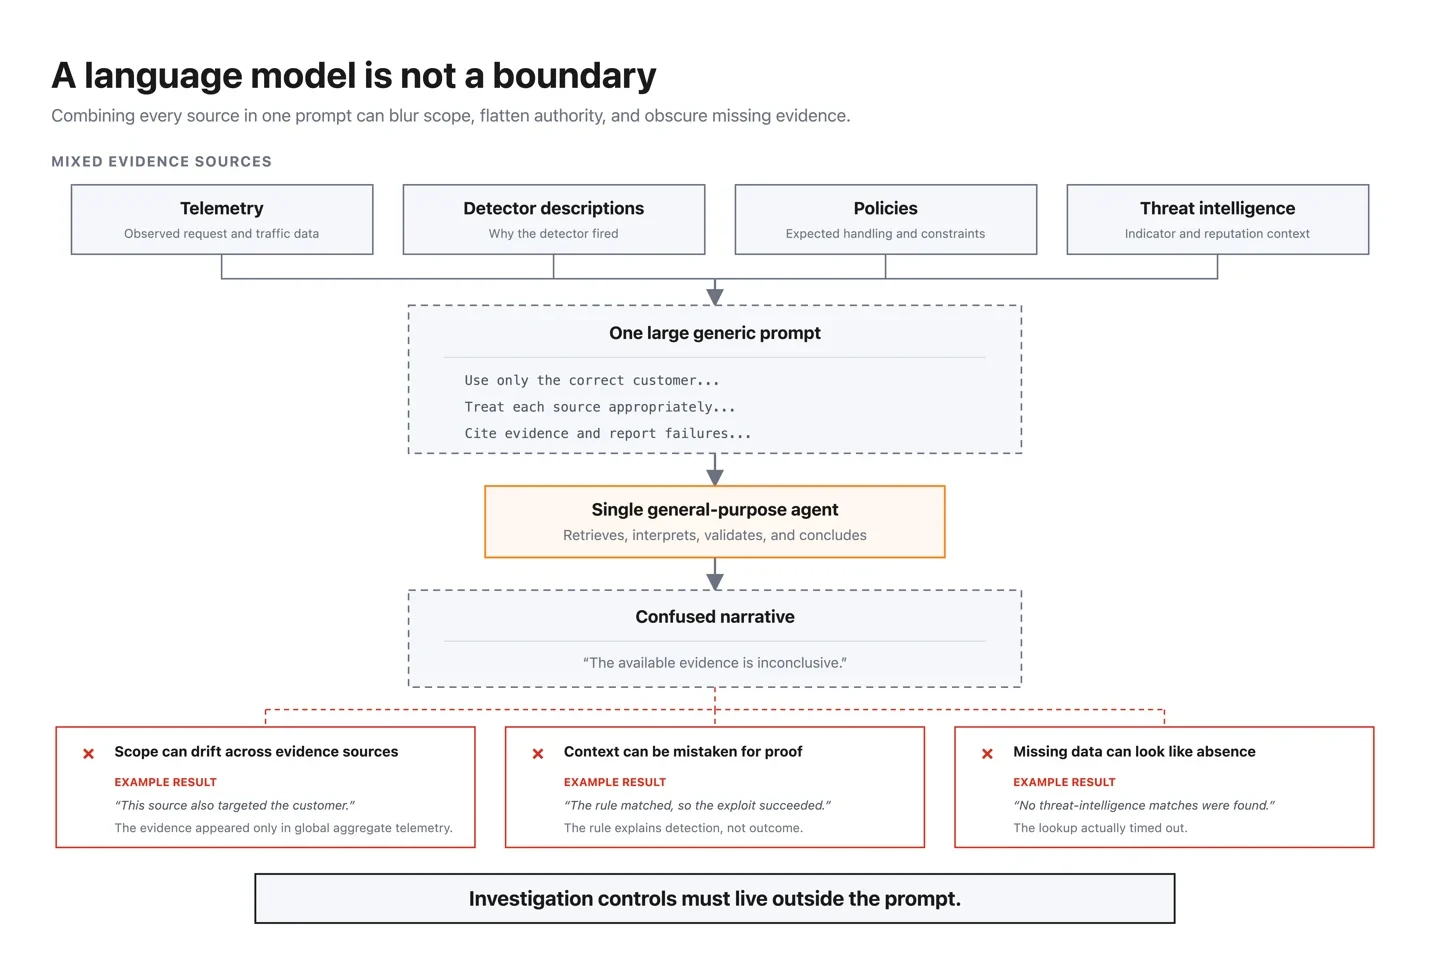
Cloudflare's initial prototype revealed the shortcomings of a general-purpose single agent. When given the entire investigation, the agent produced useful findings but also generated unsupported claims. Flattening telemetry, detector descriptions, policies, and threat intelligence into one prompt caused their distinct functions to blur together.
Three recurring issues emerged from the single-shot AI agent design:
- Context became authority. A detection is a hypothesis, not proof that an exploit succeeded or an attack occurred. A broad AI agent can blur that distinction.
- Scope drifted. An AI agent can query the wrong account, time range, or source. You can't rely on a language model prompt to be a boundary.
- Failure disappeared. If a lookup times out, the result may not distinguish "not checked" from "checked and not found."
To solve these problems, Cloudflare moved evidence collection and scope enforcement into application code, running before any model analysis begins.
Recon first, inference second
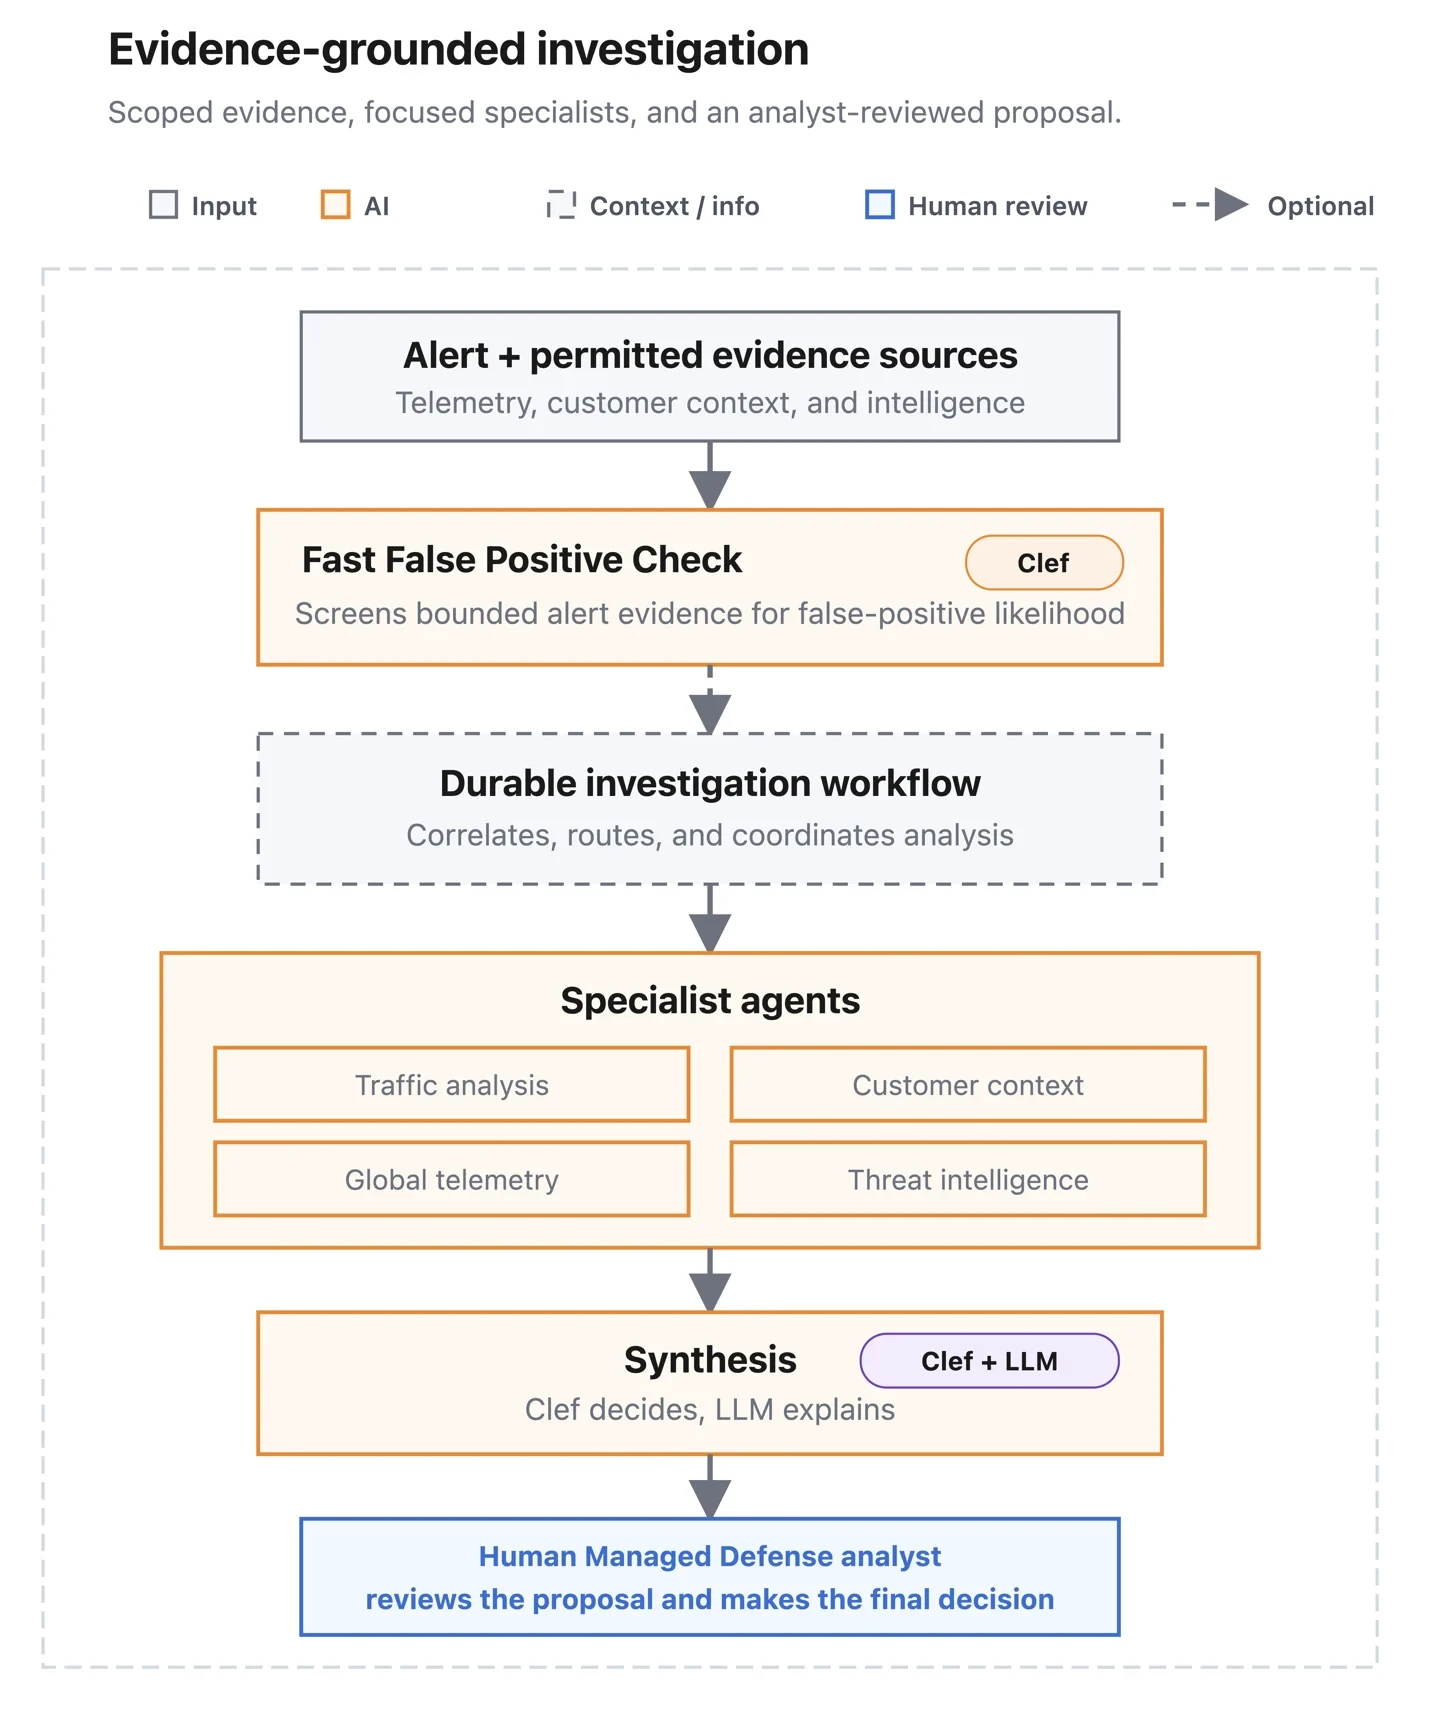
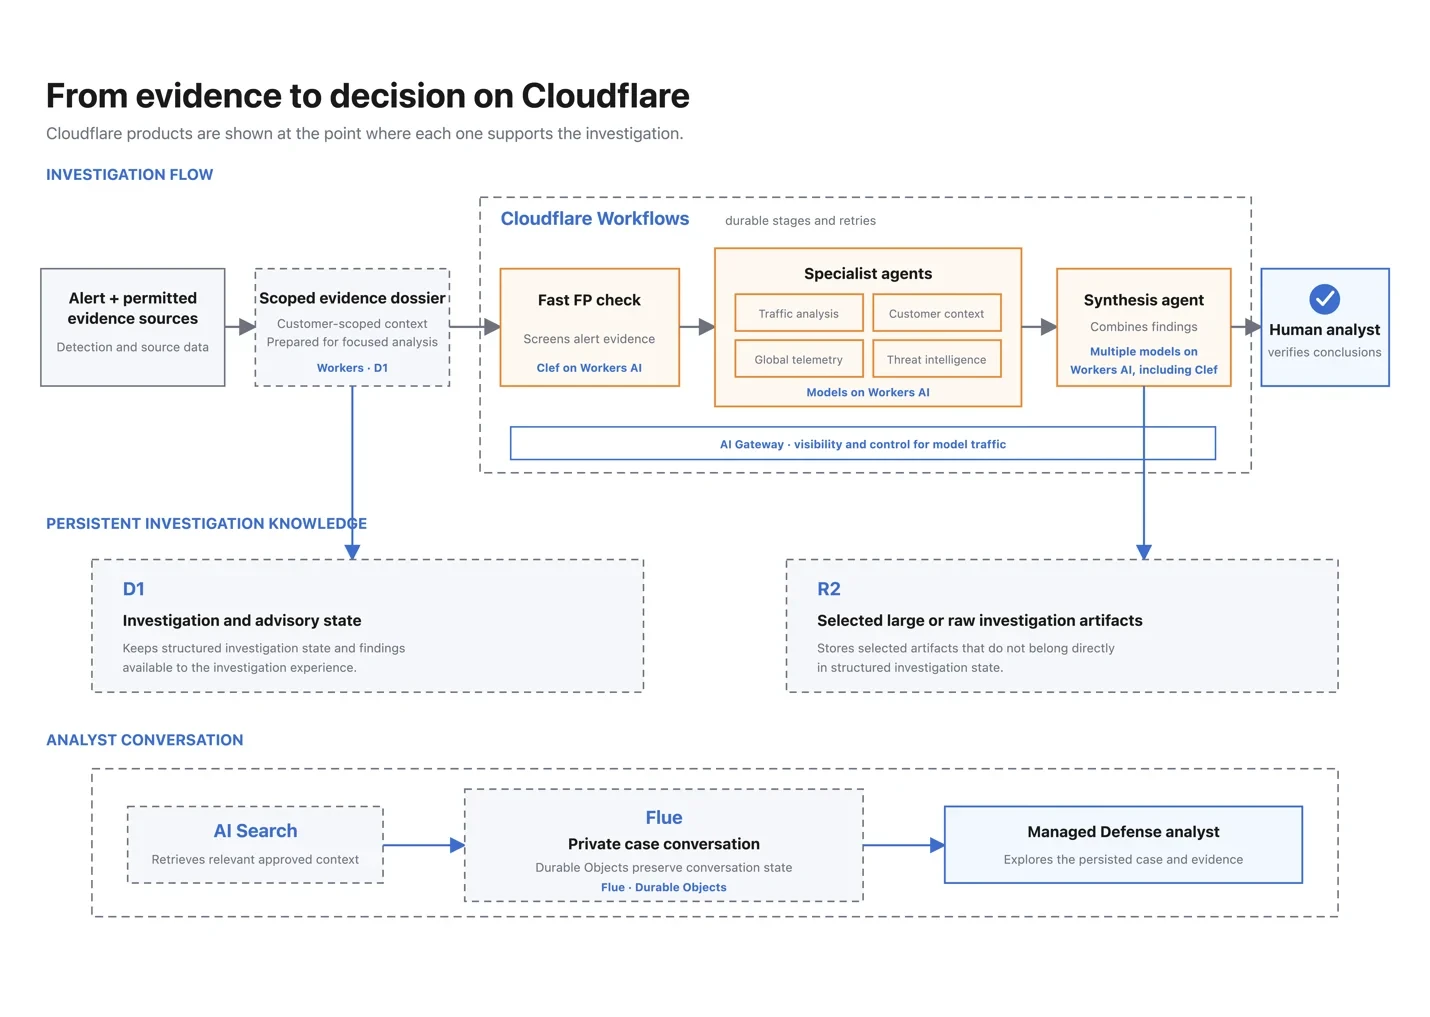
While it is tempting to insert an AI agent at every step, the front half of the harness contains none. Before inference runs, deterministic code executes a fixed set of reconnaissance workflows using versioned API calls. It gathers the customer's identity, detection history, traffic baseline, enforcement outcome, and network observations. Each data point is tagged with its source, version, and timestamp.
Cloudflare observes both the incoming request and the control action applied to it. This allows the investigation to connect the behavior that triggered an alert with both the control that fired and its result. The fixed recon snapshot also enables reproducibility. If AI agents retrieved their own data, successive runs could diverge due to changing inputs. With a static snapshot, the same data can be replayed, so differences between specialist agents' conclusions stem from interpretation rather than data retrieval.
Filter noise early
Most alerts do not represent incidents. The same rule often fires repeatedly on known traffic patterns, and alerting Managed Defense Analysts each time makes it easier to overlook genuine security threats. A lightweight triage model was needed to compare each alert against its reconnaissance data: Has this event been detected for this customer before? What did Managed Defense Analysts decide previously? Does the traffic align with normal human behavior? Alerts scoring high as likely false positives bypass analysis by specialist AI agents.
Clef, running on Workers AI, proved ideal for this fast agentic reasoning. Known high-volume noise is deterministically marked as passive upon arrival. It remains available as context but does not enter the active queue.
Specialist AI agents handle the investigation
For alerts requiring deeper examination, a coordinator AI agent deploys four specialist AI agents in parallel:
- Traffic analysis reviews request behavior, historical changes, and enforcement.
- Customer context reviews earlier alerts, dispositions, and Managed Defense Analysts' decisions.
- Global telemetry compares the activity with privacy-preserving Internet-wide signals.
- Threat intelligence checks indicators already admitted to the alert or case.
A synthesis AI agent merges their typed findings into one advisory; it cannot fetch new evidence or select a classification outside the approved vocabulary. Keeping each task narrow makes unsupported claims easier to identify, and recommendations easier to review.
Global context without customer data
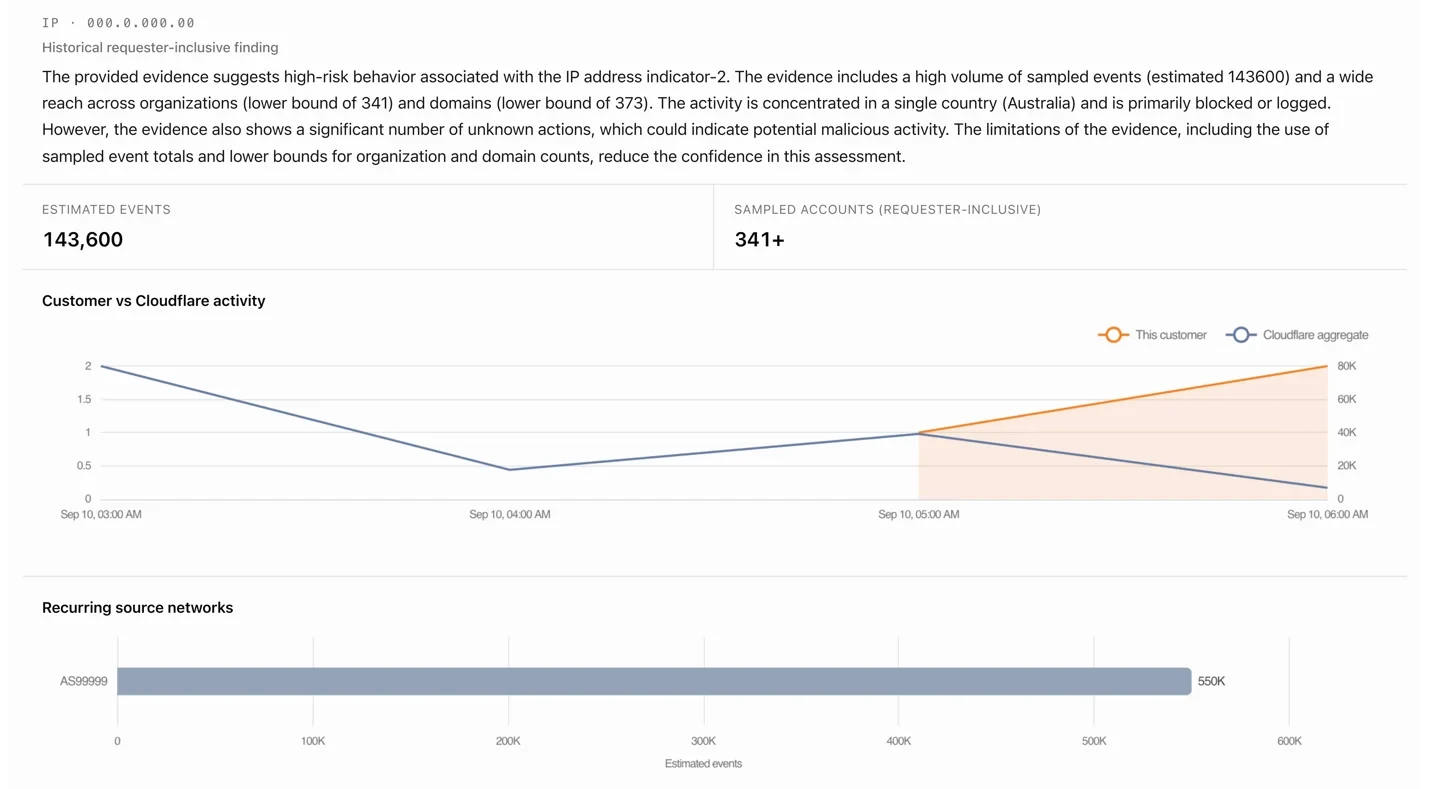
A security tool understands what occurs inside its deployed environment but knows little about the broader world. Cloudflare compares an alert against patterns observed across its global network. An IP may be targeting one site, scanning thousands of sites, or appearing for the first time. These patterns carry different significance. To maintain customer privacy, the global telemetry specialist works only with aggregates; it never receives another customer's individual records or identity.
This perspective combines signals from Cloudflare's CDN, WAF, DDoS, Turnstile, Rate Limiting, and Cloudforce One threat intelligence. The synthesis AI agent weighs both global reputation and customer history. This approach allows a globally common pattern to inform per-customer decisions without automatically implying a widespread campaign for all customers.
History is evidence
Every evaluation takes into account what came before: the alert, the pattern, and which customer. The recon dossier tracks the alert's own history including how many times this service alert has fired, how many dispositions were false positives, and what the Managed Defense Analyst concluded. An attack pattern that has been benign every time Managed Defense Analysts have seen it is fundamentally different from a first sighting, and specialist AI agents are informed which one they are examining. Approved background context is retrieved from previous alerts and cases, so prior conclusions inform today's decision instead of being rebuilt from scratch.
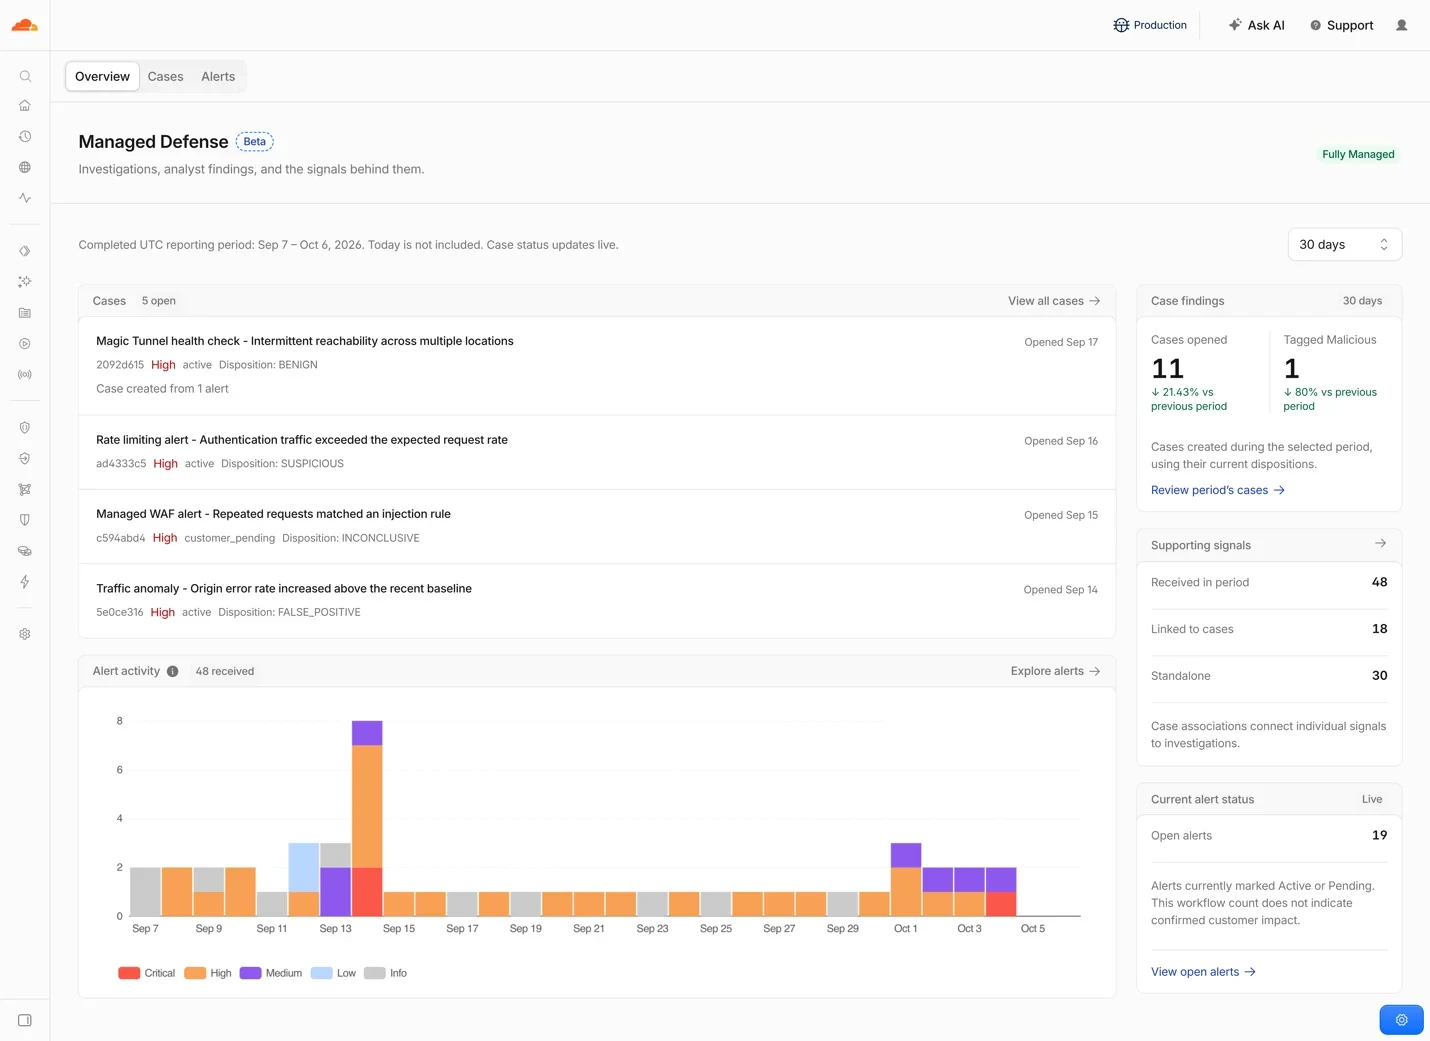
The system consolidates related alerts into a unified case. Each case stores evidence, findings, and recommendations. The system deterministically joins and correlates this data, but leaves it to a Managed Defense Analyst to confirm the actual scope. Over time, a case can connect network, application, and Zero Trust evidence together, while tracking the evidence source for additional context and reference.
From evidence to decision
Before analysis begins, the system creates a versioned evidence package containing the subject, scope, time anchor, admitted evidence, policy versions, sources, and coverage gaps. Specialists must cite items in that package. Application code verifies that every citation exists, belongs to the investigation, and supports the attached claim. Invalid findings are corrected or recorded as limitations.
Clef is used a second time to score the evidence. Is the collected evidence sufficient for a decision? Does any collected evidence contradict? Based on this evidence, Clef selects from a deterministically reduced list of attack classifications and dispositions.
Cloudflare's developer platform executes this process. Application code on Workers admits evidence and validates results; Workflows coordinates each stage and saves completed work before the next begins, so a failed stage reuses evidence and findings that already passed validation instead of starting over. D1 maintains investigation and advisory state, R2 holds bounded context and evidence artifacts. Case-chat state persists in Durable Objects, uses Flue, and is enriched with AI Search.
Finally, an LLM-powered agent generates an advisory report using terminology that Managed Defense Analysts already use: affected surface, enforcement outcome, relevant controls, and next step. Managed Defense Analysts can review evidence, investigate further, revise the recommendation, or combine alerts into a case. Application code fixes the customer scope before any model sees results, and gives each specialist only the evidence it needs. The model never receives authority to cross tenant boundaries or act for the Managed Defense Analysts.
Handling incomplete evidence
At network scale, a source will occasionally fail. A comparison may time out, metadata may be missing, or a threat intelligence lookup may return no match. The system preserves evidence already collected and records the gap.
The advisory distinguishes three states:
- Not checked
- Checked, with no matching result
- Checked, with evidence supporting absence
If global telemetry is unavailable, the system can describe what is unusual for the customer but cannot say whether the pattern is widespread. When evidence is insufficient, it makes no classification or disposition recommendation.
Remediation
A useful recommendation should lead to a solution, rather than a ticket. The advisory might suggest a rate limiting rule for an abusive path, a WAF custom rule for a signature, or a DDoS protection change. For fully managed customers, Managed Defense Analysts can apply the suggested rules; other customers will receive their recommendations in the dashboard and through their chosen alert path.
Ultimately, the Managed Defense Analyst remains responsible for the decision and any mitigation. Each alert and case includes the evidence behind the AI agent's recommendation, which empowers the Managed Defense Analyst to reach a conclusion by accepting or updating the AI agent's advice.
What comes next
Managed Defense Analysts retain responsibility for judgment. The AI agent harness handles more of the repetitive work: assembling investigations, connecting related events, and displaying the evidence behind each recommendation. Over the next few quarters, Cloudflare plans to add a Custom Managed level with more flexibility for each organization.
Cloudflare also plans to explore continuous AI agents that monitor Cloudflare traffic and surface patterns that fixed rules and thresholds may miss. The early beta is available in Cloudflare Managed Defense for eligible application-security alerts and cases. Customers already using Cloudflare WAF, DDoS protection, Magic Transit, or another supported product should contact their enterprise account team about adding Managed Defense.