Cisco is urging customers to apply updates for a critical zero-day vulnerability in its Secure Email Gateway that has been targeted by attackers in the wild. The company disclosed the flaw in a security advisory released Monday, noting that exploitation began in September 2026.
The vulnerability, designated CVE-2026-76461, resides in the email parsing functionality of Cisco AsyncOS Software running on Secure Email Gateway appliances. Both virtual and physical deployments are vulnerable regardless of how they are configured.
An attacker with no credentials can leverage this flaw remotely to achieve command execution at the root level on the underlying operating system. According to Cisco, "This vulnerability is due to insufficient validation in the email parsing logic. An attacker could exploit this vulnerability by sending a crafted email message that contains malicious SQL statements through an affected device. A successful exploit could allow the attacker to execute arbitrary SQL statements, leading to command execution with root privileges on the underlying operating system."
Cisco has provided indicators of compromise and recommends that defenders examine mail_logs on each cluster device for unusual SQL statements. Network and firewall logs should also be reviewed for anomalous activity such as transfers to or from suspicious external addresses, as attackers may attempt to erase traces of their presence.
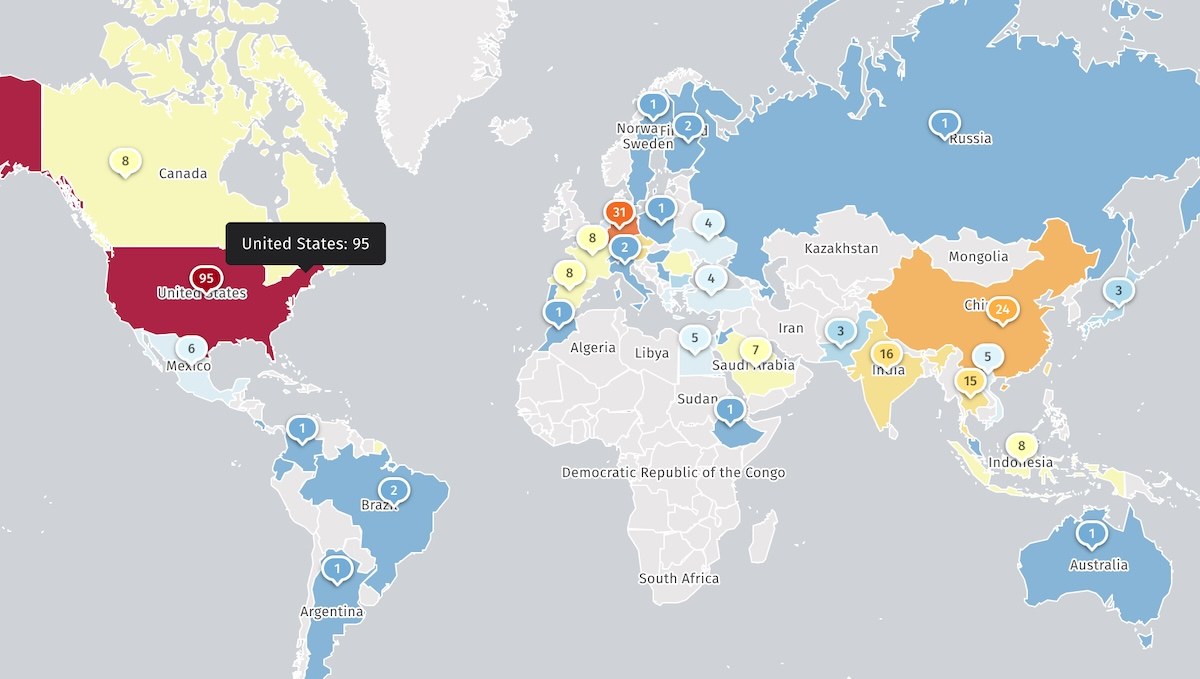
Shadowserver, an internet security research organization, has identified more than 400 Cisco Secure Email Gateway appliances online, though the count does not distinguish between honeypots or systems already patched.
The Cybersecurity and Infrastructure Security Agency added CVE-2026-76461 to its Known Exploited Vulnerabilities catalog on Monday and mandated that federal agencies remediate the issue within three days, setting a deadline of September 17.
Alongside the zero-day patch, Cisco released fixes for four additional critical vulnerabilities affecting Secure Email Gateway and Secure Email and Web Manager systems: CVE-2026-76440, CVE-2026-76441, CVE-2026-20353, and CVE-2026-76443. Cisco stated that it has found no evidence these flaws are being exploited in active attacks.
This incident follows a pattern of vulnerabilities in Cisco's email security products. In January, the company patched a maximum-severity flaw in AsyncOS (CVE-2025-20393) that had been exploited since November 2025 against SEG and SEWM devices.
More broadly, Cisco recently disclosed that ransomware operators and state-sponsored groups have weaponized two previously patched vulnerabilities in its Secure Firewall Management Center. Since November 2021, CISA has cataloged 98 Cisco vulnerabilities as actively exploited, with seven of them leveraged by ransomware crews.