Google has issued an urgent security update to address a Chrome vulnerability that attackers are actively exploiting in real-world attacks. This represents the eighth zero-day flaw the company has patched since the beginning of the year.
In a Monday advisory, Google stated: "Google is aware that an exploit for CVE-2026-125350 exists in the wild." The vulnerability stems from a Use-After-Free (UAF) weakness in Chrome's XML component. The flaw occurs when the browser's XML parser processes data, removes an object from memory, but leaves the pointer to that object intact.

Threat actors can leverage this high-severity memory corruption issue by triggering the browser to access the freed memory space, allowing them to reshape memory and inject malicious code. Google has confirmed active exploitation but has withheld specifics about the attacks themselves.
The company explained its disclosure approach: "Access to bug details and links may be kept restricted until a majority of users are updated with a fix. We will also retain restrictions if the bug exists in a third party library that other projects similarly depend on, but haven't yet fixed."
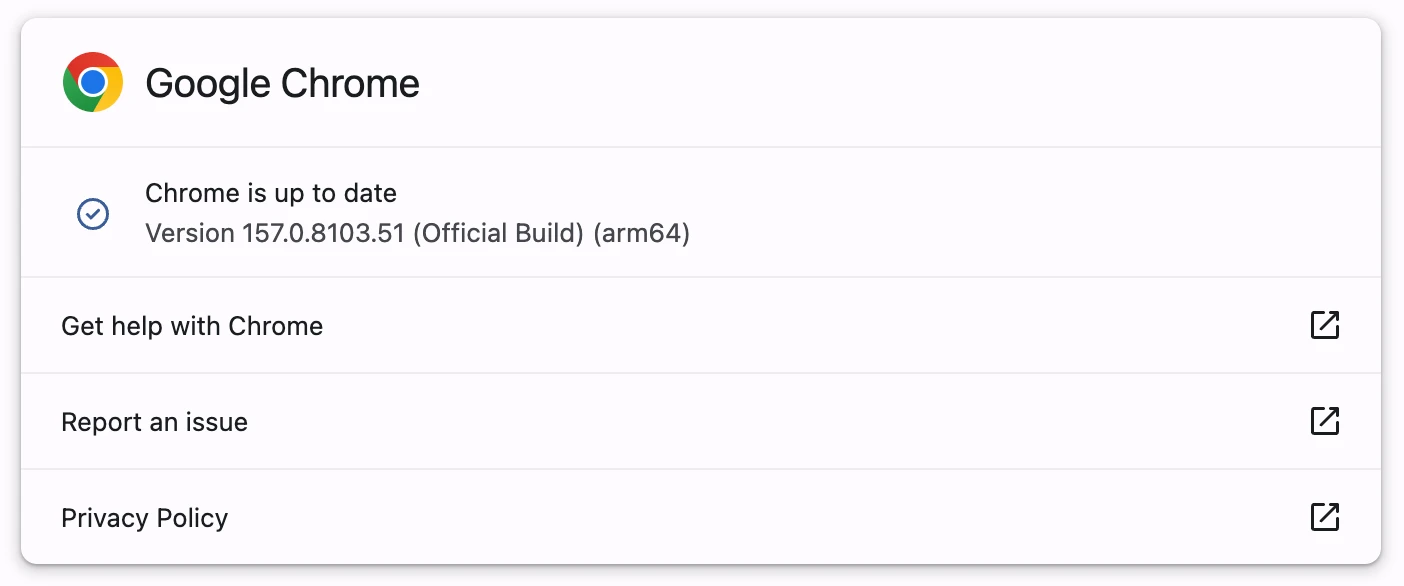
The fix is now available for the Stable Desktop channel across Windows, macOS (157.0.8103.50/.51), and Linux (157.0.8103.50). Google notes that full rollout may take several days or weeks, though the update was immediately available when checked today. Users can manually update or allow Chrome to install the patch automatically at the next browser launch.
Seven Earlier Zero-Days Patched in 2026
The current vulnerability joins a growing list of exploited flaws that Google has remedied throughout the year:
- An iterator invalidation bug (CVE-2026-2441) in CSSFontFeatureValuesMap, Chrome's CSS font feature implementation, addressed in mid-February.
- Two zero-days patched in March: an out-of-bounds write in the Skia 2D graphics library (CVE-2026-3909) and an inappropriate implementation flaw in the V8 JavaScript and WebAssembly engine (CVE-2026-3910).
- A use-after-free weakness in Dawn (CVE-2026-5281), the cross-platform WebGPU standard implementation used by Chromium, fixed in April.
- An out-of-bounds read and write vulnerability in V8 (CVE-2026-11645), exploited in attacks and patched in June.
- Out-of-bounds write (CVE-2026-87491) and type confusion (CVE-2026-85046) flaws in V8, both resolved in September.
Many of these discoveries have been reported by Google's Threat Analysis Group (TAG), which monitors zero-day exploits deployed in spyware campaigns.