Multiple Atlassian product families are facing active exploitation of CVE-2026-21589, a critical flaw that permits unauthenticated attackers to retrieve files from the application's web root directory when the exact file name and path are known. Previdian's security team observed attack attempts on its honeypot infrastructure shortly after a detailed technical breakdown became available.
The vulnerability, disclosed Monday, impacts self-hosted deployments across eight Atlassian offerings: Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye. Atlassian urged administrators of self-hosted instances to deploy patches immediately, while acknowledging it cannot verify whether specific customer environments have been targeted.
Exploitation path through Crowd integration
Following Atlassian's disclosure, offensive security firm watchTowr released technical analysis demonstrating how CVE-2026-21589 could escalate to administrator-level compromise in Jira, Confluence, and Bitbucket installations that integrate with Atlassian Crowd, the company's centralized identity and access management platform.
The underlying issue stems from a shared web-resource library that translates double colons :: into forward slashes /. Attackers leverage this conversion to craft directory-traversal requests through plugin resource endpoints, bypassing authentication controls to access protected files. While watchTowr confirmed file reads across Jira, Confluence, and Bitbucket, their technique remained confined within the Tomcat application context.
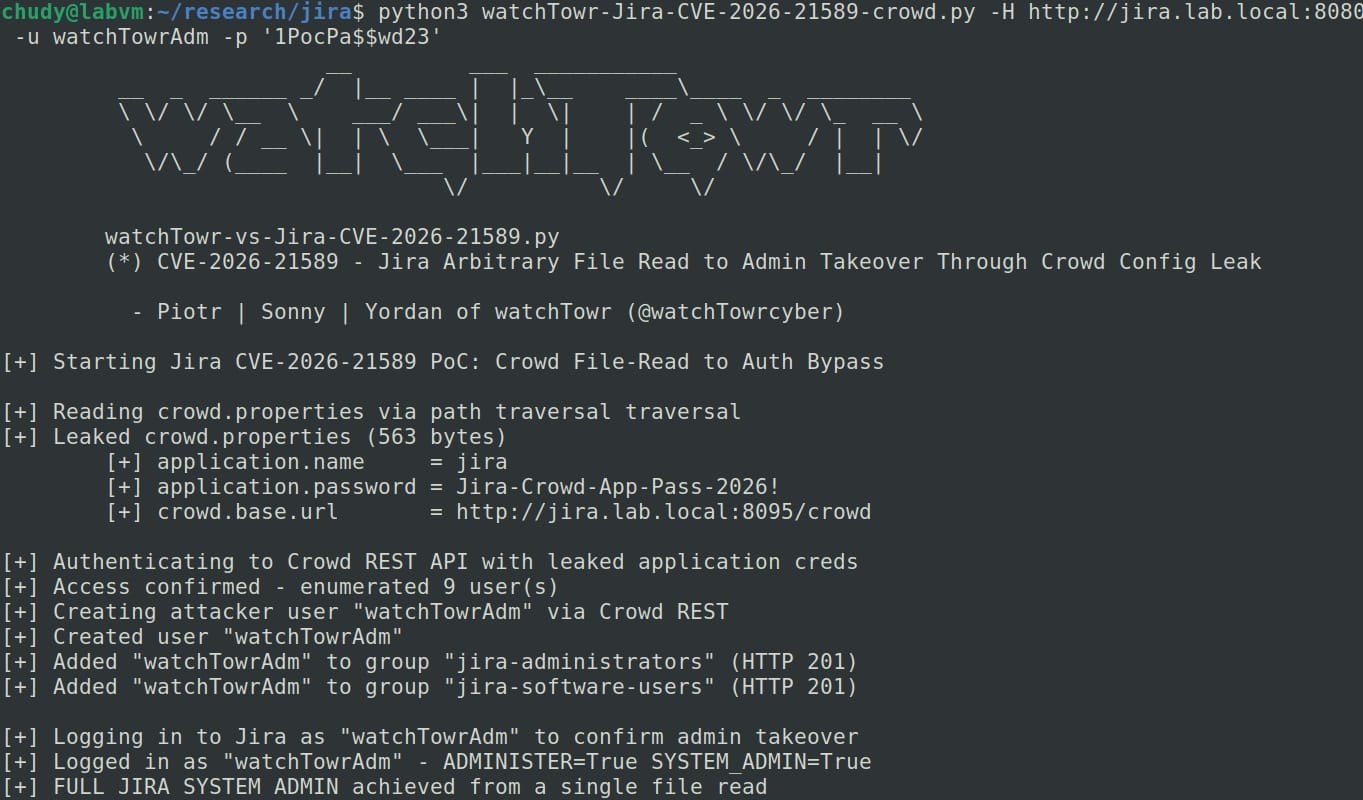
In Crowd-integrated Jira setups, the attack chain becomes more dangerous. Attackers can extract plaintext application credentials stored in WEB-INF/classes/crowd.properties, then leverage those credentials through Crowd's API to establish a Jira administrator account—provided Crowd is network-accessible and the application holds sufficient permissions. The researchers note that IP allowlisting would substantially complicate this attack vector.
[An attacker] would need to pivot through arbitrary machines or use SSRF-like capabilities of Jira, Confluence, or Bitbucket to reach Crowd directly
watchTowr researchers
Credentials extracted from crowd.properties grant full administrator rights to the Crowd identity system, enabling attackers to create accounts and alter access permissions across connected applications.
Rapid weaponization and scanning automation
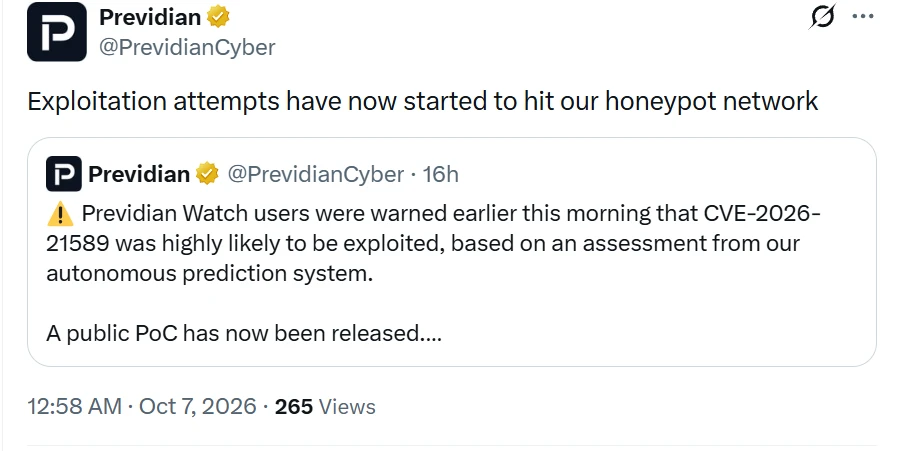
The technical depth of watchTowr's analysis proved sufficient for threat actors to identify and probe vulnerable instances. Previdian detected exploitation attempts within two hours of the public proof-of-concept release.
Within two hours of watchTowr publishing its technical research and public PoC for CVE-2026-21589, Previdian's honeypot network began observing exploitation attempts targeting the vulnerability
Ryan Dewhurst, Previdian
A Nuclei template for automated scanning has since become available, significantly lowering the barrier for threat actors to discover exposed vulnerable systems. Previdian has tracked attack traffic originating from three IP addresses: 38.60.157[.]86, 146.70.187[.]234, and 159.26.119[.]225, and recommends blocking them.
Dewhurst anticipates exploitation activity will accelerate substantially in coming days and weeks, driven by the combination of public proof-of-concept code, readily available automated scanning templates, and the wide range of Atlassian products affected.
Mitigation and remediation steps
System administrators should prioritize applying available security patches immediately. For environments where immediate patching is not feasible, Atlassian recommends several mitigation strategies:
- Restrict external network access to affected systems
- Deploy a web application firewall (WAF) or proxy rule to block specified traversal patterns across all affected products
- Apply Tomcat RewriteValve rules for Confluence, JSM, Jira, Bamboo, and Crowd
- Implement URL rewrite rules for Bitbucket
Atlassian's security bulletin contains comprehensive details on patched versions and mitigation procedures. watchTowr has released a free scanning utility to help administrators assess whether their instances remain vulnerable to CVE-2026-21589.